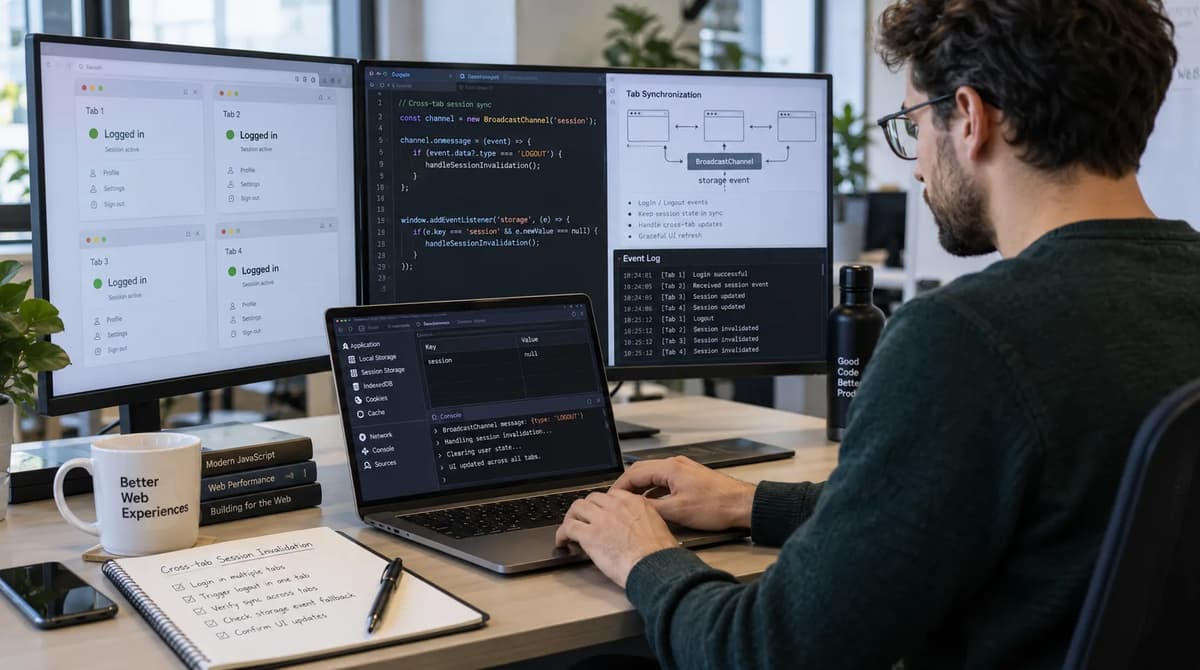
Cross-tab authentication UX looks deceptively simple: a user signs out in Tab A, so Tabs B and C should stop presenting an authenticated interface. The difficult part is not calling BroadcastChannel.postMessage() or writing a value to localStorage. The difficult part is proving that the application converges correctly when tabs reload, close, sleep, miss notifications, perform simultaneous writes, or receive the same logical state change through more than one transport.
This acceptance playbook treats BroadcastChannel session invalidation, storage event cross tab logout, and browser tab session synchronization as state-reconciliation problems rather than message-delivery demos. It deliberately avoids repeating IndexedDB schema-upgrade mechanics, service-worker update lifecycles, and generic Web Storage tutorials.
The browser platform gives applications useful communication primitives, but it does not turn those primitives into an authentication authority. BroadcastChannel communicates among eligible contexts with matching channel and storage-key boundaries; storage events communicate mutations to other relevant Storage objects. Neither mechanism proves that an application server has invalidated credentials.
The primary references for this playbook are MDN’s Broadcast Channel API (last modified February 21, 2025; accessed September 22, 2026), MDN’s BroadcastChannel: postMessage() (last modified September 6, 2025; accessed September 22, 2026), MDN’s Window: storage event (last modified August 21, 2026; accessed September 22, 2026), the WHATWG broadcasting algorithm (Living Standard updated September 21, 2026; accessed September 22, 2026), the WHATWG Web storage section (Living Standard updated September 21, 2026; accessed September 22, 2026), and MDN’s Document: visibilitychange event (last modified February 20, 2026; accessed September 22, 2026).
Why cross-tab session synchronization needs explicit acceptance criteria
A successful “logout appeared in my second tab” demo proves much less than teams often assume. It demonstrates one transport path under one timing arrangement. It does not prove that a newly opened tab reconstructs the correct state, that a tab reloading during logout converges, that duplicate notifications are harmless, or that a server will reject requests made with a revoked session.
The distinction matters because browser messaging is asynchronous. The BroadcastChannel algorithm queues a task for each eligible destination and explicitly removes the sending channel from the destination list. The Web Storage algorithm likewise queues tasks for remote storage objects rather than synchronously invoking every open page.
The acceptance target therefore should be convergence, not “every tab always observed every event.” A tab that was closed during logout cannot receive an ephemeral BroadcastChannel message. A future tab must instead derive the current state from something authoritative enough to reconstruct the UI. That durable browser state still must not be confused with the application server’s authorization decision.
Refonte Learning’s recent IndexedDB multitab recovery article is a useful contrast because it also tests client-side state across tabs, but its blocked-upgrade and schema-lifecycle mechanics are intentionally outside this playbook.
Acceptance dimension | Weak test | Required acceptance question |
Delivery | “Tab B received one message” | Do all eligible active receivers process the change? |
Convergence | “An event fired” | Do all surviving/reopened tabs reach the intended state? |
Idempotency | “One event occurred” | Is duplicate processing harmless? |
Race handling | “Normal reload works” | What happens when reload overlaps publication? |
Stale-tab recovery | “Existing tabs updated” | Does a later tab reconstruct the latest state without past events? |
Concurrency | “Only one writer tested” | What happens when two tabs change state concurrently? |
Failure handling | “Channel exists” | Can a closed/unavailable receiver recover afterward? |
Authorization | “UI says logged out” | Does the simulated server separately reject revoked sessions? |
Evidence | Console screenshot | Are tab ID, event ID, revision, timestamps, before/after state, and action recorded? |
For an active-tab test, teams may choose a finite harness timeout such as five seconds to decide whether an expected event appeared. That timeout is an application test criterion, not a platform guarantee. Browser scheduling, lifecycle transitions, and future implementations must not be represented as providing a universal five-second delivery SLA.
Define authentication truth versus browser UI synchronization
The playbook needs three state layers. First is server authorization state: whether the backend accepts a synthetic session such as SYN-A. Second is durable browser synchronization state, for example a deliberately non-secret localStorage record saying the current UI epoch is anonymous at revision 18. Third is each tab’s in-memory rendered state.
Only the first layer decides whether protected server resources should be available. Browser state can make the interface react quickly, but any same-origin JavaScript capable of changing the selected local storage key can alter that local representation. The HTML Standard also warns that persistent client storage can contain sensitive data; this lab avoids that risk by storing only synthetic identifiers and test metadata.
State layer | Example | Authority for | Must never be treated as |
Synthetic server registry | SYN-A → revoked | Mock API authorization result | Browser notification state |
Durable browser state | {revision: 18, | Cross-load UI reconciliation | Proof of credential revocation |
Broadcast message | LOGOUT, revision 18 | Fast invalidation hint | Durable history |
storage event | New auth-state value | Notification that storage changed | Server acknowledgment |
In-memory tab state | “signed-out screen” | Current rendering | Authentication truth |
An appropriate test model is:
serverTruth(sessionId)
        |
        | simulated API check
        v
authorization result

durableBrowserState <---- state mutation
        ^                       |
        | reconciliation        +---- BroadcastChannel hint
        |                       |
tab A UI   tab B UI   tab C UI <-+---- storage event
The acceptance invariant is not “all three arrows fire.” It is: after a completed logical state change and required reconciliation point, each available tab presents state no newer than the authoritative application decision and does not resurrect an older accepted session merely because a message was missed.
That wording leaves room for architecture. A real application might use a backend session endpoint as its ultimate reconciliation source rather than a browser record. The laboratory can still use durable fake state because its purpose is to validate browser races without touching real credentials.
Build a disposable multi-tab test harness
Serve one disposable application from localhost:<port> and open two to five tabs from exactly that origin. Do not use a real identity provider, customer account, OAuth token, refresh token, API key, or production cookie. Create fake session labels such as SYN-A and SYN-B; they must have no validity outside the test process.
The page should display its tab ID, current local state, durable-state revision, channel status, last reconciliation cause, and an append-only event log. This is a frontend reliability laboratory, not a replacement for broader browser engineering material such as Refonte Learning’s front-end development guide.
Use a second Refonte resource only to preserve scope: its frontend-framework discussion mentioning progressive web apps provides broader PWA context, while this experiment intentionally excludes service-worker installation, activation, cache replacement, and controller lifecycle testing.
Harness component | Recommended synthetic design | Evidence to expose |
Tab identity | Random crypto.randomUUID() on page creation | tabId |
Durable key | rl.lab.authState | Raw value + parsed value |
Channel | new BroadcastChannel( | Open/closed status |
Session IDs | SYN-A, SYN-B | Never real credentials |
Revision | Integer or server-issued epoch | Previous/current revision |
Event identity | Random UUID | eventId |
Local state | anonymous/authenticated test enum | Before/after snapshots |
Mock server | Local in-memory session registry | HTTP status + server state |
Event log | Visible <pre>/table and machine-readable array | Complete trace |
A useful durable record is deliberately boring:
{
  schema: 1,
  revision: 18,
  status: "anonymous",
  sessionId: null,
  writerTabId: "tab-b"
}
A useful transport envelope is separate:{
protocol: 1,
eventId: "synthetic-uuid",
type: "LOGOUT",
revision: 18,
writerTabId: "tab-b",
sentAt: Date.now()
}Install listeners before the first reconciliation read. Record both Date.now() and a per-tab sequence number. performance.now() can help measure intervals inside one tab, but cross-tab correctness should not depend on comparing independent monotonic clocks.
Mandatory log field | Purpose |
Wall-clock timestamp | Human trace correlation |
Per-tab sequence | Definite local processing order |
Tab ID | Sender/receiver attribution |
Transport | broadcast, storage, bootstrap, visibility, server |
Message type | Logout, login replacement, reconciliation |
Event ID | Duplicate detection |
Revision | Stale-update rejection |
State before | Debugging |
State after | Convergence proof |
Reconciliation action | Applied, ignored, re-read, rejected |
Validation result | Malformed payload handling |
Validate BroadcastChannel message semantics
MDN describes BroadcastChannel as communication among browsing contexts participating in a named channel, subject to origin/storage-partition boundaries. The current HTML Standard’s support rendering reports BroadcastChannel in current engines, with desktop support entries beginning at Firefox 38, Safari 15.4, Chrome 54, and Edge 79. These tables support a broad compatibility baseline, not a promise about every embedded, managed, privacy-restricted, or future browser configuration.
BroadcastChannel versus storage event boundaries
BroadcastChannel is a message transport. A storage event is a notification resulting from a storage mutation. A BroadcastChannel message need not alter persistent state, while localStorage.setItem() may cause other contexts to observe the changed durable value even if no BroadcastChannel exists.
The BroadcastChannel algorithm selects destinations that are eligible for messaging, have an equal relevant storage key, and use the same channel name. It then removes the sending channel from those destinations. MDN additionally notes storage-partition effects: technically same-origin contexts in different top-level-site partitions may not necessarily communicate.
Case | BroadcastChannel expectation | Storage-event expectation |
Same active origin, same channel | Candidate receiver | Independent of channel |
Sender itself | Not destination | No storage event for own write |
Different channel name | No BC delivery | Unaffected |
Different origin | No matching BC group | No shared localStorage area |
Closed BC receiver | Delivery task can abort | Storage listener independent |
Tab opened after message | No historical replay | Can read current durable state |
Same payload posted twice | Two message operations possible | Same-value setItem() may produce no mutation event |
Persistent recovery | None inherent | Current stored value can be reread |
The standard also requires structured serialization. MDN documents DataCloneError when input cannot be serialized and InvalidStateError when postMessage() is called on an already closed BroadcastChannel. Receivers should nevertheless validate the application-level schema because successful structured cloning does not establish that a payload contains a recognized protocol version, type, revision, or safe state transition.
Proposed experiment: open A, B, and C. Post PING/E1 from A. Require B and C to log the message exactly as received while A records only its explicit send operation, not a self-delivered message event. Then close C’s BroadcastChannel and send PING/E2; C must not be relied upon to receive it. The standard explicitly says a destination task aborts if its channel’s closed flag is true when that task executes.
Validate storage event semantics and key filtering
MDN states that the Window storage event fires when another document sharing the relevant storage area updates it; it does not fire in the window that made the change. For localStorage, that includes other same-origin browsing contexts such as tabs. For sessionStorage, propagation is restricted to same-origin contexts within the same top-level browsing context, so it is not the general cross-tab mechanism needed here.
The tab that changes localStorage is not the same event recipient set
This difference should shape the application architecture. The writing tab must update its own in-memory UI as part of the local action; it should not sit waiting for a storage event that is not intended to return to it. Other tabs process the remote event and then reconcile.
The normative Web Storage algorithm explicitly excludes the source Storage object while selecting remote objects. It also supplies key, oldValue, newValue, source URL, and the corresponding storage area in the queued StorageEvent.
Mutation from Tab A | Tab A | Tab B/C | Acceptance |
Set auth key to new value | Apply directly | storage event expected when eligible | Same final state |
Set identical string value | Direct call succeeds | No change broadcast required | Never depend on “heartbeat” |
Remove existing auth key | Apply directly | Remote event with newValue === null | Defined anonymous handling |
Remove nonexistent key | No effective mutation | No required event | No state change |
clear() non-empty storage | Direct clear | Event with null key/value fields | Handler must treat carefully |
Unrelated key changes | No auth change | Event may arrive | Auth handler ignores key |
Invalid JSON in auth key | Writer records fault | Receiver rejects/reconciles | No arbitrary UI mutation |
A particularly useful negative test follows directly from the specification: setItem() returns without broadcasting when the existing value equals the value being written. Repeatedly assigning "logged-out" therefore must not be designed as an event-generation trick.
Filter on the exact synchronization key before parsing. A busy same-origin application may use localStorage for unrelated preferences or development state. Receiving a storage event is not equivalent to receiving an authentication message.
Proposed experiment: write rl.lab.preference = "dense" from A and verify B records the storage event but performs no authentication transition. Next update rl.lab.authState, verify B and C reconcile, and verify A receives no corresponding storage event. Repeat the identical serialized auth value and require no receiver logic to depend on a second event.
Compare delivery, ordering, and duplicate-handling assumptions
The most dangerous acceptance tests quietly turn observed timing into an undocumented guarantee. The BroadcastChannel specification imposes a creation-order constraint for destinations sharing the same relevant agent, but explicitly says this does not define a complete ordering and allows user-agent-defined sorting within the remaining freedom. Applications should therefore avoid basing session correctness on a guessed global ordering among multiple tabs.
Web Storage has a different mechanism: each remote event is queued as a task on the DOM manipulation task source. The specification additionally warns authors not to assume a locking mechanism around shared localStorage state in multiprocess user agents. It gives the classic example of concurrent read-increment-write operations producing duplicate supposedly unique identifiers.
Assumption | Accept? | Safer design |
“Broadcast means immediate” | No | Treat delivery as asynchronous |
“Every receiver sees events at identical time” | No | Test final convergence |
“Arrival timestamp decides truth” | No | Use authoritative revision/epoch |
“A duplicated logical update is impossible” | No | Require idempotency |
“BC and storage arriving both means two state changes” | No | Deduplicate logical transition |
“LocalStorage provides a lock” | No | Avoid client-side race-dependent authority |
“One browser run proves universal ordering” | No | Run engine-specific matrices |
A practical application may deliberately publish the same logical transition through two routes: first update durable state, then send a BroadcastChannel hint. That creates an intentional duplicate opportunity. A receiving tab could see a storage notification, reconcile revision 18, and later receive a BroadcastChannel LOGOUT also referring to revision 18.
The correct reaction is not a second logout side effect. Compare a revision or epoch, optionally keep a bounded set of processed event IDs, and make applying the same desired state safe. Do not rely only on event IDs if the storage route and messaging route do not naturally share one ID.
Engineering inference: the most robust model is “messages prompt reconciliation” rather than “messages themselves are authentication truth.” This follows from BroadcastChannel’s lack of historical replay, Web Storage’s persistent current value, and the standards’ asynchronous task model.
Test logout propagation across multiple tabs
Start with three tabs in synthetic authenticated state at durable revision 10 and fake session SYN-A. The sender’s logout action should create revision 11, store the anonymous durable state, update its own UI, and optionally publish a BroadcastChannel LOGOUT hint carrying revision 11.
The receivers may reach revision 11 because of either transport. The acceptance criterion is not that a particular callback always wins the race. It is that each eligible active receiver ends at revision 11 and that repeated processing cannot turn an anonymous state back into revision 10.
Step | A sender | B receiver | C receiver | Evidence |
Initial | Auth SYN-A, r10 | Auth SYN-A, r10 | Auth SYN-A, r10 | Baseline snapshots |
Durable write | Anonymous r11 | Pending | Pending | Storage before/after |
Self-apply | Anonymous r11 | Not applicable | Not applicable | Sender reconcile log |
BC publish | Send LOGOUT/r11 | Candidate receiver | Candidate receiver | Event ID |
Remote handling | Not applicable | Reconcile ≥r11 | Reconcile ≥r11 | Transport + revision |
Duplicate path | Not applicable | No second semantic logout | Same | Idempotency evidence |
End | Anonymous r11 | Anonymous r11 | Anonymous r11 | Final snapshots |
Logout propagation is not authorization revocation
A green row in that matrix demonstrates browser-side synchronization only. BroadcastChannel has no protocol operation that tells an authentication server to invalidate a session, and a localStorage mutation is a browser-side state operation. The browser standards define messaging and storage behavior, not application authentication revocation.
The acceptance report must therefore use language such as “logout UI propagated to Tabs B and C” or “browser state converged to anonymous revision 11.” It must not say “the session was revoked everywhere” unless the separate server simulation has actually marked SYN-A revoked and subsequent protected requests are rejected.
Test sender closure as a distinct race. Have A publish, immediately close A, and observe B/C. The experiment is worth running, but its result cannot be upgraded into a universal statement that “closing a sending tab never affects delivery.” The specification’s algorithm identifies eligible destinations and queues tasks, while lifecycle timing and the exact point at which a navigation or close operation changes eligibility are precisely why the race belongs in the matrix.
Logout acceptance gate | Pass condition |
Sender self-state | Anonymous without waiting for own event |
Two to four active receivers | Eventually anonymous within configured lab timeout |
Duplicate transport | One logical transition |
Old revision received later | Ignored |
Sender closes immediately | Result recorded, no universal guarantee inferred |
Server remains active | Report explicitly says browser-only synchronization |
Server becomes revoked | Separate protected request returns simulated rejection |
Test login replacement and stale-tab reconciliation
Logout is not the only session transition that needs cross-tab semantics. Suppose Tab A is showing SYN-A while another workflow establishes synthetic SYN-B. That should be represented as a session replacement, not merely “authenticated = true.” Otherwise a stale tab can remain logically attached to the wrong session epoch while still rendering an authenticated shell.
Use revisions or server-issued epochs. A replacement from SYN-A/r20 to SYN-B/r21 should invalidate UI derived from SYN-A, clear session-scoped in-memory caches, and reconstruct the visible identity from the new synthetic state.
Scenario | Initial | Durable state | Required result |
Login from anonymous | anon r20 | SYN-A r21 | All reconciled tabs use r21 |
Account/session replacement | SYN-A r21 | SYN-B r22 | No tab retains A-specific UI |
Old logout arrives afterward | SYN-B r22 | Still r22 | Ignore stale r21 event |
New tab opens after replacement | No event history | Reads r22 | Starts as SYN-B |
Old tab resumes | Memory says r21 | Durable/server says r22 | Reconcile to r22 |
Malformed replacement message | r22 | r22 unchanged | Reject payload |
The stale-new-tab case is essential. Open Tab D after the logout or login-replacement event occurred. D could not have received an earlier BroadcastChannel message because it did not yet have a participating channel. The acceptance requirement is consequently bootstrap reconciliation from current durable or server state, not retroactive messaging.
Message schema validation should happen before state mutation. Require an expected protocol version, finite revision, recognized event type, and correctly shaped synthetic session field. A structurally cloneable value such as {nonsense: true} can travel over BroadcastChannel successfully; structured cloning and application-protocol validation solve different problems. MDN expressly notes that the application’s messaging protocol is not defined by BroadcastChannel itself.
Malformed case | Expected action |
Missing protocol | Reject |
Unknown protocol version | Reject/reconcile |
Unknown message type | Ignore + log |
Missing revision | Reject |
Revision wrong type | Reject |
Invalid session-state enum | Reject |
Valid envelope, stale revision | Ignore as stale |
Valid newer hint | Reconcile before trusting UI |
Exercise reload, close, background, and delayed-tab races
Page lifecycle is where simplistic cross-tab tests usually break down. BroadcastChannel eligibility for a Window requires its associated document to be fully active. Storage events have a different rule: the Web Storage specification says a queued event’s document need not currently be fully active and that events on such objects are ignored by the event loop until the document becomes fully active again.
MDN documents visibilitychange for transitions such as switching tabs, navigating, minimizing, and moving away from the browser on mobile. It describes transition to hidden as the last reliably observable visibility transition for page-end work. That makes visibility a useful test trigger for reconciliation, but it does not turn visibilitychange into a guaranteed session-message delivery mechanism.
Race | Action | Risk | Required recovery |
Receiver reloads | B reloads while A logs out | Listener gap/new document | Bootstrap durable reconciliation |
Sender reloads | A changes state then navigates | Publication/lifecycle timing | Durable state survives |
Sender closes | A posts then closes | Timing uncertainty | Record receiver outcome; durable fallback |
Receiver closes | C absent during event | Guaranteed missed live processing | Reopen and bootstrap |
BC explicitly closes | C calls close() | BC task can abort | Storage/bootstrap path |
Background tab | B hidden | Scheduling delay | Reconcile on visibility/focus |
Long-delayed tab | B untouched for minutes | Stale memory | Re-read authoritative state |
New tab after event | D opens afterward | No event history | Bootstrap current state |
Reload race between initial state and incoming event
A subtle startup error is to read state, render the UI, and only afterward attach event listeners. Another tab can update state between those operations. The safer sequence is: install transport listeners, read the current durable state, apply it using revision rules, and treat subsequent notifications as reconciliation triggers.
That sequence does not require assuming which asynchronous callback wins. If the state changes just before the read, the read can observe it. If it changes after the listener is installed, the tab has a route to learn about the mutation. A final reconciliation after initialization is reasonable where the application’s real authoritative source is remote.
const channel = new BroadcastChannel("rl.lab.session");

channel.addEventListener("message", handleHint);
window.addEventListener("storage", handleStorage);

// Listener installation precedes bootstrap reconciliation.
reconcileFromDurableState("bootstrap");

document.addEventListener("visibilitychange", () => {
  if (document.visibilityState === "visible") {
    reconcileFromDurableState("became-visible");
  }
});
Duplicate and out-of-order messages
Do not write a handler that means “whatever arrived last wins.” Arrival order and truth order are different concepts. A delayed LOGOUT/r41 should not overwrite a later established SYN-B/r42. Conversely, a duplicate LOGIN_REPLACED/r42 should not re-run destructive cache resets twice.
A minimal reconciliation rule is:
if (!valid(message)) return recordRejected(message);
if (message.revision < localState.revision) return recordStale(message);
reconcileFromDurableOrServerState(message.type);
For equal revisions containing different states, do not guess. That indicates a collision, malformed producer logic, or an inadequate revision scheme. Record the conflict and consult the authoritative state.
Race assertion | Evidence required |
Reload cannot resurrect r40 after r41 logout | Bootstrap log + final state |
Hidden tab eventually catches current state | Visibility/reconcile trace |
Closed tab needs no past message | Reopen bootstrap trace |
Older event arrives after newer revision | “ignored stale” trace |
Same revision, different payloads | Conflict trace, no arbitrary winner |
Duplicate logical event | One semantic side effect |
Test simultaneous updates and last-writer assumptions
The HTML Standard is unusually direct about concurrent Web Storage use: authors are encouraged to assume there is no locking mechanism around shared localStorage state across agent clusters. A read-modify-write operation performed in two windows can therefore collide. That warning makes localStorage a poor place to manufacture security-critical sequence numbers.
Consider Tabs B and C both reading revision 50. B decides logout should become revision 51. C simultaneously decides a new login should become revision 51. If both derive the same next integer locally, two contradictory states can carry the same revision. Whatever value is eventually visible in storage does not magically explain which operation should have been authoritative.
Concurrent case | Bad assumption | Acceptance behavior |
B logout, C login | “Last callback wins” | Use authority-defined epoch |
Both calculate r51 | “Revision is automatically unique” | Detect collision |
Two storage writes | “localStorage serializes application intent” | Do not rely on locking |
BC events cross | “Arrival order equals action order” | Compare authoritative version |
Equal revision/different session | “Pick one” | Conflict + reconciliation |
Server says SYN-A revoked | “Browser state can override it” | Server result wins |
For a pure browser laboratory, one can use a deterministic tuple such as (counter, writerTabId) simply to make experimental ordering reproducible. Production authentication should preferably obtain meaningful session epochs from the application’s authority rather than let independent tabs invent security truth.
Proposed simultaneous-update experiment: initialize A–D at revision 50. Schedule B and C to update from the same baseline as closely together as the harness permits. Record the exact states written, each storage event, each BroadcastChannel hint, and final durable value. Repeat at least 30 times per tested engine.
Do not summarize those repetitions merely as “last writer wins.” Record which operation was last observed in durable state and whether all tabs converged. “Last-writer-wins” is an application policy only if the application defines a trustworthy ordering mechanism; it is not a general authentication guarantee supplied by localStorage.
Evidence field | Example synthetic value |
B intent | LOGOUT |
C intent | LOGIN_REPLACED |
B proposed revision | 51 |
C proposed revision | 51 |
Durable final writer | tab-c |
Collision detected | true |
Reconciliation action | query-authority |
Authorization conclusion | Not derived from write order |
Validate failure behavior when a tab cannot receive the event
A robust synchronization design assumes missed notifications are normal recovery conditions. A tab can be closed, not yet opened, in navigation, have its BroadcastChannel explicitly closed, or otherwise fall outside the receiver set relevant to one transport operation.
BroadcastChannel’s specification is particularly useful here: only eligible destinations are selected, and a queued delivery aborts if the destination channel has been closed by the time its task executes. It follows that “every logical transition must be recoverable without that message” is a stronger application invariant than trying to prove that every message survives every lifecycle race.
Recovery when a tab missed an event
The recovery test should intentionally remove a receiver. Close Tab C completely, perform logout in A, verify B converges, then reopen a new C. The new C did not “catch up” through BroadcastChannel; its success is demonstrated only if bootstrap reconciliation discovers the current anonymous state.
Repeat by closing only C’s BroadcastChannel while leaving the document alive. If storage synchronization remains enabled, C may still learn about the durable mutation via the storage path. Then disable that handler in the test build as well and require explicit reconciliation on focus or a manual “reconcile now” action.
Failure injection | Live event expected? | Recovery acceptance |
Tab closed before update | No | Reopened tab bootstraps current state |
Channel closed | No BC dependency | Storage/server reconciliation |
Tab created after update | No historical BC message | Current state on initialization |
Message malformed | Received but rejected | State unchanged, reconciliation optional |
Unrelated storage event | Received, ignored | Auth state unchanged |
Storage unavailable/policy blocked | Do not assume persistence | Fall back to server/in-memory policy |
Tab returns from long background | Timing uncertain | Reconcile when visible |
Durable record malformed | Cannot safely trust | Fail conservative + query authority |
Web Storage access itself should not be treated as universally infallible. The HTML specification allows storage access to fail under relevant policy decisions and defines SecurityError conditions for the storage getters. An acceptance harness should therefore distinguish “transport unavailable” from “authenticated.”
A safe recovery order is: validate what can be read, compare revisions, avoid resurrecting a prior session, and query the authoritative server where browser state is ambiguous. For the disposable lab, the server is only an in-memory synthetic registry.
Separate browser synchronization from server-side revocation
This is the principal security gate. Browser synchronization answers, “What should other tabs render or clear after learning that session state changed?” Server revocation answers, “Will the authority reject requests associated with a session that is no longer valid?” They are complementary and separately testable.
Build a local mock endpoint whose in-memory registry contains SYN-A: active and SYN-B: active. A protected check for an active synthetic session returns a test success. A /revoke operation changes only the server registry. After revocation, a check for SYN-A returns a synthetic unauthorized result even if a deliberately stale browser tab still renders “authenticated.”
Experiment | Browser UI | Mock server | Correct conclusion |
BC logout only | Anonymous everywhere | SYN-A: active | UI synchronized; server not revoked |
Storage logout only | Anonymous everywhere | SYN-A: active | UI synchronized; server not revoked |
Server revoke only | Stale tab may show auth | SYN-A: revoked | Authorization revoked despite stale UI |
Revoke + browser propagation | Anonymous | Revoked | Both mechanisms succeeded |
Tab misses logout event | Temporarily stale | Revoked | Protected request must still fail |
Forged local “authenticated” record | Auth-looking UI possible | Revoked | Browser representation cannot reauthorize |
This experiment should deliberately create the uncomfortable case: revoke SYN-A at the synthetic server but suppress browser notifications to Tab C. Tab C may still display authenticated local state. Its next protected API check must nevertheless be rejected.
Then perform the reverse experiment. Broadcast LOGOUT and update durable browser state while leaving the synthetic server registry active. Every tab can present an anonymous UI, yet a direct mock-server check still reports the synthetic session active. This is the clearest evidence that propagation does not itself constitute revocation.
Authentication/authorization acceptance should consequently be split into separate assertions: UI synchronization passed, server revocation passed, and integration between revocation and client reconciliation passed. None should be inferred from another.
Security evidence gate | Required artifact |
Browser logout | Per-tab final state |
Server revoke command | Server registry transition |
Post-revoke request | Synthetic 401/denial |
Stale UI test | Tab remains stale before check |
Server supremacy | Request denied despite stale UI |
Browser-only logout test | Server remains explicitly active |
Report wording | No claim equating message delivery with authorization |
Build evidence and acceptance gates across browser engines
Current reference material describes BroadcastChannel as supported in current engines and MDN classifies the API as widely available; the WHATWG developer support rendering lists Firefox 38+, Safari 15.4+, Chrome 54+, and Edge 79+ for BroadcastChannel. Web Storage is also shown as supported across current engines. Those facts justify cross-engine testing; they do not eliminate it.
Test the current stable Chromium family, Firefox, and Safari/WebKit available to the acceptance environment. Record the exact browser version and operating system with every run. Avoid publishing a generic statement such as “all browsers deliver logout reliably” when only one engine/build was executed.
Refonte Learning’s QA automation engineering guide is relevant to turning this matrix into repeatable automated coverage, particularly where browser/environment variation makes one manual green run inadequate evidence.
Test ID | Chromium | Firefox | Safari/WebKit | Required result |
BC-01 sender + 2 receivers | Execute | Execute | Execute | Receivers converge |
BC-02 sender closes immediately | Record | Record | Record | No universal assumption |
ST-01 localStorage recipient set | Execute | Execute | Execute | Sender excluded |
ST-02 identical value | Execute | Execute | Execute | No heartbeat dependency |
ST-03 unrelated key | Execute | Execute | Execute | Ignored by auth logic |
LG-01 logout fan-out | Execute | Execute | Execute | Final anonymous state |
LG-02 login replacement | Execute | Execute | Execute | Old session removed |
RC-01 stale tab opened afterward | Execute | Execute | Execute | Bootstrap catches current state |
RC-02 receiver unavailable | Execute | Execute | Execute | Recovery without past event |
RR-01 reload during change | Repeat | Repeat | Repeat | No stale resurrection |
CO-01 simultaneous writes | Repeat | Repeat | Repeat | Collision safely handled |
ML-01 malformed payload | Execute | Execute | Execute | Rejected |
SR-01 server-only revoke | Execute | Execute | Execute | Request denied despite stale UI |
SR-02 browser-only logout | Execute | Execute | Execute | No revocation claim |
For race-oriented cases, repetitions matter more than a single pass. Run reload, immediate-close, and concurrent-write scenarios many times with controlled jitter. Record the number of iterations rather than presenting the fastest or most convenient run.
Each result needs an evidence classification. Documented means directly supported by the cited standard/reference. Observed means the lab actually produced the result on the named build. Inference means an engineering conclusion derived from documented behavior. Proposed means the test has not yet been executed.
Evidence label | May say | Must not say |
Documented | “The standard excludes the source BC destination” | “Therefore every real race passed” |
Observed | “Firefox X produced this trace in 30/30 runs” | “All browsers guarantee this” |
Engineering inference | “Durable reconciliation reduces missed-message dependence” | “The spec mandates this architecture” |
Proposed experiment | “Acceptance should execute…” | “Testing proved…” |
Blocked experiment | “Environment prevented execution” | Invented pass/fail |
A release gate should fail when evidence is missing for a required supported engine, when a stale session can be resurrected after reconciliation, when a malformed payload directly mutates auth UI, when equal-version conflicts are silently accepted, or when documentation equates browser logout propagation with server authorization revocation.
Cross-engine release gate | Pass | Fail |
Required engines executed | Exact versions logged | Missing target without waiver |
Active fan-out | Converges | Receiver remains stale |
Bootstrap | Current state reconstructed | Requires historical BC message |
Reload race | No older state resurrected | Older state wins |
Duplicate processing | Idempotent | Double destructive action |
Conflict handling | Explicit reconciliation | Arrival order blindly accepted |
Server revocation | Protected call rejected | Browser state reauthorizes |
Evidence language | Qualified and reproducible | Universal claims from one run |
Final acceptance decision and Refonte Learning CTA
Final gate | Accept |
Synthetic localhost-only lab | Required |
No real accounts, providers, tokens, production cookies, or customer data | Required |
BroadcastChannel recipient semantics validated | Required |
storage sender exclusion and key filtering validated | Required |
Logout and login replacement convergence | Required |
Reload, close, background, stale-tab recovery | Required |
Duplicate, stale, conflicting, malformed events handled | Required |
Simultaneous-write assumptions rejected or controlled | Required |
Browser synchronization separated from server authorization | Required |
Server-side revoked simulation independently verified | Required |
Chromium, Firefox, Safari/WebKit evidence recorded | Required |
Unexecuted cases labeled proposed rather than passed | Required |
Build the server-side half of this boundary with Refonte Learning’s APIs Developer program: three months, 10–12 hours per week, with REST, GraphQL, authentication and authorization, database integration, API documentation and testing, error handling and logging, and versioning and deprecation.
Extend that foundation into microservices, performance optimization, and API security without treating BroadcastChannel as an authorization mechanism.