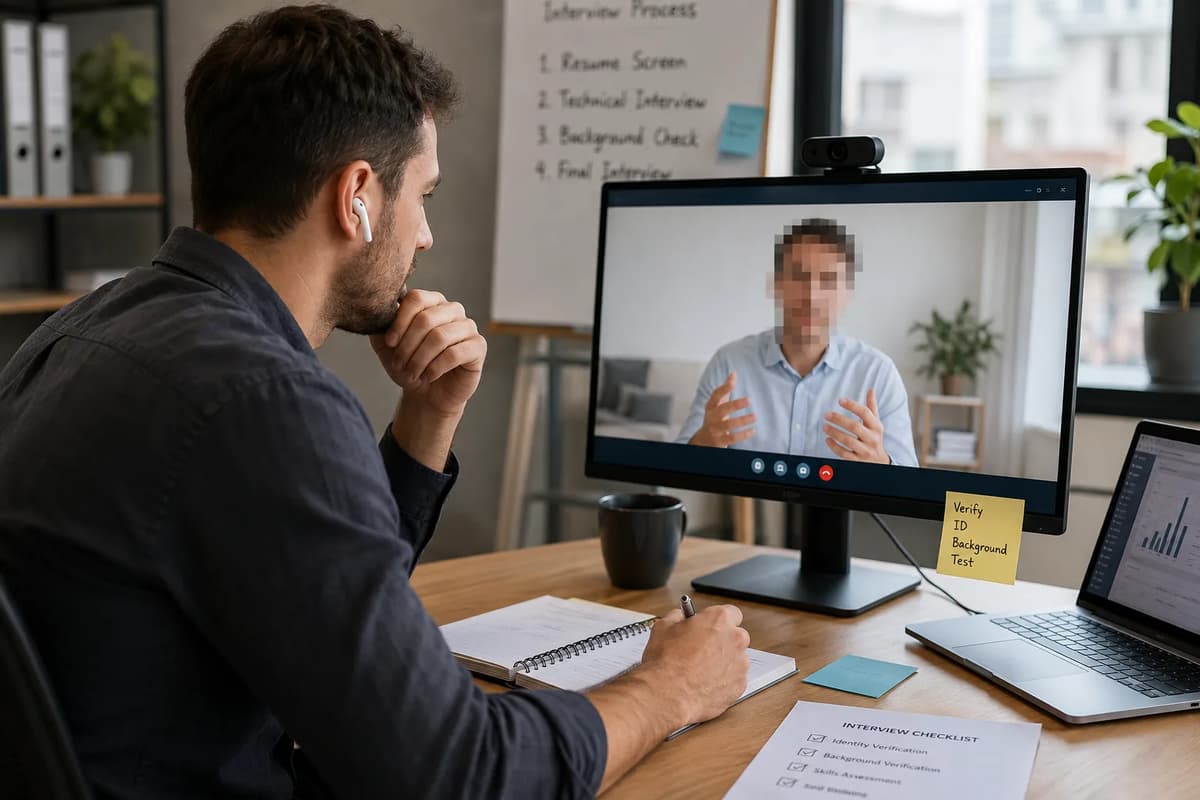
There is a particular kind of uncertainty you only understand after enough years interviewing technical candidates remotely. The candidate is answering a perfectly reasonable architecture question, but the audio arrives a fraction before the mouth moves; the edge of the face looks wrong when they turn; the background seems to shift independently of their shoulders. Your first thought is not “deepfake.” It is usually bandwidth, a bad webcam, aggressive background blur, or another piece of ordinary video-call weirdness.
Then it happens again.
That is the uncomfortable moment recruiting teams are now being forced to design for. The question stops being, “Is this person strong enough for the role?” and becomes, “Am I actually speaking to the person whose identity, résumé, assessment, and future system access I am evaluating?”
That is why AI fake candidate fraud in 2026 deserves to be treated as its own recruiting discipline. Gartner’s published research says 6% of 3,000 candidates surveyed acknowledged participating in interview fraud and predicts that by 2028 one in four candidate profiles worldwide will be fake. Experian separately made “deepfake job candidates” one of the threats in its 2026 Future of Fraud Forecast, putting hiring identity fraud in the same strategic conversation as other technology-enabled fraud risks.
This is different from using AI to make recruiting more efficient. It is hiring fraud prevention: establishing that the same genuine person moves from application to interview to offer to onboarding and, for higher-risk remote roles, into employment.
For recruiters developing those broader process skills, the Refonte Learning Talent Acquisition Program covers structured interviewing, screening, recruitment-process optimization and compliance. Those capabilities form the foundation onto which specialized identity and fraud controls can be layered. The current curriculum does not claim to teach a named deepfake-detection product.
This guide examines how large the problem actually is, what the most credible 2026 evidence shows, how North Korean IT worker fraud schemes penetrate technical hiring, what the new interview fraud detection tools can and cannot establish, and what I would put into a working verification playbook today.
The Moment You Realize the Person on Screen Might Not Be Real
The first operational mistake is treating every suspicious interview as a “deepfake case.” Candidate fraud is a spectrum, and different behavior requires different controls.
Gartner’s own data illustrates why the distinction matters. In a fourth-quarter 2024 survey of 3,290 candidates, 39% said they had used AI during the application process; among those AI users, résumé generation, cover-letter drafting, writing samples and assessment answers were all reported use cases. That is not equivalent to identity fraud, and an employer may expressly permit some of those activities.
At the other end of the spectrum is a completely different threat: a stolen or fabricated identity, a proxy interviewer, a manipulated face or voice, or a candidate who gets through hiring so somebody elsewhere can remotely control the company-issued laptop. Gartner explicitly separates interview impersonation from ordinary AI use: its second-quarter 2025 survey found 6% of 3,000 candidates admitted either pretending to be another person or having somebody else interview for them.
What you are seeing | What it may mean | Appropriate recruiter response |
AI-polished résumé | Permitted assistance, exaggeration, or misrepresentation | Validate claims through structured evidence |
Candidate reading AI-generated answers | Unauthorized assistance if policy forbids it | Apply a published interview-AI policy consistently |
Different person completing an assessment | Proxy or assessment fraud | Reverify identity and assessment ownership |
Interviewer and eventual worker appear to differ | Impersonation or identity handoff | Stop onboarding and escalate |
Synthetic face, altered voice, or real-time face swap | Deepfake job interview fraud | Preserve evidence and use approved verification process |
Stolen identity plus remote-access infrastructure | Potential organized cyber-enabled employment fraud | Involve security, HR, legal/compliance and, where appropriate, law enforcement |
As a technical recruiter, I therefore would not train an interview panel to “spot deepfakes” as though recruiters were human forensic engines. I would train them to recognize identity-integrity exceptions and move those exceptions into a repeatable escalation path.
Lip-sync problems are observations, not verdicts. So are an unusual accent, an unfamiliar communication style, nervousness, a virtual background, poor eye contact, a delayed answer, or a candidate who does not resemble a professionally edited profile photo.
The defensible question is not “Does this person look suspicious to me?” It is “Can we establish, using the same documented controls we apply to comparable candidates, that this is the same person and that this person produced the evidence we are evaluating?”
That shift matters for fairness as much as security. A badly designed anti-fraud process can turn recruiters into amateur investigators and make international, neurodivergent, disabled, low-bandwidth or simply anxious candidates bear the cost of false suspicion.
It also changes how I think about the recruiter’s job. The conventional distinction between sourcing-oriented talent acquisition and technically specialized recruiting still matters. Our separate guide to talent acquisition vs. technical recruiting covers that role boundary. High-risk technical hiring now adds another responsibility: knowing when a hiring event needs to cross over to identity, security and compliance specialists.
The goal is not to make every recruiter a cybersecurity analyst. It is to prevent the recruiter from becoming an unmonitored entrance into systems that the security team spends the rest of the organization protecting.
Gartner's Warning: What "1 in 4 Fake by 2028" Actually Means
The Gartner fake candidates 2028 statistic is powerful enough that it needs unusually careful wording.
Gartner’s July 31, 2025 newsroom release says directly that it predicts one in four candidate profiles worldwide will be fake by 2028. HR Dive’s Carolyn Crist reported the same forecast on August 8, 2025, and Staffing Industry Analysts also relayed it that month, so this is not merely a statistic circulating through vendor marketing pages.
There is also an April 9, 2025 Gartner research listing titled Mitigate Rising Candidate Fraud Through Identity Verification. Its public abstract says recruiting leaders should use identity-verification tools and stronger screening processes as GenAI, fraudulent documents and hidden locations increase candidate-fraud risk.
The precision that often disappears in social-media versions of the forecast is the word profiles. Gartner did not report that one out of every four humans sitting in interviews in 2028 will be a deepfake.
That distinction is essential. A “fake profile” category can encompass forms of falsification that are materially different from a synthetic person or nation-state infiltrator.
The same caution applies to several other statistics now appearing beside Gartner's forecast.
Widely cited figure | What the source actually supports | Confidence / caveat |
1 in 4 candidate profiles fake by 2028 | Gartner forecast | High confidence that Gartner made the forecast; it remains a forecast, not measured 2026 prevalence |
6% involved in interview fraud | Gartner survey of 3,000 candidates; respondents reported impersonating someone or using a proxy | Directly stated by Gartner, but based on self-reporting |
41% hired/onboarded a fraudulent candidate | GetReal Security survey of IT, cybersecurity, risk and fraud leaders | Real reported survey figure, but not a Gartner statistic |
47% Famous Chollima share | CrowdStrike share of state-sponsored hands-on-keyboard operations against the technology sector in its observed dataset | Strong primary-source support, but narrower than “47% of all tech hacks” |
25–30% of flagged sessions | Figure repeated in 2026 commentary about InCruiter | Vendor/secondary claim; no independently audited methodology was located |
One attribution needs correcting. The often-repeated claim that 41% of security leaders have knowingly or unknowingly hired a fraudulent candidate should not be attributed to Gartner.
GetReal Security published that figure in December 2025 from its Deepfake Readiness Benchmark research, saying 41% of IT, cybersecurity, risk and fraud leaders surveyed reported that their organization had hired and onboarded a fraudulent candidate. Security Magazine subsequently covered the same finding in February 2026.
GetReal's disclosed methodology says the research involved 668 leaders at organizations with at least 1,000 employees, surveyed in September 2025 across 15 industries. That makes it meaningful evidence of enterprise concern, but it should not be transformed into “41% of all employers have hired a fake worker,” which the study does not establish.
The 6% figure is different because Gartner itself publishes it. Gartner says the 3,000-candidate survey specifically asked about interview fraud involving impersonation, making it much closer to the identity problem discussed here than broad measurements of AI résumé usage.
Gartner's recommended response is also worth more attention than the headline forecast. Its published guidance calls for clear rules around acceptable AI use, safeguards in assessments, stronger background checking, identity verification, anomaly alerts and “system-level validation” rather than reliance on individualized surveillance.
That last phrase reflects the mature way to approach candidate identity verification in 2026. Recruiters should not be expected to win a visual arms race against increasingly convincing media manipulation.
The system should instead make an attacker defeat several independent controls.
Experian’s January 13, 2026 forecast strengthens that interpretation. Experian placed “Deepfakes outsmart HR” among five major fraud trends for the year and predicted that generative AI would make hyper-tailored résumés and deepfake candidates capable of passing remote interviews a growing identity-and-intent problem for employers.
That matters because Experian is not primarily an interview-software company trying to create a market for an HR feature. Its decision to classify deepfake job candidates within a broader fraud forecast is one indication that recruiting identity integrity is moving into mainstream enterprise risk management.
For the wider changes affecting hiring teams, see Refonte Learning's guide to talent acquisition trends and strategies in 2026. Candidate fraud belongs beside those trends, but it needs its own playbook because it involves identity continuity, security access and evidence preservation rather than normal recruiting optimization.
My practical reading of Gartner's forecast is therefore not “panic because 25% of candidates are already fake.” It is more useful: build a verification architecture before the volume becomes large enough that manual judgment cannot absorb it.
Inside the North Korean IT Worker Fraud Networks
No 2026 case study makes the stakes clearer than North Korean IT worker fraud.
On June 9, 2026, Forbes reporter Ty Roush reported that the North Korean-linked group CrowdStrike tracks as FAMOUS CHOLLIMA accounted for 47% of state-sponsored hands-on-keyboard operations against technology companies in CrowdStrike's analysis. The underlying CrowdStrike Technology Threat Landscape report covered April 1, 2025 through March 31, 2026 and said FAMOUS CHOLLIMA pursued fraudulent employment across North America, Europe and Asia.
The denominator matters. CrowdStrike did not say FAMOUS CHOLLIMA caused 47% of every cyberattack against technology businesses.
CrowdStrike said the group represented 47% of state-sponsored hands-on-keyboard operations against the technology sector in the activity it analyzed. Its report separately says eCrime accounted for 65% of hands-on-keyboard activity targeting technology organizations, which illustrates why collapsing those categories would exaggerate the finding.
Even with that qualification, the number is extraordinary because employment itself functions as the access mechanism. CrowdStrike says remote, high-salary technology roles have historically been a major target for DPRK insider operations and identifies financial gain for the regime as FAMOUS CHOLLIMA's primary motivation.
The recruiting funnel is therefore no longer adjacent to the security perimeter. In these incidents, the recruiting funnel is the attempted perimeter crossing.
The Register provided another detailed view on March 18, 2026. Reporter Dan Robinson described joint IBM X-Force and Flare research mapping an ecosystem of recruiters, facilitators, IT workers and Western collaborators or brokers, with workers coached to pursue Western technical employment using U.S.-based identities.
The report also requires a numerical caveat. The Register used a “100,000-strong” headline and cited information that upwards of 100,000 North Koreans were spread across roughly 40 countries while generating approximately $500 million annually. Flare's own March 25 summary is more nuanced: it says estimates range from 3,000 to 10,000 North Korean overseas workers across multiple industries, while some reports put the broader figure above 100,000 workers across 40 countries; operations are estimated to generate about $500 million per year.
For that reason, I would not publish “there are 100,000 confirmed fake North Korean IT workers” as an audited fact. The evidence supports a large, structured international operation and a roughly $500 million revenue estimate; the population count has substantial uncertainty depending on which category of overseas worker is being counted.
The mechanics are more useful to recruiters than the headline number.
Stage | How the scheme can operate | Hiring-control implication |
Persona creation | Fake or stolen identity, constructed professional history and online profiles | Cross-source identity consistency matters |
Application | High-volume submissions to remote technical jobs and freelance marketplaces | Application volume alone is not enough; verify evidence |
Interview | Proxy participation, artificial backgrounds, AI assistance or manipulated identity signals | Maintain identity continuity during live stages |
Paperwork | Facilitator or collaborator supports verification, paperwork or domestic presence | A successful document check should not end verification |
Laptop delivery | U.S.-based person receives company hardware | Confirm intended worker and delivery destination |
Employment | Overseas operator remotely accesses device and performs work | Coordinate HR identity controls with endpoint/security telemetry |
Expansion | Worker gains systems, client or code access; sometimes multiple people assist | Least privilege and post-hire monitoring remain essential |
Flare and IBM X-Force say the operations they investigated were highly structured. Their research describes facilitators managing fake identities and applications, technical workers carrying out the actual work, and Western collaborators providing identities, receiving company laptops and sometimes completing paperwork or other physical steps.
The FBI's Internet Crime Complaint Center has independently warned about this facilitator model. Its July 2025 guidance says U.S.-based facilitators may receive employer laptops, establish remote-desktop connections, reship devices, create job-search and financial accounts, purchase AI or background-check services and even attend virtual interviews or meetings on behalf of North Korean workers.
That detail explains why a single identity check is not enough. The individual who passes one stage can be a real person helping another actor get through the next one.
A robust control therefore asks a longitudinal question: Is this still the same verified person?
The criminal cases show that this is not a theoretical security exercise. In July 2025, the U.S. Department of Justice announced that Christina Marie Chapman was sentenced to 102 months in prison for helping North Korean workers posing as U.S. citizens or residents obtain remote IT positions at more than 300 U.S. companies. DOJ said the scheme generated more than $17 million in illicit revenue and involved 68 stolen identities, 309 U.S. businesses and two international businesses.
In a separate nationwide enforcement announcement, DOJ described “laptop farms” through which overseas North Korean workers remotely accessed employer-provided computers. It said workers gained access to sensitive employer information and that some activity involved export-controlled U.S. military technology and virtual currency; another alleged scheme involved more than $900,000 in stolen cryptocurrency from a blockchain company.
Then the story widened again in August 2026.
On August 10, Federal News Network reporter Justin Doubleday reported that FBI Cyber Capabilities Branch deputy assistant director Todd Hemmen said the bureau had identified a DPRK remote IT worker who had been working for the U.S. federal government. The FBI declined further comment, and the agency involved, duration of the case and whether sensitive information had been taken remained unclear, so those unknowns should remain unknown rather than being filled with speculation.
The same report pointed to an earlier case involving software work connected with Federal Aviation Administration contracts and access to sensitive government systems from China.
For technical recruiting teams, that progression matters. The risk has moved from warnings, to corporate prosecutions, to 2026 threat-intelligence measurements, to an active FBI investigation involving a federal organization.
This also explains why remote software roles are especially attractive. They combine comparatively high compensation, geographically distributed hiring, remote assessments, shipment of powerful corporate hardware and eventual access to code repositories, cloud environments, internal messaging, customer systems and sometimes production infrastructure. CrowdStrike specifically identifies remote high-salary technology roles as a historic DPRK target, while Flare and IBM describe access extending into common corporate and client systems once a fraudulent worker is embedded.
The recruiting lesson is not to distrust remote candidates. It is to stop using remoteness as a substitute for identity assurance.
The New Generation of Detection Tools
Until recently, most hiring stacks were designed primarily to answer three questions: Can we find enough candidates? Can we assess them consistently? Can we move qualified people through the process efficiently?
The interview fraud detection tools arriving in 2026 add a fourth: can we establish that the person producing the interview evidence is the verified candidate and detect signals that the interaction is being manipulated?
HireID is one example. On August 17, 2026, the company announced an Interview Integrity Platform and Candidate Intake product that it says can verify candidate identity, inspect submitted documents and surface signals associated with deepfakes, impersonation, proxy interviews and unauthorized AI assistance.
Those are vendor-described capabilities, not an independently audited accuracy finding. HireID's launch announcement is a company press release distributed by Newsfile, so recruiters evaluating it should ask for validation data, false-positive and false-negative performance, demographic testing, evidence-retention practices, integration details and human-review workflows rather than treating a feature list as proof of detection effectiveness.
HireID also explicitly says its intake process does not replace work-authorization mechanisms such as I-9 or E-Verify. That is a useful distinction: employment eligibility, background screening and “is this the same human who interviewed?” are overlapping but not identical questions.
Other products are moving the checks inside the interview itself. Zoom announced on June 24, 2026 that BrightHire, a Zoom company, was introducing fraud signals and deepfake detection within live Zoom interviews, describing identity checks, interview-stage detection and broader hiring signals as complementary layers. BrightHire's own product material says it looks for signals associated with impersonation, deepfakes, AI-assisted cheating and identity inconsistencies and sends flagged cases to human review rather than presenting the signal as an automatic rejection decision.
The AI interview assistance detection category deserves particularly careful governance. Detecting that a candidate is receiving prohibited real-time help may protect assessment integrity, but using an AI assistant is not automatically identity fraud; whether it constitutes misconduct depends on what the employer told candidates was permitted.
That policy should exist before the interview.
For InCruiter, a 25–30% detection statistic has been circulating in 2026 commentary. One secondary industry article on deepfake candidates claims that when InCruiter's deepfake technology launched earlier in 2026, it found fraudulent activity in 25–30% of “flagged sessions,” reportedly nearly twice what human interviewers detected.
I would not use that number as an industry benchmark. I could not locate a sufficiently detailed independent audit or primary study establishing the sampling method, what constituted a “flagged” session, the ground-truth labeling process or a comparable human-control methodology.
That does not mean the technology is ineffective. It means vendor-reported detection rates belong in a different evidence category from FBI court cases, DOJ prosecutions, Gartner surveys or CrowdStrike threat telemetry.
Control type | What it is trying to establish | What it should not be expected to prove alone |
Government-ID/document check | Claimed identity corresponds to submitted document | Same person will attend every later stage |
Face match/liveness | Live participant corresponds to enrolled identity | Candidate is personally producing all answers |
Deepfake detection | Video/audio contains manipulation signals | Intent or guilt |
Proxy detection | Different person may be participating | Full legal identity without another verification source |
AI assistance detection | Prohibited external assistance may be occurring | Identity fraud by itself |
Background check | History/records associated with an identity | Continuity between applicant, interviewer and employee |
Human structured interview | Competence and consistency under questioning | Forensic authenticity of media |
This scope differs from ordinary AI interview tooling. Software that helps recruiters transcribe interviews, organize notes, schedule candidates or improve interviewing efficiency solves a recruiter-productivity problem.
Candidate-fraud systems solve an adversarial verification problem.
Conflating the two leads to bad procurement. A team can have an excellent AI-enabled interview workflow and still lack any reliable way to prove that the applicant, assessment taker, video interviewee and person receiving a company laptop are one continuous identity.
The opposite mistake is assuming a fraud detector replaces good recruiting. It does not.
A detector can surface a signal. A structured interview, an identity policy, documented escalation rules, security review and a proportionate final decision turn that signal into a defensible hiring process.
Building a Verification Process Into Your Hiring Pipeline
The biggest improvement I would make in a high-volume technical pipeline is simple: stop treating identity verification as a one-time event.
Think in terms of identity continuity.
The applicant creates an identity claim. The screening call provides another observation. The technical assessment produces work that is attributed to that identity. Each live interview provides additional evidence. Offer paperwork, onboarding and device delivery then connect that candidate identity to corporate access.
A good candidate identity verification 2026 strategy links those events rather than independently “passing” each one.
Gartner makes a similar recommendation at a higher level. Its published candidate-fraud guidance calls for multiple layers, assessment safeguards, stronger background checking, identity verification, anomaly alerts and continued validation rather than a control that ends once somebody receives an offer.
The FBI's guidance reinforces the same principle for the North Korean IT-worker threat. IC3 recommends scrutinizing identity documents, cross-checking photographs and contact information, verifying education and prior employment directly and, when feasible, using in-person interactions as another identity and location check.
I would map controls to the hiring sequence like this:
Hiring stage | Verification objective | Example control |
Application | Establish a coherent identity claim | Duplicate-contact checks; résumé/profile consistency |
Before first high-cost interview | Establish baseline identity | Approved ID/liveness process appropriate to role and jurisdiction |
Technical assessment | Tie work to candidate | Authenticated session, clear AI policy, follow-up defense of submitted work |
Live interviews | Maintain identity continuity | Consistent participant verification and structured questioning |
Pre-offer | Resolve discrepancies | Employment/education/background checks appropriate to role |
Offer and onboarding | Confirm candidate-to-worker continuity | Reverification before credential/device issuance |
Laptop delivery | Ensure device reaches approved worker | Controlled shipping and exception handling |
First access | Limit consequences of a missed fraud case | Least privilege and security monitoring |
Ongoing remote employment | Detect identity handoffs or suspicious access | HR/security exception process based on proportionate risk |
The position of the first identity check should be risk-based. Requiring every early-stage applicant to upload sensitive identity documentation can create unnecessary privacy burden and candidate friction, particularly in a high-volume funnel where most applicants will never be interviewed.
A more proportionate model may place strong identity proofing before an expensive or security-sensitive interview stage while using lighter duplicate-account and consistency controls earlier. Higher-risk jobs involving privileged engineering access, payment infrastructure, cryptocurrency, defense-adjacent technology or sensitive customer systems may justify stronger controls sooner.
The second principle is to write down what acceptable AI use means.
“Don't cheat” is not a usable policy in 2026. Can candidates use AI to improve résumé wording? To practice beforehand? During a take-home task? To autocomplete code? To search documentation? To read suggested answers during a live technical interview?
Those rules need to be role-specific, communicated in advance and applied consistently. Gartner explicitly recommends setting candidate expectations around permissible AI use rather than relying only on detection after the fact.
The third principle is evidence ownership.
When somebody submits code, an architecture exercise or a take-home project, use part of the live interview to ask them to defend it. Change a constraint. Ask why they rejected an alternative. Ask them to debug a small variation.
That technique is useful even when there is no fraud concern because it tests reasoning rather than memorized output. For fraud prevention, it also makes it harder to separate the person who generated the work from the person being evaluated without creating a theatrical “gotcha.”
For North Korean IT-worker schemes specifically, HR and security need shared controls. FBI guidance documents cases where domestic facilitators received corporate laptops and enabled overseas remote access, meaning a recruiting team can complete its workflow “successfully” while the security problem begins at device delivery.
That suggests a fourth principle: candidate verification cannot stop at HRIS status = hired.
Among the red flags I would document are:
identity, photo, résumé, location, contact or employment-history discrepancies that persist when objectively rechecked;
a different individual apparently attending later stages;
duplicate phone numbers, emails, résumés or identities appearing across unrelated applications;
unexpected changes to physical address, payment destination or laptop-shipping instructions;
unexplained use of remote-access infrastructure on a newly issued corporate device;
a candidate who cannot explain technical work they supposedly created;
observable interview-media anomalies that continue after ordinary connection problems are ruled out;
inconsistencies between claimed location and independently verified information.
The FBI and joint Flare/IBM research identify several of those categories, including identity inconsistencies, artificial or manipulated interview environments, Western facilitators, corporate-laptop handling and unauthorized remote-access arrangements.
The key phrase is combination of signals.
I would not reject somebody because their video glitches. I would not reject them because they use an accent the interviewer did not expect, because their room is virtual, because their GitHub activity looks unusual, or because they hesitate over a location question.
Neither would I recommend one of the more gimmicky approaches sometimes proposed for finding North Korean applicants, such as geopolitical trivia or nationality-based “trap questions.” That is not a standardized identity control, and it invites both false positives and discriminatory judgment.
Fraud prevention should make the pipeline more structured, not more subjective.
For high-volume teams, I would track four operational metrics: verification exceptions by stage, false-positive rate after investigation, time required to resolve an exception, and confirmed cases by fraud type. Without those numbers, a new fraud tool can quietly create a second queue of manual work while nobody knows whether it is actually reducing risk.
The control architecture should ultimately look less like “recruiter spots a deepfake” and more like this:
identity baseline → authenticated assessment → continuity checks → discrepancy resolution → verified onboarding → controlled access → post-hire monitoring for genuinely high-risk roles.
That is much harder to defeat than a recruiter staring harder at somebody's face.
What to Do If You Suspect Fraud Mid-Interview
The worst time to invent your fraud-response policy is 18 minutes into an interview.
I learned to think about a suspicious call as an incident with incomplete information. You have an observation; you do not yet have a conclusion.
That framing helps because the immediate objective is not to expose the candidate dramatically. It is to avoid contaminating the evidence, making an unsupported accusation or granting further access while the concern is unresolved.
My interview playbook is:
Stabilize: first eliminate ordinary technical causes. Pause, reconnect or switch the video configuration using your normal support procedure.
Verify: use only approved identity-continuity controls. Ask the candidate to repeat or complete a normal interaction rather than inventing an improvised biometric test.
Probe competence: ask a fresh role-relevant follow-up tied to something the candidate previously said or submitted.
Document: record observable facts, such as “video froze during head movement” or “name differed from assessment account,” rather than conclusions such as “candidate is North Korean.”
Escalate: move the case to the designated recruiting, HR, security, privacy or legal owner rather than conducting an amateur investigation during the call.
Contain: if the concern remains material, pause the hiring or onboarding action until approved verification is complete.
Resolve: either clear the candidate and continue without stigma, or take action under the organization's documented policy.
That “clear the candidate” step matters.
A fraud-control program that can flag people must also have a way to unflag them. Otherwise every detection system becomes a one-way reputation machine in which an innocent network glitch can follow somebody through a hiring process.
For organizations that record interviews, capture biometrics or use automated detection, privacy and employment-law requirements need to be reviewed for the relevant jurisdiction before implementation. The operating rule for recruiters should be straightforward: collect only through approved systems, follow required notice and consent procedures, and do not start making personal recordings or screenshots simply because something looked strange.
When technical indicators suggest a genuine cyber threat rather than ordinary candidate misrepresentation, security should take over the investigation.
That distinction matters in North Korean IT-worker cases because the FBI describes employment as a means of obtaining access to U.S. company networks, sometimes through remotely controlled corporate laptops. DOJ cases have also involved stolen identity information, export-controlled technology and virtual currency.
A mature response matrix might look like this:
Situation | Interviewer action | Escalation |
One visual artifact, otherwise normal call | Troubleshoot normally | None unless repeated |
Persistent audiovisual anomalies | Follow approved continuity check | Recruiting operations if unresolved |
Candidate cannot account for assessment/work | Structured follow-up questions | Hiring manager + recruiting |
Identity records materially conflict | Pause progression | HR/compliance/verification team |
Different person appears across stages | Pause immediately | HR + security |
Suspicious laptop, remote access or corporate-account behavior | Do not investigate through interview tricks | Security/incident response |
Evidence consistent with organized employment fraud | Preserve through authorized systems | Security, legal and appropriate authorities |
For U.S. employers, the FBI and IC3 publish guidance specifically for North Korean IT-worker threats, and organizations dealing with a credible incident can use established law-enforcement reporting channels rather than relying on the recruiter to determine attribution.
This is the cultural change I would emphasize most in interviewer training: you are allowed not to know yet.
“I observed an inconsistency and followed the escalation procedure” is excellent recruiting behavior.
“I could tell from the way the candidate looked that they were fake” is not.
Technical Recruiter Salaries in 2026: What the Data Shows
The expansion of recruiting into structured assessment, analytics, compliance and identity-risk coordination raises a practical career question: what does a technical recruiter salary in 2026 actually look like?
The honest answer is that two prominent salary sites currently tell very different stories.
As of August 18, 2026, ZipRecruiter lists the U.S. average Technical Recruiter salary at $69,588 per year, or $33.46 per hour. It says the majority of salaries fall between roughly $50,500 at the 25th percentile and $84,500 at the 75th, with the 90th percentile around $106,000.
Glassdoor's live U.S. page on August 18, 2026 showed roughly $118,000 median total pay, with a displayed total-pay range of approximately $92,000–$156,000. Glassdoor separates estimated base pay from additional compensation on that page.
Source checked August 18, 2026 | National figure displayed | Additional context |
Glassdoor | ~$118K median total pay | ~$92K–$156K displayed total-pay range |
ZipRecruiter | $69,588 average annual pay | ~$50.5K–$84.5K majority range; ~$106K 90th percentile |
That is not a small discrepancy. It is a reminder that “average recruiter salary” is not a single objective market measurement.
ZipRecruiter says its estimates use employer job postings plus third-party data and continuously scan a database of active jobs. Glassdoor's page presents user-contributed compensation estimates and separates base and additional pay, so the two sources are not necessarily measuring identical compensation populations or applying identical title normalization.
A previously circulated Glassdoor figure of $118,676 and a $91,824–$198,234 range did not match the live national Technical Recruiter page on August 18, 2026. The current displayed national figures are those above, so presenting the older numbers as the live U.S. benchmark would be misleading.
For candidates or employers benchmarking compensation, the better practice is to disclose the source, date, geography, seniority, base-versus-total-pay definition and job-title scope.
That is especially important for technical recruiting because “Technical Recruiter,” “IT Recruiter,” “Senior Technical Recruiter,” agency recruiter and internal talent partner may sit in very different compensation structures.
For broader career and compensation context, Refonte Learning's talent acquisition jobs, salary, and certification guide covers the wider talent-acquisition career path. The fraud-prevention skill set discussed here should be viewed as an emerging extension of recruiting capability, not a reason to invent a new salary benchmark unsupported by market data.
The more durable career advantage is knowing how to run a structured funnel under adversarial conditions: evaluate evidence, recognize an exception, maintain documentation, communicate with security and compliance teams, and avoid letting urgency turn into improvisation.
Building This Skill Set: The Refonte Learning Talent Acquisition Program
Candidate fraud detection is not primarily a “buy the right deepfake detector” problem.
The technology sits on top of process. Before a recruiter can use an identity signal responsibly, they need to know how to screen consistently, conduct a structured interview, document evidence, optimize a hiring workflow, operate an ATS, understand compliance boundaries and move candidates through a repeatable process.
Those are the areas where the Refonte Learning Talent Acquisition Program connects directly to this emerging challenge.
As of August 18, 2026, the live program page described a three-month program requiring approximately 8–10 hours per week. Its listed competencies include candidate sourcing and screening, employer branding and recruitment marketing, behavioral and structured interviewing, hiring-process optimization, ATS proficiency, onboarding, diversity and inclusion, recruitment analytics, negotiation and offer management, and compliance/legal considerations in hiring.
Program detail | Current information |
Format | 3 months |
Weekly commitment | 8–10 hours |
Relevant foundations | Screening, structured interviewing, process optimization, ATS, onboarding, analytics and compliance |
Mentor | Kevin Harris, Senior Advisor |
Mentor experience | More than 10 years in Talent Acquisition |
Career outcomes listed | Talent Acquisition Specialist, Recruitment Consultant, HR Coordinator, Hiring Manager, Technical Recruiter |
Certificates | Training Certificate and Certificate of Internship |
One-time fee | $300 |
Installment option | $204 + $98 |
The program page identifies Kevin Harris as a Senior Advisor at Refonte Learning and describes him as a Talent Acquisition professional with more than 10 years of experience building recruitment strategies.
Successful completion currently comes with a Training Certificate and Certificate of Internship, according to the page. The published one-time enrollment price is $300, while the installment option is $204 plus $98; Refonte's course catalog displays the Talent Acquisition offering against a $387 reference price with a 30% discount.
There is an important boundary to state clearly: the curriculum currently visible on the program page does not name HireID, InCruiter, BrightHire, Zoom deepfake detection or another dedicated candidate-fraud product as a taught tool. The verified curriculum describes recruiting tools and processes at a broader level, so it would be inaccurate to market the program as formal deepfake-detection training.
The value is more foundational.
Structured interviewing gives you a repeatable way to test evidence rather than relying on intuition. Process optimization lets you decide where an identity checkpoint should sit. Compliance training helps you understand that anti-fraud controls must coexist with privacy, fairness and candidate rights. ATS proficiency gives you the workflow discipline needed to document exceptions and maintain continuity across stages.
Specialized fraud technology can then be layered onto that operating model.
That sequence is exactly how I would build a recruiting team's capability in 2026: process first, verification architecture second, detection tooling third.
The evidence now justifies doing it. Gartner's verified forecast says one in four candidate profiles worldwide could be fake by 2028, while its survey has already recorded self-reported interview impersonation. Experian has elevated deepfake job candidates into its fraud forecast. CrowdStrike has measured fraudulent DPRK employment operations at striking scale within state-sponsored activity against technology companies. DOJ has prosecuted U.S. facilitator schemes involving hundreds of employers.
And as of August 2026, Federal News Network reports that the FBI is still investigating how a suspected North Korean remote IT worker reached work associated with the federal government.
That is the real lesson of deepfake job interview fraud.
The face glitch on the screen is not the problem you are trying to solve. It is merely one possible signal.
The problem is that most recruiting systems were built on an assumption that no longer deserves to remain implicit: the résumé owner, assessment taker, interview participant, person signing the offer, worker receiving the laptop and human operating the account are all the same person.
In 2026, high-risk hiring teams need to establish that continuity rather than assume it.
For a recruiter, that does not mean becoming suspicious of everyone. It means becoming systematic enough that you do not have to be.