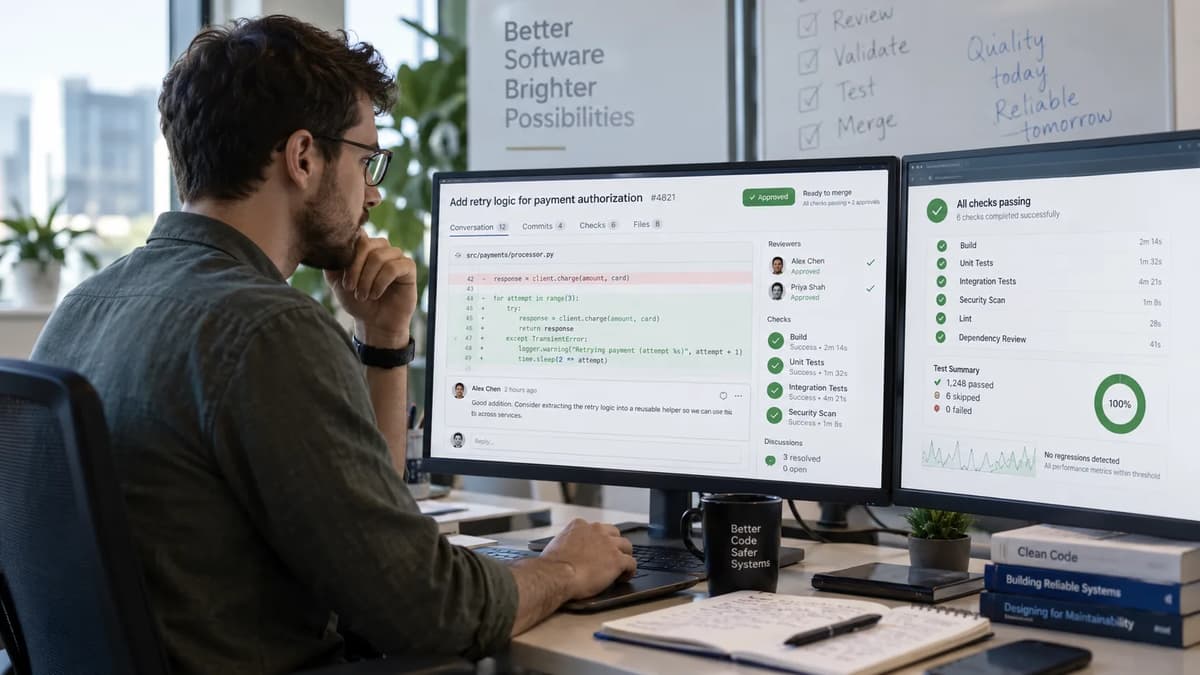
A resolved review thread is a useful signal. It is not, by itself, a merge decision.
That distinction matters more after GitHub’s September 11, 2026 changelog updated Copilot code review. GitHub says that when a later commit addresses a Copilot review comment, Copilot can resolve that comment during re-review. The same update also expanded review analysis with shell tools and an ensemble approach for Lite reviews. Those changes can reduce review friction, but they do not collapse conversation state, approval state, test evidence, and repository policy into one control.
For software leads, maintainers, security reviewers, and platform engineers, the operational question is narrower: what evidence applies to the exact commit that is about to merge? Product-behavior statements below are bounded to the research cutoff of September 15, 2026; later documentation changes should be rechecked before publication or policy enforcement. This playbook treats the pull request at a particular commit as the unit of governance. It separates documented GitHub behavior from a proposed operating model, shows where evidence becomes stale, and gives you a reversible way to test Copilot code review auto-resolution and approval-preview behavior without treating automation as proof of correctness.
Define merge readiness independently of comment count
A merge-ready pull request needs an evidence argument, not a tidy conversation pane. A thread may be resolved because feedback was addressed, acknowledged, or otherwise closed. That says something about discussion state. It does not prove the current code has the required approval, that regression tests actually executed, or that repository rules were satisfied without a bypass.
GitHub’s protected-branch documentation, accessed September 15, 2026, lists review requirements, required status checks, and required conversation resolution as separate settings. That separation is the right mental model for AI code review governance: do not infer one control from another.
Evidence dimension | Merge-ready question | A quiet thread list proves |
Current code | Is the reviewed and tested commit the current head commit? | Nothing about commit freshness |
Review state | Are required approvals valid under the configured rules? | Only that discussions are closed |
Executed validation | Did the tests we rely on actually run against the relevant commit? | Nothing about execution |
Repository policy | Are branch/ruleset requirements satisfied without an unexplained bypass? | Nothing about policy enforcement |
Proposed operating rule: define Copilot merge readiness as the conjunction of current-commit identity, valid review evidence, executed validation, and applicable repository policy. A resolved-comment count is an observation, not a quality score.
That framing also fits broader modern software development practices: tools can change the workflow, but the merge decision still needs explicit engineering criteria. The internal article is context, not authority for GitHub behavior.
Map the states that auto-resolution can change
GitHub’s September 11 changelog documents a specific behavior: when you push a commit that addresses a Copilot code review comment, Copilot can resolve the comment during its re-review; outstanding feedback remains open. The same changelog says the analysis updates do not change how reviews are requested or received.
That is narrower than “Copilot decides the pull request is safe.” Auto-resolution changes the state of a discussion thread. It does not inherently establish a new human approval, prove that tests ran, or rewrite branch-protection policy.
State | Auto-resolution can change it? | Governance interpretation |
Copilot discussion open/resolved | Yes, on documented re-review behavior | Conversation evidence only |
Copilot review assessment | Re-review can produce new review output | Review evidence; validate scope |
Required approval count | Only under the separate approval-preview configuration | Check effective settings |
Status-check result | No, not merely because a comment resolved | Inspect CI evidence independently |
Branch/ruleset requirement | No | Evaluate the repository’s configured gate |
The distinction is especially important because “Copilot” spans different responsibilities. A coding agent that implements changes and Copilot code review that critiques a pull request are not the same control surface. For adjacent context on that separation, see Refonte Learning’s discussion of Copilot agent workflow boundaries. Current code-review approval behavior must still be taken from current GitHub documentation. That creates an apparent source tension worth naming: material about Copilot cloud agent may state that the agent cannot approve its own pull request, while the live Copilot code review documentation describes a public-preview path where a code-review approval can count toward merge requirements. Those statements address different surfaces and should not be flattened into the universal claim “Copilot can never approve.”
An addressed comment is not a complete regression argument
Suppose Copilot flags a missing null check. The author pushes a fix. On re-review, the comment is resolved. You now have evidence that Copilot considers the underlying feedback addressed. You do not yet have evidence that the fix preserves behavior across the surrounding call graph, handles the negative case correctly, or avoids a new security or performance regression.
GitHub’s responsible-use documentation, accessed September 15, 2026, is explicit that Copilot can miss code-quality problems, generate false positives, and produce suggestions that may be inaccurate or insecure; GitHub instructs users to review and test generated code.
Post-resolution evidence checklist:
Confirm the fixing commit is the current pull-request head.
Read the actual diff that addressed the comment.
Run the targeted positive and negative tests required by the risk.
Check whether any later commit invalidated the review or test evidence.
Record who owns the residual risk decision.
Default reviews and approval-preview reviews differ
The safest current statement is not “Copilot approvals never count.” GitHub’s live code-review documentation, accessed September 15, 2026, says that, by default, Copilot reviews do not count toward required approvals. It also says Copilot approvals are in public preview and, when enabled through the applicable repository, organization, and enterprise settings, Copilot can submit an approving review that satisfies a repository approval requirement. If new commits are pushed after Copilot approves, that Copilot approval is dismissed and a review can be re-requested.
Before describing the actual effect in a repository, inventory the effective enterprise, organization, and repository settings. GitHub’s configuration documentation, accessed September 15, 2026, shows that enterprise policy can constrain lower levels and that repository settings include separate controls for allowing Copilot approvals and allowing those approvals to count toward merge requirements.
Inventory repository rules and reviewer settings
Do not start a governance rollout by changing settings. Start with a read-only inventory that tells you what can affect the pull request today. Capture the effective configuration with a timestamp or configuration revision identifier that your team can reproduce later.
GitHub’s code-review configuration documentation, accessed September 15, 2026, describes automatic-review controls at multiple scopes. At repository level, a ruleset can automatically request Copilot review and can optionally enable “Review new pushes.” If that option is not selected, GitHub says Copilot reviews the pull request once unless a re-review is manually requested. Approval-preview settings are configured separately.
Inventory item | Record | Why it matters |
Auto-review trigger | New PR, draft behavior, review-new-pushes setting | Determines whether new commits receive automatic re-review |
Approval preview | Enterprise, organization, repository effective state | Determines whether Copilot can approve and whether it can satisfy a requirement |
Required reviews | Count, code-owner rules, stale-approval settings | Defines valid approval evidence |
Required checks | Check names, expected source, strict/loose mode | Defines CI merge conditions |
Conversation resolution | Required or not | Determines whether open threads block merge |
Bypass authority | Actors/roles and whether bypass is prohibited | Identifies override paths |
Keep the inventory descriptive. “Enabled” is a configuration fact; “safe for this repository” is a governance judgment.
The inventory should also identify where authority comes from. A repository administrator may see a repository-level toggle but still be constrained by an organization or enterprise policy. Conversely, a repository may inherit an organization default but override a setting that the higher scope allows repositories to decide. GitHub’s organization-policy documentation, accessed September 15, 2026, states that an enterprise-selected policy can prevent override at organization level.
For auditability, record both the visible setting and its effective scope. “Repository says enabled” is incomplete if an enterprise control determines whether that setting can take effect. The same discipline applies to bypass authority: identify the actor and permission path, not merely the existence of a merge button.
Proposed control: attach the configuration snapshot or revision reference to the pull request’s evidence packet. If policy changes while a pull request is open, mark the packet as needing re-evaluation rather than assuming yesterday’s merge rules still explain today’s green state.
Bind every relevant observation to a commit
The strongest defense against stale evidence is simple: every review, approval, check, and exception should answer “for which commit?” Use the pull request head commit’s full object identifier as the primary evidence key, not the pull-request number alone.
GitHub’s branch-protection documentation, accessed September 15, 2026, explains that stale-approval handling is tied to changes in the diff. It can dismiss approvals when new commits change the diff, and it separately offers a rule requiring approval of the most recent reviewable push by someone other than the person who pushed it. These are distinct controls with different consequences.
A commit-specific review evidence contract can be small enough to use operationally:
Evidence record | Minimum binding |
Code under decision | Pull-request number, base branch, current head commit |
Copilot review | Review timestamp, reviewed head commit, effort level if shown, open/resolved findings |
Human approval | Reviewer identity/role, approval state, commit/diff state the approval covered |
CI validation | Workflow/check name, run identifier, tested commit, execution result |
Exception | Rule bypassed, actor, reason, scope, expiry or incident reference |
Final decision | Commit merged, merge actor/owner, timestamp |
Proposed invariant: no evidence is “current” merely because it is visible on the pull request. It is current only when it can be bound to the head commit or to a policy fact that remains applicable to that head.
Re-review after the code changes
GitHub’s Copilot code-review documentation, accessed September 15, 2026, describes two different re-review paths. Automatic review can be configured to review new pushes. Without that setting, an automatically reviewed pull request is reviewed once, and a later re-review must be requested manually if the code changes.
Therefore, a new push is a re-review trigger condition, not proof that re-review occurred.
New-push condition | Evidence action |
Review-new-pushes enabled and a new review is recorded | Bind the new review to the new head |
Review-new-pushes disabled | Manually request Copilot re-review when required by local policy |
Setting unknown | Treat Copilot review evidence as potentially stale |
Review recorded before latest commit | Do not use it as current-commit review evidence |
Separate stale-approval policy from latest-push policy
GitHub’s protected-branch documentation, accessed September 15, 2026, lets repositories choose among different approval protections. “Dismiss stale pull request approvals when new commits are pushed” invalidates approvals when the relevant diff changes. “Require approval of the most recent reviewable push” requires an authorized reviewer other than the latest pusher to approve the latest changes without necessarily dismissing every earlier approval. GitHub describes the stale-dismissal option as the safer choice when pull-request hijacking is a concern.
Proposed policy decision: choose one combination deliberately by repository risk class, test it, and document why. Do not write “GitHub requires reapproval after every push” unless that is actually true for the configured repository.
Require executed validation, not merely accepted statuses
A green merge box can be weaker evidence than the words “required test passed” imply. GitHub’s protected-branch documentation, accessed September 15, 2026, says a required status check may be in a successful, skipped, or neutral state and still satisfy the required-status-check gate.
That is product behavior. The governance response is local policy: if a test is required because it provides specific risk evidence, your team may need to require proof that the test job actually executed and produced the intended result, not merely that GitHub accepted the check state.
Check state | GitHub merge-gate interpretation | Proposed evidence interpretation |
Successful, test executed | Accepted | Executed validation, subject to commit binding |
Skipped | Accepted as a required status state | Missing execution unless skip is explicitly allowed by policy |
Neutral | Accepted as a required status state | Investigate meaning; do not call it a passed test |
Failure/error | Not accepted | Validation failed |
Result tied to older commit | May still be visible historically | Stale for current-commit claim |
For a claim such as “integration tests passed on the merge candidate,” verify the run targets the current head or the exact merge candidate defined by your process, identify the test job that actually ran, and retain a run identifier or durable link. When conditions intentionally skip a job, such as for documentation-only changes, record that as an explicit policy exception or allowed path, not as silent equivalence to execution.
Stop condition: do not merge when a required test was not actually executed and the team’s intended risk control depends on that execution.
Review generated fixes as new code changes
A suggestion is not evidence; it is code waiting to be evaluated. GitHub’s responsible-use guidance, accessed September 15, 2026, says Copilot code suggestions may be syntactically or semantically incorrect, may fail to resolve the identified problem, and may introduce security issues. GitHub instructs users to carefully review and test generated code.
GitHub’s September 11 changelog also says Copilot can generate a smarter commit message when a user applies an autofix suggestion. A better commit message does not increase the evidentiary strength of the code itself.
Generated-fix gate | Reviewer question |
Understandable diff | Can a reviewer explain the behavioral change without trusting the suggestion text? |
Targeted positive test | Does the intended case now work? |
Negative/regression test | Does the fix preserve behavior that must not change? |
Security/ownership review | Does the change touch an area needing specialist approval? |
Current-commit revalidation | Were review and tests rerun after the fix entered the branch? |
This is where implementation and review responsibilities must stay separate. Copilot code review may suggest a change; GitHub’s Copilot code-review documentation, accessed September 15, 2026, also describes a public-preview capability to pass suggestions to Copilot cloud agent for implementation. That implementation path creates new code that must be reviewed and tested; it does not turn the earlier review comment into an approval of the resulting diff.
Teams exploring generated tests can use material on Playwright AI test workflows as adjacent learning context, but generated tests should still be assessed for what they assert, what they omit, and whether they ran against the merge candidate.
Interpret the vendor’s severity and cost metrics carefully
GitHub’s September 11 changelog reports results from its experimentation with the new Lite ensemble approach: the average number of addressed comments per review increased by 47% for high-severity findings, 31% for medium-severity findings, and 11% for low-severity findings, while review cost decreased by about 8%. GitHub also says the change surfaced more high-severity findings and fewer nits.
Those are vendor-reported experiment metrics with a specific denominator. They are not defect-detection accuracy rates, false-negative rates, escaped-defect reductions, or independently reproduced evidence that production quality improved by 47%.
Metric | What it can support | What it cannot establish alone |
Addressed comments per review | Review-output engagement in GitHub’s experiment | Defect detection accuracy |
Severity distribution | Mix of findings surfaced/addressed | Production impact of those findings |
Review cost | Cost behavior in the measured setup | Total engineering cost |
Comment resolution rate | Whether feedback was acted on | Whether the resulting code is correct |
For a local pilot, measure what maps to your risk: percentage of merge candidates with current-commit review evidence, percentage of required tests actually executed, stale-approval events caught before merge, reviewer override rate, and post-merge regressions traced to review gaps. Define denominators before collecting results.
This is also why AI coding-tool adoption metrics should remain a separate analytical topic. Adoption or activity can explain usage; it cannot substitute for pull-request evidence.
Work through a pull request with misleading green signals
Consider fictional pull request PR-4821 in a payment-service repository. The scenario is intentionally constructed to exercise the controls; none of its names or pass criteria are GitHub defaults.
At commit A1, Copilot flags a retry path that can write a duplicate ledger event. A human maintainer approves after reading the initial change. The author pushes commit B2 with a generated fix. On re-review, Copilot resolves its comment. The repository’s required integration check shows skipped because a workflow condition misclassifies the changed path. Then the author pushes C3, a small refactor. Copilot approvals public preview is enabled in the effective settings.
The pull request now looks quiet. That is exactly when a commit-specific packet should resist the urge to infer readiness.
Revision | Conversation | Approval | Test evidence | Policy/evidence state | Next action |
A1 | Copilot comment open | Human approval recorded | Unit tests ran on A1 | Comment unresolved | Address finding |
B2 | Comment resolved on re-review | Human approval may be stale under chosen rule | Integration check skipped | Fix changed code; execution missing | Re-run required test and re-establish approval |
C3 | Prior resolution remains historical evidence | Any approval not covering C3 is stale for proposed policy | No executed integration run on C3 | Current-commit packet incomplete | Re-review, execute tests, obtain valid approval |
Merge candidate | All required discussions resolved | Approval valid for current policy and commit | Required tests executed on accepted candidate | No unexplained bypass | Merge may proceed |
A resolved discussion and a skipped required test
GitHub’s protected-branch documentation, accessed September 15, 2026, allows a required status check in a skipped state to satisfy the merge gate, but the team’s risk claim may require actual execution. That makes the pull request simultaneously “repository gate satisfied” in one dimension and “validation evidence missing” in another.
For PR-4821, the resolved Copilot thread is relevant: it shows the original feedback was addressed to Copilot’s satisfaction on a re-review. It does not compensate for the skipped integration test.
Proposed state labels:
Satisfied: evidence applies to the current commit and meets local policy.
Stale: evidence exists but applies to an older revision or diff state.
Missing: required evidence was never produced, such as an unexecuted test.
Overridden: a requirement was bypassed by an authorized actor and the override must be recorded.
A new commit after approval
At C3, ask two questions separately: what does GitHub’s configured rule do, and what does local policy require? Under GitHub’s protected-branch rules, accessed September 15, 2026, stale approvals may be dismissed when the diff changes. If the repository instead uses the “most recent reviewable push” requirement, the prior approvals can remain while another authorized reviewer must approve the latest push.
For this fictional repository, assume local policy requires one human approval covering the current revision even though Copilot approvals preview is enabled. That is an organization choice, not a GitHub limitation. The evidence packet therefore requests a fresh human approval and a Copilot re-review if the configured automatic trigger did not already run.
Test policy behavior before enforcing it broadly
Configuration documentation is necessary but not sufficient for rollout. You also need empirical evidence that the settings interact the way your platform team expects in your repository topology, workflow design, and permission model.
Use an isolated non-production repository or a deliberately scoped pilot ruleset. Record the exact settings before each test, then change one factor at a time. The objective is not to “prove Copilot works.” It is to verify your merge-control assumptions.
Test case | Configuration under test | Expected outcome to record | Result |
New push after auto-review | Review new pushes off | No automatic re-review; manual request needed | Record result |
New push after auto-review | Review new pushes on | New Copilot review event appears | Record result |
Default Copilot review | Approval preview not counting | Review does not satisfy required approval | Record result |
Preview approval | Effective approval settings enabled | Copilot may submit approval that satisfies configured rule | Record result |
Post-Copilot-approval push | Preview approval active | Copilot approval dismissed per current docs | Record result |
Required test skipped | Required check configured | Merge gate may accept skipped state; evidence policy flags non-execution | Record result |
Stale human approval | Stale-dismissal enabled | Approval dismissed when qualifying diff change occurs | Record result |
Latest-push approval | Latest-push rule enabled | Authorized reviewer must approve most recent reviewable push | Record result |
Bypass attempt | Bypass actor present/absent | Outcome matches documented bypass configuration | Record result |
Generated fix | Suggestion applied | New commit requires normal review/test evidence | Record result |
GitHub’s Copilot code-review configuration documentation, accessed September 15, 2026, documents the automatic-review and approval-preview controls, while GitHub’s protected-branch documentation, also accessed September 15, 2026, defines the review and check behaviors being exercised.
Before enforcing, preserve screenshots or exported configuration facts where appropriate, ruleset identifiers, test pull-request identifiers, and observed outcomes. Do not rely on memory of UI labels.
A team building this test discipline may also find Refonte Learning’s automation engineering foundations useful as adjacent background on test automation and continuous integration. It is not evidence for GitHub’s feature behavior.
Proposed rollout gate: enforcement begins only after the matrix has no unexplained outcome in the controls that can block, approve, skip, or bypass a merge.
Define reviewer accountability and exceptions
Automation changes who produces evidence; it does not remove the need to own decisions. Every repository should have an accountable role for merge policy, an accountable reviewer for high-risk changes, and a named authority for emergency exceptions.
GitHub’s responsible-use documentation, accessed September 15, 2026, says human oversight is an important safeguard because AI outputs can be inaccurate, incomplete, biased, misaligned, or irrelevant. It also says Copilot code review should be supplemented with careful human review.
Decision | Accountable owner | Minimum evidence |
Repository merge policy | Platform/repository owner | Versioned rule definition and test record |
Security-sensitive approval | Designated security/code owner | Current diff review plus relevant security validation |
Generated fix acceptance | Maintainer/change owner | Understandable diff and executed tests |
Emergency bypass | Authorized incident/change owner | Reason, scope, affected commit, follow-up obligation |
Final merge | Named merge actor or accountable maintainer | Current-commit evidence packet |
A “human-only approval” rule can be a sensible local policy for authentication, authorization, payment, safety, or regulated code. Describe it as a chosen risk control. Do not justify it by claiming GitHub universally prevents Copilot from approving: the code-review approval preview is the documented exception in GitHub’s Copilot code-review documentation, accessed September 15, 2026.
For exceptions, require the bypass owner to state what evidence is being waived, why waiting is riskier, and what compensating validation will occur. “Admin merged it” is an event; it is not an exception rationale.
Roll back the policy separately from the application
There are two very different rollback problems: “our review policy behaves badly” and “the merged application change is bad.” They need separate procedures.
If an approval-preview or auto-review rollout produces unexpected gating, first revert or disable the policy change at the scope where it was introduced. Preserve the test pull requests, audit trail, prior configuration, and observed failure. Do not erase evidence simply to make the repository usable again.
Failure type | Recovery target | Evidence to preserve |
Auto-review creates unacceptable churn | Review trigger/ruleset configuration | Prior setting, test results, affected repositories |
Approval preview counts where policy did not intend it | Approval-preview configuration | Effective enterprise/org/repo state |
Required check semantics are too permissive | CI design or evidence policy | Skipped/neutral examples and run IDs |
Application regression after merge | Application commit/release | Merge packet, deployment evidence, incident data |
Generated fix causes defect | Application code plus review process gap | Suggestion source, diff, tests, approvals |
An application rollback is evaluated independently. Disabling Copilot code review does not revert code Copilot suggested, code an agent implemented, or code a human merged. Restore the application through the normal version-control and release path, then investigate which evidence failed to predict the regression.
That separation belongs in broader DevOps lifecycle management: repository policy, continuous integration (CI) validation, deployment, and production recovery are connected stages, but each has its own rollback object.
Proposed recovery rule: rollback policy first when governance behavior is wrong; revert application code when product behavior is wrong. Never use one as a substitute for the other.
Build a review packet that survives a post-incident audit
A good review packet should let someone reconstruct why a specific commit was merged without relying on the current pull-request UI. The UI can change, discussions can collapse, settings can evolve, and a reviewer can forget why an exception was granted.
The packet does not need to copy proprietary source code or secrets. It needs stable identifiers, evidence references, and decision context.
Packet field | What to retain |
Commit identity | Pull request, base, merged head/merge commit, timestamps |
Diff evidence | Durable repository link or change summary; avoid unnecessary code export |
Review output | Copilot review event, effort level where relevant, human reviews |
Resolution events | Which discussions resolved, by whom/what mechanism, at which revision |
Approvals | Reviewer, state, commit/diff relevance, dismissal/reapproval events |
Checks | Workflow/run IDs, commit tested, executed/skipped/neutral outcome |
Exceptions | Bypass authority, rationale, scope, expiry/follow-up |
Final ownership | Person or role accepting merge risk |
GitHub’s responsible-use material, accessed September 15, 2026, emphasizes traceability for agentic work and warns that generated code can be inaccurate or insecure; for review governance, the same practical lesson applies: preserve enough context to examine what the automation did and what humans decided afterward.
Minimize sensitive exposure. Prefer commit hashes, run identifiers, policy revisions, and access-controlled repository links over copied source, secrets, production payloads, or personal data. If a security review contains sensitive findings, store the detailed record in the system authorized for that material and put only the reference in the merge packet.
Treat the packet as a chain of claims, not a screenshot archive. “Check green” should expand to “check X produced status Y for commit Z, and policy says Y is acceptable for this risk.” “Approved” should expand to “reviewer R approved the diff state governed by rule Q.” That structure makes later policy changes survivable: an investigator can replay the historical decision using the rules that applied then rather than interpreting old evidence through today’s configuration.
Audit test: an independent maintainer should be able to answer “what code, what review, what executed validation, what rule, what exception, and who accepted the risk?” from the packet.
Pilot review automation with measurable exit gates
A governance rollout should be reversible and observation-first. A proposed 30-day pilot is long enough to encounter ordinary re-review and CI paths without pretending that 30 days is a GitHub recommendation or a statistically guaranteed evaluation period.
Start with repositories where ownership is clear and rollback is cheap. For the first phase, observe and collect evidence without changing merge authority. Only after test cases match documented behavior should you enable enforcement or allow preview approvals to count.
Proposed 30-day pilot checklist:
Days 1–7: inventory settings, define evidence fields, and run the isolated policy matrix.
Days 8–14: enable auto-review/re-review behavior for a scoped repository, but keep existing approval policy.
Days 15–21: measure stale evidence, skipped-check cases, generated-fix validation, and reviewer overrides.
Days 22–30: decide whether to expand, narrow, or roll back based on predefined exit gates.
Exit only when policy ownership, rollback steps, and current-commit evidence are consistently demonstrable.
Useful exit measures include “all merge decisions sampled had identifiable current-commit evidence,” “no unexplained skipped required tests were treated as executed,” and “all bypasses had named owners.” Set your own thresholds; no numerical pass threshold here is a GitHub default.
For practitioners building the underlying engineering judgment, Refonte Learning’s Software Engineering Program lists software development lifecycle, application security, scalable software solutions, full-stack development, cloud and microservices, performance, and a capstone among its foundations; the live page lists a three-month duration and 12–14 hours per week, with admissions tied to pursuing or completing a bachelor’s degree in computer science, engineering, mathematics, or a related field. Those foundations are relevant to reasoning about review evidence, but the page does not establish a dedicated Copilot review-governance module.
Answer the review questions and decide whether to merge
Does Copilot code review auto-resolution mean the requested change is correct? No. The September 11 update says Copilot can resolve its addressed comments during re-review after a later commit addresses the feedback. That records discussion state. GitHub separately warns in its responsible-use documentation, accessed September 15, 2026, that Copilot can miss problems and generated suggestions can be wrong or insecure, so the fix still needs review and testing.
Can a Copilot review satisfy a required approval? By default, GitHub’s live code-review documentation, accessed September 15, 2026, says Copilot reviews do not count toward required approvals. Under the Copilot approvals public preview, when the necessary settings are enabled, Copilot can submit an approving review that satisfies the repository’s approval rule. Check effective enterprise, organization, and repository settings before making a claim about a specific pull request.
Is a skipped required status check equivalent to an executed passing test? No. GitHub’s protected-branch documentation, accessed September 15, 2026, lists successful, skipped, and neutral as acceptable states for a required status check. A team that relies on actual execution must inspect and record execution evidence rather than translate every accepted state into “tests passed.”
What should happen after a new commit? Re-evaluate evidence. Confirm whether Copilot re-reviewed automatically or needs a manual request under GitHub’s code-review documentation, accessed September 15, 2026; determine how GitHub’s protected-branch rules, also accessed September 15, 2026, affect human approvals; and run the validations required for the new head commit. Do not assume every new push is automatically reviewed.
The final merge decision should be mechanical enough to resist a persuasive UI state:
Current-commit merge checklist | Required answer |
Is the exact head commit identified? | Yes |
Do review and approval records satisfy the effective configured policy for that commit/diff? | Yes |
Did every locally required test actually execute, or is an allowed skip explicitly documented? | Yes |
Are generated fixes reviewed as code changes rather than trusted as remediation proof? | Yes |
Are bypasses/exceptions owned, recorded, and still valid? | Yes |
If any answer is “no” or “unknown,” the pull request is not ready under this proposed governance model. Stop when evidence belongs to an older commit, a required test did not execute, policy ownership is missing, or a generated fix has not been validated. Resolve the evidence gap first. Merge readiness is a claim about the current change under the current rules. It is not an endorsement of an AI reviewer, and it is not a count of resolved comments.