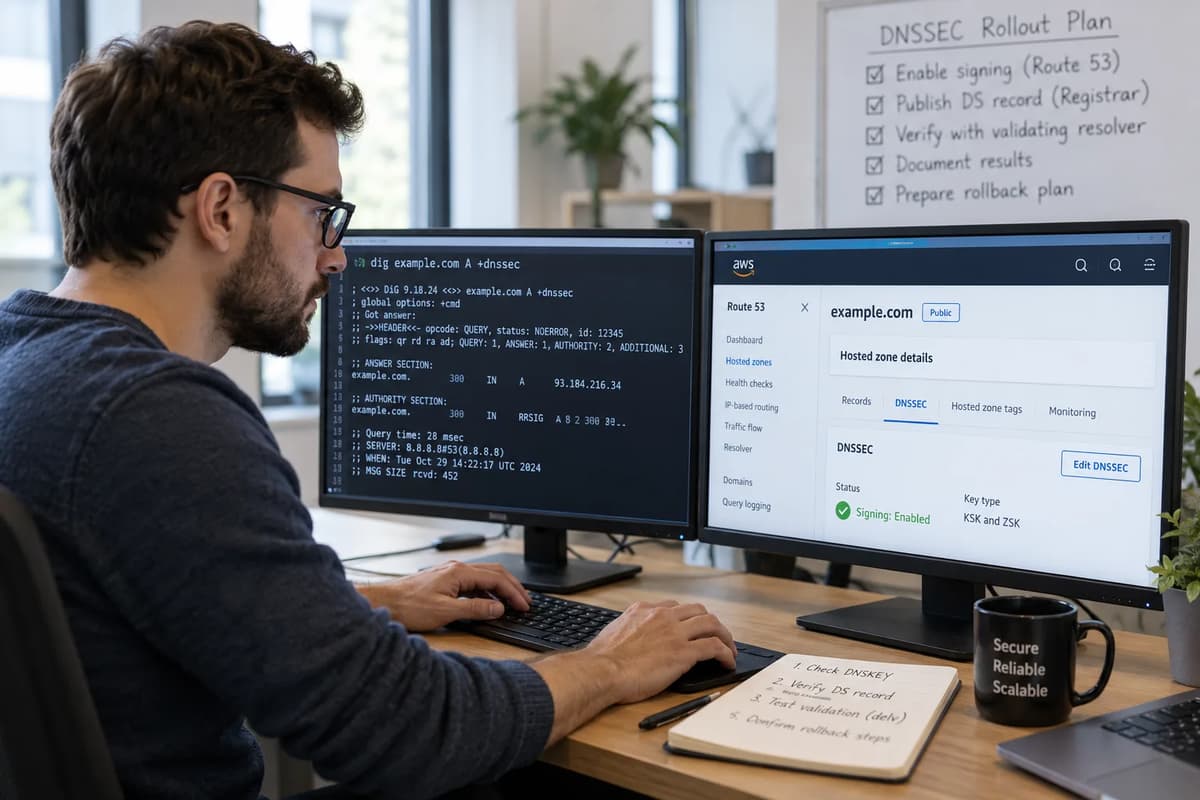
When a DNS zone in AWS Route 53 shows DNSSEC Signing: Enabled but no parent DS record exists and no validating-resolver record has been captured, the chain of trust is incomplete. This playbook separates three claims that need independent evidence: the hosted zone is signing responses, the parent delegation carries the matching DS record, and a resolver validates a specific answer. It identifies the Route 53 account owner, the registrar or parent-zone operator, and the validating-resolver operator who must cooperate. The main rehearsal uses one authorized public test zone with no delegated child zones and a parent that supports DS publication. Every proposed command, timestamp, tool version, trust anchor, and rollback gate belongs in a change ledger. Deliberate failure cases belong only in a disposable public test name. The result is either an observed chain of trust or a documented hold and recovery decision, never a claim that enabling signing alone proves resolver validation.
Separate zone signing from a trusted answer
Four statements are often conflated when planning DNSSEC: that Route 53 has started signing records, that the delegation carries a matching DS linking to a trust anchor, and that a resolver has validated an answer. These must be treated as distinct claims with distinct evidence. For example, one can see DNSKEY and RRSIG records in the hosted zone (proof of signing) yet still have no DS at the parent or any resolver set up for validation (so the chain is broken). We must gather evidence for each:
Authoritative signing (child zone): The hosted zone is producing DNSKEY and RRSIG records. Evidence: queries against Route 53 authoritative nameservers should return DNSKEY and RRSIG. For example, dig @ns-*.awsdns-*.net example.com DNSKEY +noall +answer should list the DNSKEY RRset, and dig example.com A +dnssec should show an RRSIG for the A record, indicating the child zone was signed by a Zone Signing Key (ZSK) and Key Signing Key (KSK). This shows Route 53 is signing.
Delegation completed (parent DS): The parent zone (e.g. .com or a parent domain) has a DS record that exactly matches the KSK in the child zone. Evidence: a query at the parent’s authoritative servers (or via the registrar API) confirms the DS exists, and its fields (key tag, algorithm, digest type, digest) match those reported by Route 53. This is the chain of trust link between the parent and child.
Resolver validation (end-to-end): An independent validating resolver (or delv with a trust anchor) returns the record with the DNSSEC authentication status set to “validated” (AD flag or equivalent). Evidence: a successful delv example.com A or dig example.com A +dnssec on a DNSSEC-aware resolver with a known trust anchor should return “Status: NOERROR” and the AD bit (or a message like “delv validates” with no errors). If validation fails, delv will explicitly note the failure.
These correspond to three columns in our state table. In summary:
Claim | Child (authoritative) Evidence | Parent/Registrar Evidence | Resolver Evidence (validation) |
Signed | Authoritative DNSKEY and RRSIG records are present in the child-zone answers. | Not applicable: signing is internal to the child zone. | Not yet tested: signatures alone do not establish validation. |
Delegation DS present | Not applicable: the DS belongs at the parent. | The parent DS matches the child KSK field for field. | Without a parent DS, the delegation remains insecure. |
Chain validated | The child continues to sign authoritative answers. | The parent trust link must exist first. | A validator records a cryptographically secure result from the documented trust anchor. |
Requesting DNSSEC data with dig +dnssec does not prove validation; it only asks the server to include DNSSEC records. A validating tool such as delv, or a resolver with a recorded trust model, must establish the result. For context, review DNSSEC within broader network-security knowledge; this playbook is not a general cryptography tutorial. The focus is evidence and operational boundaries: what must be true at each layer before the chain can be accepted.
Inventory the zone, delegation, owners and TTLs
Before touching anything, document the starting state. Record the domain name, AWS hosted-zone ID, and authoritative name servers (via dig NS). Note the parent domain and registrar/operator. For each party, identify the person or team allowed to change DS records and the person who controls the AWS account and KMS key. Confirm no child sub-zones are delegated under this domain.
Example inventory table:
Zone name: example.com (public hosted zone in AWS)
HostedZoneId: Z123ABCDE (Route 53)
Authoritative servers (child): ns-000.awsdns-00.com., ns-001.awsdns-01.org., etc. (from Route 53 console or dig NS example.com)
Parent domain: com (TLD, or could be a second-level domain if example is a subdomain)
Parent operator: (TLD registrar, e.g. Verisign for .com, or specific registrar UI if domain registrar)
Registrar account/owner: (e.g. DNS team handles example.com, or AWS account ID if using Route 53 domains)
Existing DS record: (check dig example.com DS; expect none if never enabled)
TTL settings: Note the maximum TTL in the zone (SOA MINIMUM or highest record TTL). Example: SOA min=300, SOA TTL=900, NS records TTL=900, a TXT with TTL=86400: current max=86400 (1 day). We’ll log these values and also record current DNSKEY/RRSIG counts (which should be none initially if signing off).
Owners for DS changes: Document who can add/remove the DS: e.g. “Registrar contact Alice can add DS via registrar portal; AWS Account Admin (CloudTeam) can also update Route 53 if domain is with Amazon Registrar.” If a TLD directly, note if the parent is managed by an ISP or other registry interface. Also list who controls the AWS KMS key and who can run route53:ChangeResourceRecordSets or create-key-signing-key.
This creates a ledger of who owns what and preserves the pre-signing state. A proposed lab can use a disposable, authorized public zone to simulate failures without touching a customer domain. Keep the initial answers, TTLs, owners, and last known working configuration with the change record. Readers who need prerequisite context can review DNS and system-administration foundations.
Qualify the hosted zone and signing-key prerequisites
Before enabling DNSSEC, qualify the public hosted zone, the parent publication route, and the signing key. The AWS KMS requirements for DNSSEC specify a customer managed asymmetric key in us-east-1 with KeySpec ECC_NIST_P256 and KeyUsage SIGN_VERIFY. Inspect the key rather than relying on its alias. The change role also needs the Route 53 permissions required to create the KSK and enable hosted-zone signing. Treat any missing parent-DS path, key-policy access, or change permission as a hold.
Both KMS and parent-delegation ownership should have clear owners.
KMS key and permissions: Confirm that the key is asymmetric, uses ECC_NIST_P256, is enabled in us-east-1, and is not pending deletion. Verify the complete AWS-documented key policy for the dnssec-route53.amazonaws.com service principal; do not reduce the requirement to kms:Sign alone. Loss of KMS access can put the KSK into an ACTION_NEEDED state. Restore the existing key and permissions first, then reactivate the KSK. A replacement key would require a separately reviewed key and DS transition, not an improvised shortcut.
Zone and domain prerequisites: AWS warns that a parent DNS provider that cannot answer DS queries authoritatively can make a signed child zone unresolvable. Query the actual parent authoritative servers, not only a recursive resolver, and confirm that the registrar or parent operator supports the required DS publication. If that route is unavailable, stop and select a suitable test domain before enabling signing.
Checklist (preflight):
Hosted zone exists and is public, not private.
KMS key in us-east-1, KeySpec=ECC_NIST_P256, and Enabled.
Route 53 can use the customer managed key through the complete AWS-documented key policy.
Zone’s current TTLs noted (max, SOA min, etc.), and owners aware of these values.
The parent authoritative service and registrar support DS publication and authoritative DS responses.
Owners assigned: AWS admin for KMS, DNS admin for registrar/DS.
Plan in place if KMS key access lost: who will fix key vs who will update DS.
Record account IDs or team names for these owners, but do not commit secrets. This split between the KSK owner and the parent-DS publisher is a practical example of cloud key-management responsibilities. It also makes the escalation path explicit when either side is unavailable.
Check the KMS region, key type and access
AWS requires the DNSSEC KSK to be backed by a customer managed AWS KMS key in us-east-1 with the ECC_NIST_P256 key spec and SIGN_VERIFY usage. Use a read-only describe call to inspect the actual key:
aws --region us-east-1 kms describe-key --key-id alias/my-kms-ksk
Confirm KeySpec is ECC_NIST_P256, KeyUsage is SIGN_VERIFY, KeyState is Enabled, and the key is not pending deletion. The key policy must use the DNSSEC Route 53 service principal, dnssec-route53.amazonaws.com, and include the AWS-documented DescribeKey, GetPublicKey, Sign, and constrained CreateGrant permissions. Keep real account IDs and key-policy documents out of public logs.
If the KSK enters ACTION_NEEDED, restore access to the existing customer managed key and reactivate the KSK. AWS troubleshooting guidance notes that unresolved loss of key access can eventually make the zone unavailable to validating resolvers. Capture fresh signing and resolver evidence after the repair.
Assign parent-DS and key-lifecycle ownership
Name the responsible persons or teams for each action:
Child zone owner: (e.g. Cloud DNS team): can run Route 53 APIs (create KSK, enable DNSSEC).
KMS key owner: (e.g. Security Ops): maintains the KMS key’s rotation and policy. If the key goes missing, they re-enable it.
Registrar/parent operator: (e.g. Domain Admin): can publish or remove the DS record at the parent. If the DS is wrong, they fix it.
For each role, document backup contacts and the channel (ticket, on-call, email) for urgent response. For example, if a Key’s permissions change in error, KMS owners must restore them. If the registrar interface is down and DS can’t be published, DNS owner escalates to the registry support. Never remove or delete the KMS key out of panic; that loses all trust. Instead, if a key is compromised or lost, treat it as an emergency requiring new key creation and DS rollover. All parties should understand the reversal plan in their domain: for example, if DS needs to be withdrawn, the registrar knows to remove the record and note its TTL.
Capture an unsigned baseline and a recovery plan
Before signing, capture the “clean” DNS behavior. Use dig or similar tools to query records and record the results. This includes the A (or any) record answers, the NS delegation, and how the parent responds to DS queries. Also log the resolver endpoints you use for testing.
Example commands (synthetic output):
# Query child zone via one of its NS
dig @ns-000.awsdns-00.net example.com A +noall +answer
;; ANSWER SECTION:
example.com. 900 IN A 192.0.2.123
# Query parent for DS
dig +short example.com DS
# (Expect empty)
# Query a public resolver before DNSSEC (should give AD=0 and no DS)
dig @8.8.8.8 example.com A +dnssec +multiline
;; flags: qr rd ra; QUERY: 1, ANSWER: 1 ...
example.com. 3600 IN A 192.0.2.123
; ... no AD flag; has RRSIG? (none, since not signed yet)
Record the exact commands, UTC timestamps, resolver endpoints, transport assumptions, and tool versions. Mark sample output as synthetic unless it came from an authorized execution. Define stop conditions before the change. If a validating resolver begins failing after the parent DS is published, hold the rollout and repair or withdraw the parent trust link in the documented order; do not disable child signing while resolvers can still cache the DS.
The unsigned baseline is the recovery reference: known record answers, delegation, TTLs, parent DS state, and resolver behavior. Store the last known configuration and the ordered withdrawal checklist with the change record. Recovery means returning to a reviewed state with fresh authoritative and resolver evidence, not running a one-line disable command out of sequence.
Enable child-zone signing without declaring completion
With prerequisites met and the unsigned baseline captured, follow the AWS procedure for enabling DNSSEC signing and creating a KSK. The example below uses synthetic placeholders and requires a role authorized for the Route 53 DNSSEC operations plus access to the selected KMS key:
# Create a KSK and enable signing (example placeholders)
aws --region us-east-1 route53 create-key-signing-key --hosted-zone-id Z123ABCDE \
--key-management-service-arn arn:aws:kms:us-east-1:111122223333:key/abcdef12-3456-7890-abcd-ef1234567890 \
--name my-ksk --status ACTIVE --caller-reference $(uuidgen)
aws --region us-east-1 route53 enable-hosted-zone-dnssec --hosted-zone-id Z123ABCDE
After the create and enable calls succeed, use the returned change identifier with GetChange and inspect GetDNSSEC. Do not proceed until the relevant Route 53 change is INSYNC and the KSK is ACTIVE. Then retrieve the child-side values for the parent handoff:
aws --region us-east-1 route53 get-dnssec --hosted-zone-id Z123ABCDE
GetDNSSEC returns the zone signing status and a KeySigningKeys array. For the active KSK, capture KeyTag, SigningAlgorithmType, DigestAlgorithmType, DigestValue, DNSKEYRecord, the complete DSRecord string, and Status. Do not copy documentation examples; use the values returned for the authorized zone. A synthetic response shape is shown below:
"KeySigningKeys": [
{
"KeyTag": 12345,
"SigningAlgorithmType": 13,
"DigestAlgorithmType": 2,
"DigestValue": "ABCD1234EF...",
"DSRecord": "12345 13 2 ABCD1234EF...",
"Status": "ACTIVE"
}
]
Save these exact values; you’ll use them to publish the DS.
Meanwhile, query the child zone to see it’s being signed:
dig @ns-001.awsdns-01.org example.com DNSKEY +noall +answer
Query a Route 53 authoritative server and capture the actual DNSKEY RRset and its RRSIG. Expect an active KSK, identified by flag 257, and Route 53-managed zone-signing keys, identified by flag 256. Do not paste invented success output into the change record; record the authoritative answer instead.
# Evidence fields to record from the actual answer
authoritative_server=<actual Route 53 name server>
dnskey_rrset=<verbatim DNSKEY answer>
rrsig_dnskey=<verbatim RRSIG DNSKEY answer>
observed_at_utc=<actual timestamp>
This observation establishes only the authoritative-signing claim. Until the parent publishes the matching DS and a validating path accepts an answer, the state remains: child zone signed; chain not yet established.
Review and publish the exact parent DS record
Now we move to Step 3: publishing the DS at the parent. This is a two-person (or two-role) handoff. The child side must verify the DS fields and communicate them, and the parent side must publish them correctly.
Match the key tag, algorithm and digest
First, on the child side, confirm the DS parameters exactly. Using the earlier aws route53 get-dnssec output, note:
Key Tag (a number, e.g. 12345)
Algorithm (should be 13 = ECDSA P-256 SHA-256)
Digest Type (2 = SHA-256)
Digest (hex string)
Instead of relying on documentation examples, query an authoritative Route 53 name server and compare its current KSK with the values returned by GetDNSSEC:
dig @<ROUTE53_AUTH_NS> example.com DNSKEY +dnssec +noall +answer
If independent derivation is required, save the DNSKEY RRset and use a DNSSEC-aware tool such as dnssec-dsfromkey to derive the DS. The operational handoff still uses the current Route 53 DSRecord and a field-by-field comparison against the parent-authoritative answer.
Child KSK DNSKEY: 257 3 13 <public-key>
Route 53 DSRecord: 12345 13 2 <digest>
Parent-authoritative DS: 12345 13 2 <digest>
Do not copy a sample. Use the exact public DS values generated for this zone, and protect any accompanying account identifiers or change tickets. Proceed only after a second reviewer confirms the zone name, key tag, algorithm, digest type, and digest.
Confirm the record at the parent authority
Next, the parent owner publishes the DS. The JSON below is an example only for a parent hosted zone managed in Route 53; it is not a Route 53 Domains registrar API call. Another registrar requires its own reviewed interface or API.
{
"Comment": "Insert DS for example.com",
"Changes": [
{
"Action": "UPSERT",
"ResourceRecordSet": {
"Name": "example.com",
"Type": "DS",
"TTL": 300,
"ResourceRecords": [
{
"Value": "12345 13 2 ABCD1234EF..."
}
]
}
}
]
}
aws --region us-east-1 route53 change-resource-record-sets --hosted-zone-id Z98765PARENT \
--change-batch file://insert-ds.json
Use the actual parent hosted-zone ID and the exact child-generated DS value. The operator needs permission to change DS records in the parent zone.
After submission, use GetChange when the parent is hosted in Route 53. Otherwise, poll the parent authoritative servers and account for any registrar publication schedule. Query the parent authority directly:
dig @<PARENT_AUTH_NS> example.com DS +dnssec +noall +answer
The actual answer must contain the intended DS value. Compare all four fields and record the observed TTL:
12345 13 2 <digest> # synthetic comparison shape; record the real TTL separately
Evidence: Capture the parent-authoritative DS answer, its TTL, the server queried, and the UTC timestamp. A registrar screen or a DS record placed in the child zone is not proof that the parent delegation changed. When useful, repeat the query against a second parent authoritative server.
dig @a.gtld-servers.net example.com DS +dnssec +noall +answer
Once the parent-authoritative answer contains the exact reviewed DS value, update the ownership ledger with the parent operator, change identifier or ticket, observed TTL, and actual UTC timestamp. The parent publication is complete only when both the submitted value and the authoritative answer agree.
Validate the chain from a recorded trust anchor
With the DS visible at the parent authority, validate from a recorded trust anchor. The BIND 9 stable delv documentation describes local validation and its built-in root trust anchor. Record the installed tool version, the trust anchor used, and the upstream or iterative mode before running the query:
delv -v
delv +ns example.com A
Capture an evidence record instead of inventing successful output:
tool_version=<actual delv -v output>
trust_anchor=<built-in root or reviewed anchor file>
query_mode=<iterative +ns or recorded upstream resolver>
query_name=example.com
query_type=A
result=<secure | insecure | validation failure>
diagnostic=<verbatim tool message>
observed_at_utc=<actual timestamp>
As a second observation, query an approved validating resolver and record the endpoint and transport assumptions. The AD flag is that resolver’s assertion; it is not independent local validation. Use a placeholder until the approved resolver is known:
dig @<VALIDATING_RESOLVER_IP> example.com A +dnssec +multi
Accept this evidence only when the actual answer contains the intended record, the resolver sets AD under the documented trust assumptions, and the same chain validates locally with delv or another approved validator. Record the full query, result, endpoint, tool version, trust anchor, and UTC timestamp.
Distinguish requested signatures from validation
Running dig +dnssec requests DNSSEC records; it does not validate them locally. An RRSIG proves that signature data was returned, not that the chain was accepted. The AD flag is meaningful only as the selected recursive resolver’s assertion and only when the client trusts the path to that resolver. delv performs local validation using its configured trust anchor. Record these assumptions with every result.
Separate secure, unsigned and failing outcomes
Consider possible outcomes in validation checks:
Secure: The parent DS matches the child KSK, the signed answer is current, and the approved validator records a secure result. Interpretation: the tested chain validated for this query and observation path.
Unsigned or insecure delegation: The child may return RRSIG records, but the parent has no DS for the zone. A validating path treats the delegation as insecure rather than secure. Interpretation: signing exists, but no trusted chain has been established.
Validation failure: A DS is present, but the DNSKEY, signature, time validity, or delegation evidence does not validate. A validating resolver may return SERVFAIL, while delv should provide a diagnostic. Capture the actual message rather than assuming the cause.
status=<NOERROR | SERVFAIL | other>
ad_flag=<0 | 1>
delv_result=<secure | insecure | validation failure>
diagnostic=<verbatim tool message>
A SERVFAIL can be consistent with bogus DNSSEC data, but it is not proof of a specific DNSSEC fault. Correlate it with the parent DS, child DNSKEY and RRSIG, validator diagnostics, timestamps, and an ordinary resolution baseline.
Record each scenario explicitly. If validation fails, capture the error message (delv’s failure explanation or the absence of AD flag). A table of outcomes helps clarify:
Condition | Delv/dig Output | Interpretation |
All correct (DS matches, child signed) | A delv validation result is secure, and the approved recursive resolver may set AD. | Secure for the tested chain and observation path. |
DS missing (child signed but no DS) | Normal answer, but no secure chain result; AD is not set on the approved validating resolver. | Child may be signed, but the delegation is insecure. |
DS present but wrong | Local validation fails; a validating resolver may return SERVFAIL. | Repair the exact DS, DNSKEY, signature, or timing fault. |
Unrelated DNS error | NXDOMAIN, NODATA, timeout, or SERVFAIL without chain-specific evidence. | Investigate separately; status alone does not identify DNSSEC. |
Interpret the result carefully. A nonexistent name can produce NXDOMAIN; a missing record type at an existing name can produce a NOERROR response with no answer. SERVFAIL has multiple causes. If a known record begins returning SERVFAIL only after a DS change, DNSSEC is a strong hypothesis, not a verdict. Record the actual query and response, then test the trust links before accepting or rejecting the change.
Exercise failure cases only in the disposable zone
Before using the process on a production name, rehearse failure recovery in a separately delegated, disposable public zone that the team owns. The proposed scenarios below must have approved restoration steps and must not touch a customer domain, a shared KMS key, or an unowned name.
Mismatched DS: Publish a deliberately incorrect digest only in the disposable parent/child pair. Expect a validating path to reject the chain after relevant caches refresh. Restore the exact reviewed DS, confirm it at the parent authority, and obtain fresh validator evidence before proceeding.
Missing parent DS: Omit or remove the DS in the disposable zone. The child can remain signed, but the delegation is insecure and should not produce a secure validation result. Restore the DS, observe the parent authority, wait through the relevant timers, and validate again.
KSK access failure: In a dedicated disposable environment, apply a pre-reviewed policy change that removes only the DNSSEC service principal’s access to the test key. Do not disable, schedule deletion of, or alter a production or shared key. Expect the KSK to enter ACTION_NEEDED. Restore the exact prior policy, reactivate the KSK, and repeat authoritative and resolver checks.
Summarize each in a small table:
Scenario | Trigger | Observed evidence | Recovery step |
Bad DS digest at parent | Parent DS updated with wrong value | Parent-authoritative DS differs from the child-generated value; local validation fails; a validating resolver may return SERVFAIL. | Remove bad DS; re-publish correct DS |
No parent DS | Parent DS omitted or removed | Parent has no DS. The child can still answer with signatures, but the delegation is insecure and no secure validation result exists. | Publish correct DS, wait TTL |
KSK disabled or missing key | Test-only policy removes the DNSSEC service principal’s access to a dedicated test key. | KSK enters ACTION_NEEDED; signing health degrades and validation risk grows as signatures age. | Restore the exact prior policy, reactivate the KSK, and repeat authoritative and validator checks. |
Different zone/NS issue | Unrelated DNS glitch (e.g. NS gone) | Resolution failure without a parent-DS or validator-specific correlation. | Use the ordinary DNS and network runbooks; do not classify it as DNSSEC without evidence. |
Run these scenarios only in the authorized failure zone. For every trigger, preserve the before state, define the repair owner, restore the reviewed configuration, and require fresh parent-authoritative and validator evidence. A recovery is not complete merely because a console status turns green.
Observe cache transitions before expanding the change
Caches can preserve both positive and negative delegation state. AWS preparation guidance recommends lowering the zone maximum TTL to 3,600 seconds before signing, but that recommendation is not an Internet-wide convergence guarantee. The parent DS, delegation NS records, and prior negative answers have their own timers. Record the old values before changing them and treat each wait as an evidence gate.
Keep a timeline:
T=0: Parent operator submits the exact reviewed DS. Record the submission time, parent change identifier or ticket, and the first authoritative observation.
T+sampling interval: Query the parent authority and selected validating paths. Use the same names, tools, endpoints, and evidence fields on every pass:
dig @<PARENT_AUTH_NS> example.com DS +dnssec +noall +answer
The parent answer may appear before all recursive caches refresh. Record when each selected resolver first observes the DS and when it first records a secure result; do not convert the earliest success into a universal convergence claim.
T+observed NS/negative-cache timers: Repeat the parent and validator checks after the longest relevant pre-change timer expires.
T+DS TTL: Requery the selected resolvers. Expiration of the DS RRset TTL is an observation gate, not proof that every resolver worldwide has refreshed.
Also account for records cached before the TTL reduction. The AWS preparation sequence for the SOA TTL and SOA minimum is intended to shorten negative-cache recovery, but an answer already cached under an older value can remain until that older timer expires. Record the old and new values separately.
A short timeline checklist can clarify steps and waits. For example:
Reduce the child zone maximum TTL and negative-cache timers according to the reviewed AWS preparation step, then wait for the previous values to expire before relying on the reduction.
Publish parent DS with TTL=300 (Step 3).
Wait at least the observed parent DS TTL before treating DS removal or replacement as broadly aged out across the sampled resolver set.
Apply any additional buffer as a proposed operating control, document its basis, and keep probing; a fixed extra 600 seconds is not a universal rule.
During this wait, monitor test queries (from multiple locations) to confirm resolver caches are updated.
Do not call the rollout complete because a suggested hour has elapsed. Close the gate only after the relevant previous TTLs have expired, the parent authority shows the exact DS, each approved validation path has fresh evidence, and no unresolved observation gap remains. Record when the first and last sampled paths become secure.
Lowering a TTL affects future cache entries; it does not shorten an answer already cached under the old value. AWS’s one-hour rollback example is preparation guidance tied to a reduced zone maximum TTL. The operating decision still depends on the actual old timers, the parent DS and NS state, and observed validator behavior.
Monitor signing health and resolution separately
Once DNSSEC is on, we need to watch both the signing process and normal DNS resolution. These are separate domains of health. For example, a Route 53 metric or CloudWatch alarm for the KSK status is purely about signing, whereas an application failure could be a plain DNS outage.
For signing health, AWS recommends CloudWatch alarms for DNSSECInternalFailure and DNSSECKeySigningKeysNeedingAction. Route these alarms to the owner who can repair KMS access or KSK state. Query the current KSK state as part of the runbook; an ACTION_NEEDED status requires prompt repair and fresh validation evidence.
For resolution, probe a known record through the approved validating paths and preserve the endpoint, transport, AD result, and local validation result. A timeout, NXDOMAIN, NODATA, or SERVFAIL can have non-DNSSEC causes, so correlate the probe with authoritative answers and application symptoms before paging the owner of a specific layer.
A brief monitoring checklist:
Route 53/DNSSEC metrics:
KSK status (DNSSECKeySigningKeysNeedingAction): security or DNS signing owner.
Internal failures (DNSSECInternalFailure): Route 53/DNS platform owner.
DNS validation probes:
Sample resolution through delv and an approved validating resolver: DNS on-call owner.
Log AD flag or error.
Application health:
App owners monitor that domain lookup succeeds at their stack (separate issue if they see no connectivity, trigger normal DNS/network runbooks).
Network-health signals have a different evidence boundary. Route 53 signing metrics can show key health, and an application probe can show that a name resolved, but neither alone proves that a particular resolver validated the chain. The related discussion of the limits of network-health indicators helps separate reachability evidence from DNSSEC evidence. Keep DNSSEC-specific probes and their sampling limits in the change record.
Hold rollout and repair the failing trust link
If any verification step fails, pause and fix before proceeding. Use a table of symptom / evidence / action to guide this. For example:
Symptom (alert) | Evidence | Action |
KSK status = ACTION_NEEDED | AWS get-key-signing-keys shows Status: ACTION_NEEDED | Restore access to the existing KMS key, reactivate the KSK, and collect fresh signing and validation evidence. |
Dig/resolver SERVFAIL on example.com | delv or another approved validator reports a chain failure; parent DS and child DNSKEY do not match. | Correct the reviewed trust object, confirm it at the parent authority, wait through relevant timers, and revalidate. |
Example.com not resolving at all | Authoritative query returns NXDOMAIN, NODATA, timeout, or an unexpected delegation response. | Investigate ordinary DNS and delegation state before changing DNSSEC objects. |
Unexpected resolver without AD flag | Approved resolver returns no AD flag, while parent and child answers are otherwise available. | Check resolver policy, endpoint, transport trust, cache state, and the parent DS. Do not infer a missing DS from AD=0 alone. |
Always restore the reviewed, correct state rather than work around it. For instance, if a DS was published incorrectly, fix it rather than globally turning off validation. Once you take corrective action, run the same validation tests again to get fresh evidence. Only after seeing the chain pass again would you clear the hold and move forward.
Withdraw trust before disabling signing
For this reviewed single-zone hierarchy, follow AWS’s ordered withdrawal procedure: identify the current DS TTL, remove the parent DS, confirm the authoritative removal, wait through the relevant DS timer, then disable signing and deactivate the KSK. Zones with signed descendants require a broader hierarchy review.
1. Remove the parent DS: The named parent-zone operator, using the exact current DS RRset and approved ChangeResourceRecordSets permission or the registrar’s equivalent control, submits the delete. Preserve the change identifier and the pre-change DS answer.
{
"Comment": "Remove DS for example.com",
"Changes": [
{
"Action": "DELETE",
"ResourceRecordSet": {
"Name": "example.com",
"Type": "DS",
"TTL": 300,
"ResourceRecords": [
{ "Value": "12345 13 2 ABCD1234EF..." }
]
}
}
]
}
aws --region us-east-1 route53 change-resource-record-sets \
--hosted-zone-id Z98765PARENT \
--change-batch file://remove-ds.json
Confirm removal: Query the parent authoritative servers for the DS RRset. If the parent is hosted in Route 53, also wait for GetChange to report INSYNC. Record the first empty parent-authoritative answer and its UTC timestamp.
Wait for the old DS TTL: Keep child signing active while resolvers can still cache the DS. Continue validation probes through the agreed observation set. Use the observed pre-removal DS TTL, registrar schedule, and any documented buffer as change-control inputs.
Disable signing and deactivate the KSK: Only after the parent DS is absent authoritatively and the old DS timer has expired should the authorized Route 53 operator run the following commands:
aws --region us-east-1 route53 disable-hosted-zone-dnssec --hosted-zone-id Z123ABCDE
aws --region us-east-1 route53 deactivate-key-signing-key --hosted-zone-id Z123ABCDE --name my-ksk
Or use the console’s “Disable DNSSEC” page. AWS will ask you to confirm you’ve removed the DS and waited for TTL.
Removing the parent DS first keeps the transition reversible while cached trust ages out. This is not the same as certificate renewal or revocation; TLS certificate lifecycle as a separate trust workflow has different objects, timers, and evidence. Do not use a valid TLS certificate as proof that DNSSEC withdrawal is complete.
Build cloud-architecture foundations for these handoffs
Rolling out DNSSEC across cloud and registrar boundaries depends on networking, identity, security, automation, and reliability fundamentals. Readers building those foundations can review the Refonte Learning Cloud Architecture Program. Its page lists four months and 8–12 hours per week, and it covers AWS, Azure, Google Cloud, cloud networking, identity, reliability, security, Terraform, observability, and disaster recovery. The page does not confirm a dedicated Route 53 DNSSEC or registrar-DS lab, so treat it as a broader architecture learning path rather than a promise of this exact exercise.
Accept the chain with its owners and evidence attached
Complete the change record only after the evidence exists. The entries below are a template, not executed observations:
Zone owner: Record the named team and accountable person.
Hosted zone: Record the authorized zone name and hosted-zone ID.
KMS-backed KSK: Record the approved key alias or ARN reference, region, state, and KSK status without exposing sensitive policy details.
DS comparison: Record the key tag, signing algorithm, digest type, and digest from the active child KSK, then attach the matching parent-authoritative DS answer.
DS TTL and publication time: Record the observed parent DS TTL and the actual UTC timestamp.
Validation evidence: Attach actual delv output, tool version, trust anchor, query mode, resolver endpoint, and UTC timestamp.
Resolver sample: Record each approved resolver tested and whether the result was secure, insecure, or failed.
Observation window: Record the agreed window, detected errors, and known sampling gaps.
Withdrawal or recovery evidence: Record whether the parent DS was retained, corrected, or removed and whether recovery was exercised.
Approve only the tested zone, parent delegation, resolver path, and observation window. The acceptance package must contain the ownership ledger, exact DS comparison, parent-authoritative answer, timestamped validation output, cache timeline, and recovery result. It does not establish that every resolver has refreshed or that future key changes are safe. Repeat the same evidence gates for each KSK, DS, registrar, or parent-zone change.