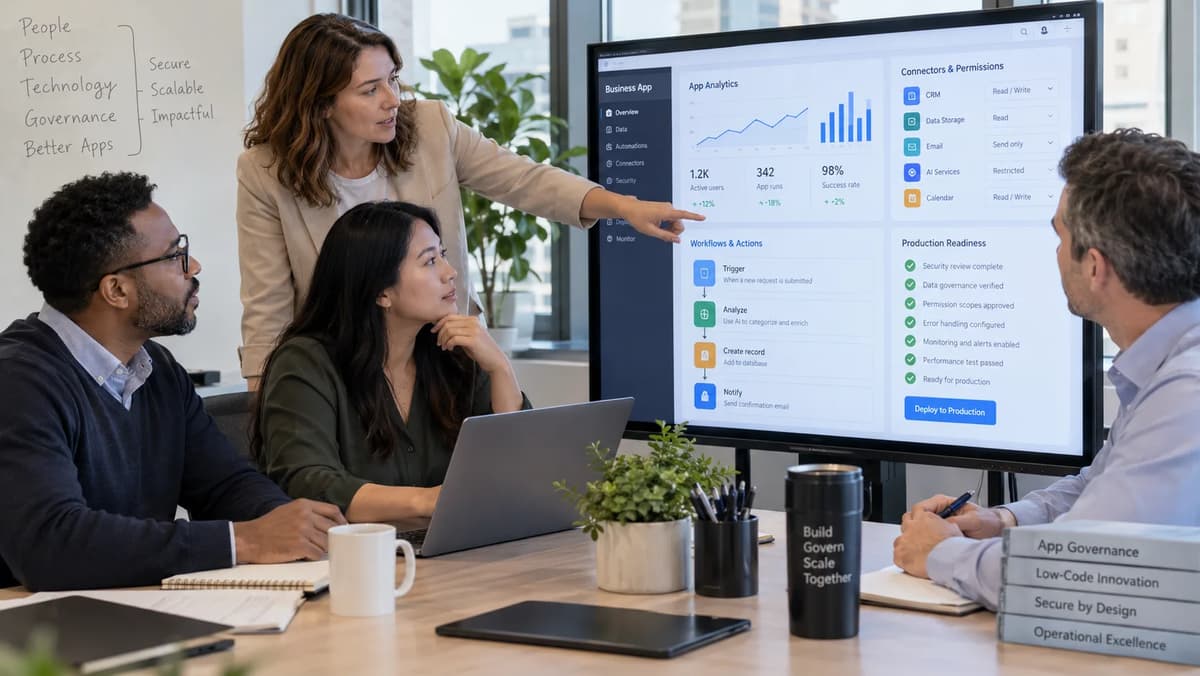
A business analyst can now describe a useful application in a conversation, watch it take shape, and share it before a conventional software intake process would have reached its first architecture meeting. The speed is valuable. The governance problem appears one step later: the app reads operational data, stores records between sessions, invokes an external action, and becomes the team’s daily operating surface before information technology, security, or the data owner knows it exists.
AWS announced Amazon Quick custom applications as generally available on September 1, 2026. General availability makes the capability a supported product choice; it does not create an accountable business owner, validate generated logic, prove authorization boundaries, establish support, or guarantee an exit path. A natural-language app can still become a system of record by accident, inherit an unsuitable connector identity, expose a public surface, or break when a schema changes.
The production decision should therefore look familiar even if the build interface does not. Treat every app as a governed business application with a maker, accountable owner, data and action contract, lifecycle state, test evidence, monitored service level, cost center, incident path, and retirement plan. The objective is not to slow citizen development. It is to make the safe production path clearer and easier than shadow deployment.
What General Availability Changes for Business-Built Apps
The Amazon Quick user guide describes Apps in Quick as interactive web applications built through natural-language conversation. The documented capability set includes user interfaces, embedded Quick Sight visuals, action connectors, built-in AI inference, spaces, and persistent key-value storage. That means the governance unit is not a dashboard. An app can read, calculate, classify, store, and write.
The first control is to separate documented platform behavior from organizational approval. AWS can declare a feature generally available, but the organization must decide whether a specific app is allowed to handle payroll data, write to a customer relationship management system, accept anonymous input, or become a departmental operating record. Production readiness is a property of the use case and controls, not of the vendor lifecycle label.
There is also a current documentation divergence worth preserving. The September 1 launch announcement says app building is available to Plus, Professional, and Enterprise customers. A current getting-started page lists a different set of authoring entitlements, including Author, Professional, Author Pro, Enterprise, and Admin Pro. Public-facing app documentation separately says public apps are available on Free and Plus accounts. Do not invent a single entitlement model from those pages. Capture the actual subscription, account type, Region, and feature availability during the production review and recheck them before each major rollout.
Question | Vendor evidence | Organization decision |
Can the app be built? | GA and current account entitlement | Whether the use case is approved for this platform |
Can it access data? | Quick and connector authorization behavior | Data classification, purpose, minimization, owner approval |
Can it take action? | Registered integration and write capability | Least privilege, human approval, reversibility, audit |
Can it be shared? | Account, limited, or public mechanisms where available | Allowed audience and threat model |
Can it stay in production? | Product availability and version history | Owner, support, tests, monitoring, continuity, retirement evidence |
Acceptance gate: an app cannot move beyond prototype merely because it works in the maker’s session. It moves only when the business owner signs the operating purpose and the control owners can identify the runtime identity, data boundary, write boundary, failure behavior, and recovery path.
Choose Use Cases That Belong in Amazon Quick
Citizen development works best when the risk profile matches the platform and the support model. A request tracker, internal status console, governed analytics front end, or review queue can be a strong candidate when the data and actions are bounded. A public intake that writes to a regulated system, a money-moving approval engine, or a record that must meet stringent transactional guarantees deserves a higher bar and may belong in a conventional application stack.
Do not classify only by business value. Two apps can have the same value and radically different consequences. A sales pipeline viewer that reads approved fields is not equivalent to an app that changes opportunity stages for every seller. An internal training portal is not equivalent to an anonymous public form that accepts personal data. A useful decision rubric scores both the value of the app and the blast radius of a mistake.
Dimension | Lower-risk signal | Escalation signal |
Data sensitivity | Public or low-sensitivity internal data | Personal, financial, regulated, confidential, or privileged data |
Write impact | Read-only or reversible personal state | System-of-record updates, notifications, approvals, financial actions |
Autonomy | Human initiates and confirms each material action | AI or generated logic can choose actions without review |
Audience | Small named internal group | Enterprise-wide, external named users, or anonymous public access |
Availability | Convenience tool with simple fallback | Business process stops when the app is unavailable |
Record ownership | Derived or cached information | App becomes authoritative record |
Compliance | No special retention or legal duties | Retention, legal hold, audit, consent, residency, accessibility duties |
Support burden | Owner can support during business hours | On-call, strict recovery, or cross-department dependency |
Decision rule: promote low and moderate-risk use cases when controls are proportionate and tested; escalate high-impact writes, regulated data, public exposure, and system-of-record behavior to security, data, legal, and application architecture review. Reject only when required controls cannot be implemented or evidenced. That is governed enablement, not a blanket ban.
For analytics-heavy use cases, the adjacent question is whether the app is presenting governed decisions or creating new definitions. Refonte Learning’s discussion of AI and machine learning in BI strategy is useful for the analytics context, but Amazon Quick app governance starts where a visualization becomes an executable business interface.
Create a Maker, Owner, and Application Inventory
The maker is the person who builds or edits the app. The accountable owner is the person who accepts the business risk and keeps the app supportable. Those roles can be held by the same person during a prototype, but production should never depend on that coincidence. A maker can leave, change roles, lose access, or stop maintaining the application while the department continues to rely on it.
Inventory is the control that turns a conversational artifact into an enterprise asset. Record the app before production, not after an incident. The inventory should be searchable by owner, system, connector, data class, sharing mode, risk, cost center, and lifecycle state. If your broader organization already maintains an agent registry, align the fields rather than creating a parallel spreadsheet. Refonte Learning’s AI agent sprawl governance article covers enterprise-wide discovery; this playbook narrows that discipline to Apps in Quick.
Inventory field | Required production content | Why it matters |
Identity | App ID/name, account/workspace, version, environment | Locate the running asset and distinguish copies |
Ownership | Maker, accountable owner, sponsor, support contact | Prevents personal prototypes becoming ownerless systems |
Purpose and users | Business process, audience, criticality, SLA or support expectation | Defines legitimate use and fallback |
Data | Sources, classification, fields, retention, authoritative vs derived | Supports minimization and data-owner review |
Actions | Connectors, operations, scopes, credential model, human approvals | Defines the write blast radius |
State and AI | Persistent tables/keys, AI features, prompt/config version | Makes generated logic and stored state reviewable |
Exposure | Sharing mode, public URL status, legal/privacy review | Makes anonymous exposure visible |
Operations | Logs, metrics, cost center, fallback, review date, retirement date | Supports support, cost control, and exit |
Separate the Builder From the Accountable Business Owner
The owner should be senior enough to accept the consequences of incorrect outputs and broad enough to coordinate data, connector, and support decisions. The owner is not merely the person whose name appears first in a sharing dialog. They approve purpose, audience, data classification, service level, manual fallback, retention, and retirement. Security and IT own control standards; data owners approve sensitive data; action owners approve write authority; the application owner integrates those decisions into one production accountability model.
Maker permissions should also be separated from runtime permissions. A maker may legitimately have broad access while exploring, but the finished app should not need every permission the maker happened to possess. Rebuild or reauthorize integrations to match the declared runtime need. Test with representative users who have ordinary permissions, not only with the maker’s elevated identity.
Define Prototype, Pilot, Production, and Retirement States
State | Entry evidence | Allowed permissions and audience | Exit condition |
Draft | Named maker and purpose | Maker only, non-sensitive sample data | Working concept or deletion |
Prototype | Basic risk classification and inventory record | Synthetic or approved test data, no high-impact writes | Review package complete |
Review | Owner, data/action contracts, threat model where required | Controlled reviewers only | Approvals and tests accepted |
Pilot | Versioned release, monitored users, fallback | Limited real users and least-privilege actions | Pilot outcomes and failure evidence accepted |
Production | Owner, support, tests, monitoring, cost and retirement plan | Approved business audience only | Change review, suspension, or retirement |
Suspended | Incident or control failure recorded | Sharing/actions disabled as needed | Safe version restored or retirement approved |
Retired | Export/deletion and replacement decision | No active users or credentials | Inventory closed with evidence |
Every state needs an owner, environment or copy, permission ceiling, test expectation, and next review date. “Published” is not a lifecycle state by itself. Publication is a technical action; production is an organizational decision backed by evidence.
Govern Data Sources, Connectors, Tools, and Permissions
AWS documents action integrations as the mechanism for apps to read data, write data, or perform operations in external services. The same page distinguishes user authentication, where each viewer uses individual credentials, from service authentication, where a shared administrative credential can serve multiple users if the connector supports it. That distinction changes the threat model.
User authentication usually preserves end-user authorization boundaries more naturally, but it still requires careful consent and negative testing. Service authentication can be appropriate for a controlled shared function, but every app user may effectively gain the reach of the shared credential through whatever actions the app exposes. A narrow UI is not a security boundary if the backend credential is broad and generated logic can call more than intended.
Create a connector contract before production. Treat it like an API contract plus an authorization decision. The contract should name the system, action, read/write class, approved scope, credential owner, consent method, expected rate/usage, idempotency rule, error behavior, audit evidence, revocation procedure, and human approval requirement. If you cannot revoke the credential quickly without destroying unrelated workflows, the design has a containment problem.
Connector contract field | Example decision | Production evidence |
Action | Create a service ticket, not arbitrary API calls | Registered action and test payload |
Scope | Project A tickets only where platform supports scope | Permission capture and action-owner approval |
Credential | End-user OAuth preferred; shared service identity only by exception | Credential owner and expiry/rotation path |
Write policy | Create only; no delete or bulk edit | Negative tests for prohibited operations |
Idempotency | Client-generated request key for retry-safe creation | Duplicate-action test |
Failure handling | No automatic retry on ambiguous write result | Partial-write reconciliation runbook |
Revocation | Disable connector or credential within incident objective | Revocation drill and owner contact |
Human approval | Required before customer, financial, or irreversible action | Recorded approval step and test |
Require Consent and Least Privilege for Action Connectors
Consent is not a one-time click by the maker. Data owners must approve sensitive reads; system owners must approve writes; security must approve shared or unauthenticated outbound paths that cross trust boundaries. Reauthorization after a scope change should be treated as a change event. If an app no longer needs an integration, remove the logical dependency and revoke the underlying credential even if the platform interface does not provide a perfect one-click removal path.
For connector and workflow foundations, Refonte Learning’s guide to no-code AI agents and MCP is useful background on how connectors and AI-callable tools differ. The production rule here is narrower: expose only the action contract the app needs, regardless of how easy the platform makes broader integration.
Test Identity and Authorization From the End User’s View
Authorization tests must use real role combinations. Test an ordinary employee, a manager, a user outside the target group, a user whose connector authorization has been revoked, and a former owner account if your offboarding test environment allows it. Verify both what the interface hides and what the runtime refuses. Conditional visibility generated in the UI can improve usability, but it must not be treated as the only authorization control.
Positive test: the intended user can read the exact approved fields and perform the exact approved action.
Negative test: an unauthorized user cannot read protected data even by changing inputs, filters, URLs, or identifiers.
Revocation test: removing the user or connector permission takes effect within the expected control window.
Privilege drift test: expanding the maker’s access does not silently expand the app’s effective runtime reach.
Service-credential test: every exposed action remains safe when called by the least-trusted approved viewer.
Understand the App Sandbox and Outbound Boundary
AWS’s current security and sandbox documentation says each app runs in a sandboxed iframe and that direct network requests from app code are blocked. External communication is expected to go through the secure bridge API or registered integrations. The same documentation describes restrictions on external resources, link navigation, direct browser file creation, and public-app access to integrations. This is a meaningful boundary, but it should be tested rather than converted into a vague statement that “the app has no network risk.”
The practical threat model has at least three layers. First, generated code inside the sandbox is constrained by the browser policy. Second, approved platform bridges and connectors deliberately cross that boundary. Third, connected services have their own identity, scope, data, rate-limit, and audit behavior. The security review should map those three layers instead of assuming the sandbox either solves everything or permits unrestricted code execution.
Boundary test | Expected result | Evidence to retain |
Direct HTTP request from app code | Blocked by sandbox policy | Test transcript or screen capture |
Unapproved external resource load | Blocked by Content Security Policy | Browser/runtime error evidence |
Approved connector call | Works only through registered integration | Connector registration and successful test |
File export | Uses supported secure download/bridge mechanism | Export test and file validation |
Public app connector call | Unavailable under documented public model | Negative test after public publication |
Revoked integration | Fails safely without stale cached authority | Revocation test and error handling result |
Outbound review should also include the destination, data leaving the platform, authentication, legal/privacy implications, and whether the destination itself can trigger another action. A “controlled bridge” still carries sensitive information if you approve a connector that sends it somewhere inappropriate. Document allowed and blocked paths as test cases, not architecture folklore.
Choose Organizational or Public Sharing Deliberately
Sharing is a security architecture choice. Internal authenticated use starts with an organizational identity and can combine app access, Quick permissions, and connector authorization. Anonymous public use removes that identity and therefore changes what personalization, authorization, storage, abuse prevention, and incident response can rely on.
AWS documents public Apps in Quick as accessible without a Quick account, with shared storage and optional AI inference, while public apps do not support connectors, embedded visuals, embedded chat experiences, or Quick spaces. AI inference usage for a public app counts against the owner’s quota. Public availability is therefore not simply “the same app with a wider audience.” It is a different feature envelope and a different misuse model.
Sharing mode | Identity assumption | Primary risk | Minimum gate |
Named internal users | Authenticated organizational users | Over-broad data or connector authorization | Role tests and least-privilege connector contract |
Organization/account wide | Large authenticated population | Audience creep and unexpected data visibility | Data-owner approval, role coverage, monitoring |
Public/anonymous | No reliable end-user identity | Input abuse, data exposure, shared-state poisoning, quota/cost abuse | Separate threat model, legal/privacy review, rate/usage controls, shutdown drill |
Treat Anonymous Public Use as a Different Security Model
For anonymous use, assume every input is hostile and every shared record can be manipulated within the platform’s exposed behavior. Do not store secrets, private user preferences, internal workflow status, or sensitive identifiers in shared app storage simply because the interface does not display them. Validate size, format, allowed values, and business rules for every input. Consider whether the public app needs persistence at all.
The public-use checklist should cover abuse cases such as automated submission, prompt injection against any AI feature, stored-content poisoning, oversized or malformed values, offensive content, duplicate requests, quota exhaustion, and privacy requests. Establish who can disable public access, how quickly the URL becomes unusable, what data must be preserved for investigation, and what data must be deleted afterward.
Keep Internal Apps Bound to Organizational Identity
For internal apps, use group-based or named access appropriate to the platform and avoid “everyone” sharing as a substitute for requirements discovery. The intended audience belongs in the inventory. Test role changes and offboarding. If the business process requires a stable non-human action identity, make that explicit and scope it independently from the maker. If end-user authorization is the control, prove that the connector acts as the end user and cannot silently fall back to a broader service credential.
No production share until the accountable owner signs the audience.
No public publication of an app designed around internal connector or identity assumptions.
No sensitive shared storage without a documented reason, retention rule, and access model.
No organization-wide sharing merely to avoid maintaining groups or access requests.
Every high-risk app needs a tested “suspend sharing” action in the incident runbook.
Design Persistent App Data and Record Ownership
AWS documents built-in app storage as per-app key-value storage with private and shared scopes, Put/Get/List/Delete operations, 255-character keys, values up to 350 KB, and an INSERT mode that can reject duplicate keys. The documentation also says data persists across sessions, and public anonymous viewers can use shared storage but not private storage.
Those capabilities are enough to create operational dependence. A team can start with bookmarks or preferences, then add approvals, comments, case status, or manually entered customer facts. At that point the data may become authoritative even though nobody made an explicit system-of-record decision. Governance must prevent that drift.
Define whether each table or key family is authoritative, derived, cached, temporary, or user preference data. Assign a schema owner even though the physical store is key-value. Version JSON structures, validate required fields, choose stable keys, and define concurrency behavior at the application level. The sources reviewed document key operations and item limits, but they do not document database-style multi-record transactions, transaction isolation, or platform point-in-time recovery guarantees. Do not assume those properties.
Persistent-data control | Required decision | Test |
Authority | Is this the official record or a derived convenience copy? | Reconcile against authoritative system |
Schema | Version, required fields, type validation, migration rule | Read old and new records after change |
Keys and duplicates | Stable key and INSERT/UPSERT policy | Duplicate submission and retry test |
Concurrency | Conflict detection or last-writer policy | Two-user simultaneous update test |
Retention | Business/legal retention and deletion owner | Age-out/delete test |
Backup/export | Supported export or snapshot process and frequency | Restore/rebuild drill from exported data |
Public shared state | Allowed fields and abuse controls | Anonymous poisoning and deletion test |
Exit | Portable representation and replacement mapping | Import into target or reconstruct sample records |
For governed calculations, do not bury business definitions only inside generated app logic. Reuse an approved semantic source where possible and document the formula when the app must calculate locally. Refonte Learning’s article on semantic layers for AI agents explains why a mathematically correct query can still answer the wrong business question. The same risk applies when an app-generated formula becomes an operational decision rule.
Control AI Inference, Generated Logic, and Human Approval
Natural-language generation creates two kinds of logic that require review: code or configuration generated to implement the app, and AI inference that runs as part of the app’s user experience. The first can introduce ordinary software defects. The second can produce variable output by design. Neither should be trusted merely because the preview looked correct.
Maintain a small decision record for every AI-dependent production feature: purpose, input fields, sensitive-data classification, expected output format, prompt or configuration version, representative test cases, unacceptable outcomes, exception handling, human-review rule, and rollback version. Structured outputs can reduce parsing ambiguity, but they do not prove that a classification or recommendation is substantively correct.
AWS’s app-data documentation adds a useful platform safeguard: when an app uses AI inference and writes to shared storage or through an action connector, each write payload must be reviewed and approved. Preserve that human review for high-impact actions even if future platform options make approval less intrusive. The human should see the material fields, destination, and consequence, not merely an “approve” button with hidden payload details.
AI or generated-logic risk | Control | Acceptance evidence |
Incorrect calculation | Golden input/output tests and independent formula review | Expected and actual results match for boundary cases |
Hallucinated or unsafe content | Constrained inputs, policy checks, human review where impact is high | Adversarial and exception test set |
Prompt/config drift | Version record tied to release | Rollback to prior accepted configuration |
Sensitive-data leakage | Field minimization and output inspection | Tests with representative sensitive values |
AI-triggered write | Explicit payload review and action contract | Human approval event and reconciled write |
Ambiguous confidence | Escalate/ask for clarification instead of forced decision | Low-confidence or conflict scenario test |
For broader deployment context, Refonte Learning’s guide to building AI agents in production addresses agent-level evaluation and operations. An Amazon Quick app should apply the same principle at the application boundary: generated behavior earns production trust through tests and monitored evidence.
Build Functional, Permission, and Failure Tests
A no-code app production checklist that contains only the happy path is not a production checklist. The app must prove what happens when the user is unauthorized, a connector is revoked, a schema changes, a dependency is unavailable, a write partially succeeds, the user retries, shared data is deleted, or the maker leaves. These are the scenarios that distinguish a useful prototype from a supportable application.
Keep a versioned test pack outside the conversational build history. Each test should name the precondition, user role, input, expected visible result, expected data or external action, expected log/evidence, and cleanup. Test data should be synthetic or appropriately protected. A production gate should fail if a critical negative test is unexecuted, not merely if it fails.
Test case | Expected safe behavior | Evidence |
Happy path | Correct result and exactly one intended write | Input/output and external record ID |
Invalid input | Reject or request correction before action | Validation message and no write |
Unauthorized user | No protected data or action | Denied result and audit evidence |
Revoked connector | Clear failure, no stale authority, no silent fallback | Connector error and no external change |
Stale schema | Detect missing/changed field and stop safely | Failure message and preserved original data |
Dependency outage/rate limit | Bounded retry or manual fallback | Retry count, latency, no duplicate |
Partial write | Detect ambiguity and reconcile before retry | Reconciliation record |
Duplicate action | Idempotent or explicit duplicate prevention | One resulting business record |
Public misuse | Input and usage controls limit abuse | Blocked/limited requests and alert |
Data deletion | App handles missing record without recreating unsafe defaults | Deleted state remains deleted |
Maker departure | App still has owner, support, credentials, and access path | Offboarding drill |
Acceptance rule: every material connector and data source needs at least one failure test; every role needs a negative authorization test; every high-impact write needs a duplicate and partial-write test; every production app needs a maker-departure test. These are small investments compared with reconstructing intent during an incident.
Version Changes and Separate Development From Production
Conversational editing is fast enough to make live-editing tempting. Resist it. Production needs a recoverable boundary between the version users depend on and the version a maker is changing. Where the platform supports version history, note stable versions and restore points. Where separate workspaces or app copies are the available separation mechanism, document which object is development, test, pilot, and production.
AWS’s current app guidance explicitly recommends noting stable version numbers so a broken change can be restored. Current limitations also say source-code export is not available, although an app can be duplicated. That portability constraint makes your external version record more important, not less. Record prompts, formulas, integration changes, schema assumptions, screenshots or flow descriptions, test cases, and the accepted production version.
Change class | Required review | Promotion gate |
UI text/layout only | Maker plus owner if business meaning changes | Smoke test and accessibility/readability check |
Calculation or AI prompt | Business owner and logic reviewer | Golden tests and rollback version |
Data source/schema | Data owner plus application owner | Schema compatibility and reconciliation |
Connector scope/action | Action owner and security as required | Least-privilege review and negative authorization tests |
Sharing mode/publication | Owner, security, privacy/legal where public | Threat model and shutdown drill |
Persistent-data schema | Schema owner and support | Migration, concurrency, export/recovery test |
Do not edit live production logic without recovery evidence. For urgent fixes, record the incident, make the smallest change, test the failed scenario and critical regression paths, then preserve both the prior version and the new release note. “The agent changed it for me” is not a change record.
Monitor Usage, Errors, Data Quality, Cost, and Adoption
Monitoring should answer four questions: Is the app being used by the intended population? Is it functioning correctly? Is it changing data safely? Is it worth the ongoing cost and support burden? A simple page-view count is not enough for an app that can call AI inference or external systems.
Define metrics before pilot so the baseline is not invented after success or failure. Useful signals include active users, run or action counts, error rate, connector authentication failures, denied access, data-quality exceptions, AI invocation volume, write actions, latency, public usage, cost, owner changes, abandoned apps, and the business outcome the app was meant to improve. Where the platform does not expose a built-in metric, use supported logs or a carefully designed app-level counter without turning shared storage into a sensitive telemetry dump.
Cost governance should work at the application level. Assign a cost center and budget owner, separate normal usage from public or AI-driven spikes, and define a response when spend exceeds an agreed envelope. Refonte Learning’s agentic AI cost governance article covers the broader problem of variable agent spend; an app-level control should translate that into usage, quota, and business-value decisions for one application.
Metric | Owner question | Trigger example |
Active users / intended users | Is adoption real and appropriately scoped? | Unexpected audience or prolonged inactivity |
Errors and connector failures | Is the app reliable and are credentials healthy? | Sustained error increase or auth failures |
Denied access | Are role rules working or confusing users? | Spike after permission/schema change |
Write volume and duplicates | Is the action path behaving as designed? | Unexpected bulk changes or duplicate creations |
Data-quality exceptions | Are source assumptions still valid? | Missing fields or reconciliation failures |
AI usage and latency | Is inference necessary, usable, and within quota? | Quota pressure, latency regression, abnormal public use |
Cost per business outcome | Is value proportional to ongoing cost? | Cost rises without adoption/outcome improvement |
Owner/review status | Is the asset still governed? | Owner leaves or review date expires |
Adoption is not an unconditional success metric. An app can be popular because it bypasses a control, or unpopular because the workflow is unnecessary. Review value together with error, risk, and support evidence at pilot exit and at scheduled production reviews.
Respond to Incidents and Revoke Access Quickly
An incident involving a citizen-built app is still an application incident. The response team needs a containment path that does not depend on finding the original maker. The inventory should identify the accountable owner, connector owner, data owner, support contact, sharing mode, stable version, and manual fallback before anything goes wrong.
Containment actions should be granular. Depending on the event, suspend sharing, change public access to restricted, revoke a connector, disable a high-impact action, restore a stable version, or disable the whole app. Preserve evidence before destructive cleanup when security, privacy, fraud, or regulatory review may follow. If an external system was modified, reconcile the actual records, not merely the app logs.
Incident signal | First containment | Recovery evidence |
Unauthorized data exposure | Suspend sharing and revoke affected access | Audience review, access logs, corrected permissions |
Bad or duplicate writes | Disable action/connector | List of affected records and reconciliation |
AI-generated harmful content | Disable inference or action path | Test reproduction, prompt/config rollback |
Public abuse or quota spike | Revoke public access | Usage review, blocked URL, cost/quota assessment |
Schema/dependency break | Restore safe version or manual fallback | Compatibility fix and regression tests |
Maker offboarding gap | Transfer ownership and credentials | New owner, support contact, access test |
Suspend the smallest surface that stops harm: sharing, public access, connector, action, or app.
Preserve relevant logs, versions, connector details, payloads, and timestamps according to policy.
Notify the application owner, data owner, action-system owner, security, privacy, or legal teams as the incident requires.
Reconcile external writes and persistent app data against authoritative systems.
Restore a previously accepted version or move users to the documented manual fallback.
Run the failed test plus critical regression tests before reopening access.
Record root cause, control changes, owner actions, and whether the app remains fit for production.
Access revocation is part of incident readiness. Test it during the pilot. If you cannot disable a connector or public surface within the required response objective, the app is not ready for a high-impact business process.
Plan Portability, Export, Replacement, and Decommissioning
No-code reduces the amount of conventional source code you own, but it does not remove vendor dependency. Current Apps in Quick limitations state that app source code cannot be downloaded, while duplication is supported. That means portability has to be designed around business logic and data artifacts, not a promise that you can export a repository later.
Keep a portability packet outside the app: business purpose, user journeys, prompts and generation instructions, formulas, data schemas, connector contracts, permissions, sample data, expected outputs, screenshots or flow maps, test cases, current owners, exports, and the replacement plan. A competent builder should be able to recreate the critical workflow on another platform from that packet without interviewing the original maker.
Exit artifact | Minimum content | Retirement proof |
Purpose and user flow | Who uses it, trigger, decisions, outputs | Replacement covers required business path |
Logic | Prompts, formulas, rules, AI configuration assumptions | Representative outputs reproduced elsewhere |
Data | Schema, authority, retention, export format | Final export reconciled and deletion completed |
Integrations | Systems, actions, scopes, credentials, owners | Credentials revoked and external subscriptions removed |
Permissions | Audience, groups, public status | No remaining access or public URL |
Tests | Critical happy, negative, failure, and recovery cases | Replacement passes accepted test set |
Operations | SLA/support, alerts, cost center, fallback | Monitoring and budget moved or closed |
Ownership | Maker, owner, sponsor, support team | Inventory marked retired with approver and date |
Decommission in a controlled sequence: freeze new changes, identify active users, export required data, reconcile authoritative records, move users to the replacement or manual process, revoke connectors and public access, delete or archive app data according to policy, remove credentials, stop cost-bearing dependencies, and close the inventory record with evidence. Do not leave a retired app “just in case” with live credentials.
Platform churn is one reason to do this work before you need it. The asset is portable when its purpose, data, permissions, tests, and dependencies are understandable outside the builder. The goal is not perfect vendor neutrality. It is the ability to continue the business process and shut the old surface down safely.
Launch a 60-Day Governed App-Building Program
A rollout should make approved building easier than shadow deployment. Do not begin with a large policy document and no practical path. Begin with a small maker cohort, pre-approved use-case classes, inventory and connector templates, a security/data review lane, and a production gate that is fast for low-risk apps and deeper for public, sensitive, or high-impact apps.
The first 60 days should produce evidence that the organization can govern the lifecycle, not a target number of apps. A successful pilot ends with at least one app promoted through the full process, one intentionally rejected or redesigned use case, an incident drill, a retirement exercise, and clear metrics for maker effort, reviewer effort, support burden, cost, adoption, and business value.
Days | Focus | Required output |
1-10 | Policy and scope | Approved use-case classes, prohibited/high-risk triggers, lifecycle states, owner model, inventory template |
11-20 | Maker enablement | Training on data classification, connector contracts, public-sharing rules, tests, change records, support and exit |
21-30 | Prototype cohort | Three to five bounded apps using synthetic or approved low-risk data; inventory created at prototype stage |
31-40 | Security/data/action review | Least-privilege connector approvals, sandbox boundary tests, data-state decisions, public-use restriction unless explicitly reviewed |
41-50 | Pilot and monitoring | Limited real users, stable versions, dashboards/metrics, cost ownership, manual fallback, negative and failure tests |
51-55 | Incident drill | Suspend sharing, revoke connector/action, preserve evidence, reconcile writes, restore safe version |
56-60 | Value and retirement review | Promotion decisions, cost/adoption review, maker-departure test, export/replacement and decommission exercise |
Day-60 production acceptance should require all of the following: a named maker and accountable owner; approved audience and sharing mode; data-owner and action-owner approvals where required; documented sandbox/outbound assumptions tested against allowed and blocked paths; persistent-data authority and recovery decision; versioned logic and AI tests; negative authorization and failure tests; monitoring and cost ownership; incident and revocation drill; support fallback; and portability plus retirement evidence.
Measure reviewer throughput too. If low-risk apps wait weeks for a security committee, users will route around the process. Use risk tiers, reusable templates, approved connector patterns, and office hours to keep safe paths fast. Reserve full threat modeling and cross-functional approval for the cases that actually need it, especially public exposure, sensitive data, shared service credentials, and high-impact writes.
The durable skill is not prompt phrasing. It is learning to translate a business process into bounded data, actions, human decisions, tests, and measurable outcomes. The same foundations transfer across no-code platforms. Refonte Learning’s program is not presented here as Amazon Quick training; its verified value is the adjacent foundation in workflow design, integrations, safety, human review, and return-on-investment thinking.
Natural-language business applications should lower the cost of solving small operational problems without lowering the standard for production accountability. The right governance model does not force every departmental app through the same process as a public banking system, and it does not let a useful prototype become permanent infrastructure simply because nobody stopped it.
Make the safe route easier: approved patterns, clear ownership, fast review for low-risk use cases, reusable connector contracts, versioned tests, monitoring templates, and a simple retirement checklist. Then keep the production rule non-negotiable. Every production Amazon Quick app needs an accountable owner, least-privilege data and actions, a deliberate sharing model, tested persistent-state assumptions, validated generated logic, failure and authorization tests, monitoring, support, cost ownership, incident containment, and evidence that the process can survive the maker and the platform.
For builders who want structured practice with transferable no-code workflow foundations, the Refonte Learning AI Agents (No-Code) Program currently lists Zapier, Make, n8n, Microsoft Copilot Studio, Custom GPTs, Claude Projects, Gmail, Slack, Notion, Sheets, CRM integrations, safety, human review, and ROI thinking. The live curriculum does not explicitly list Amazon Quick, its app sandbox, public sharing, persistent app data, or AWS-specific governance. Use the program for the verified integration and human-review foundations; keep Amazon Quick production controls tied to current AWS documentation and your own operational evidence.