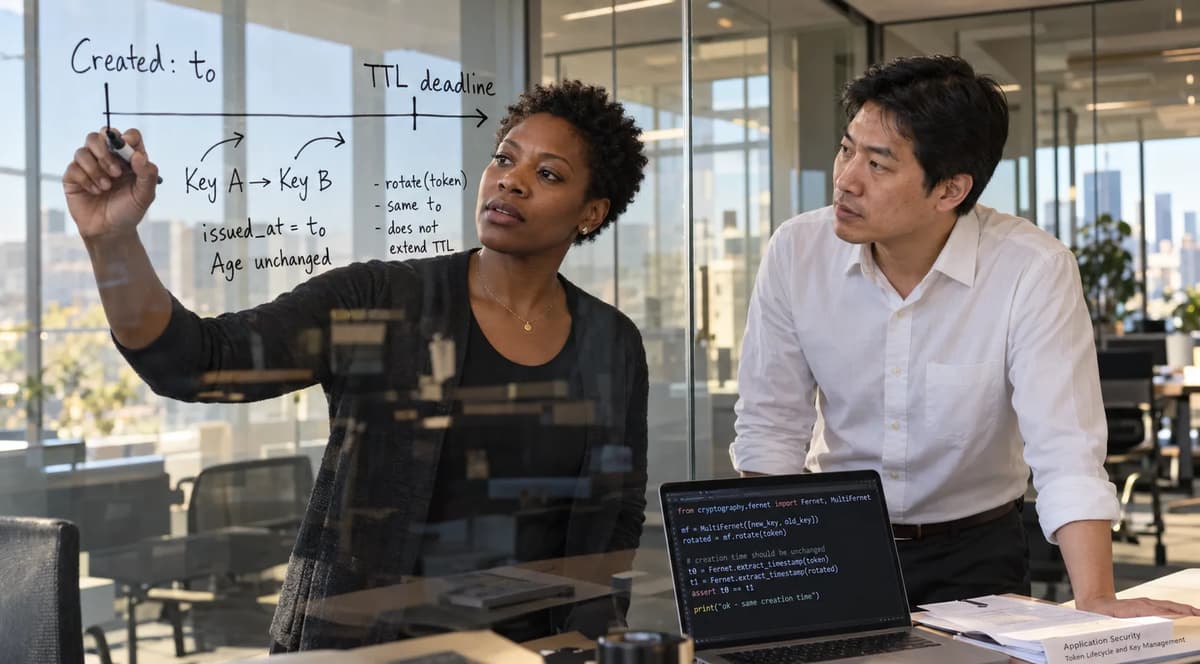
A useful Fernet rotation review starts with a deceptively simple failure: the new key can decrypt a token produced by MultiFernet.rotate(), yet the application still rejects that token when it applies the same TTL it used before rotation. That is not contradictory behavior. It is what should happen when rotation changes key protection but preserves the token’s authenticated creation timestamp.
The practical review question is therefore not “did the bytes change?” It is: which authenticated timestamp does the consumer use after actual re-encryption, and does its age decision remain unchanged under the same TTL? Cryptography’s Fernet documentation states that MultiFernet.rotate() preserves the original token timestamp, while decrypt(..., ttl=...) considers message age only when a TTL is supplied.
This playbook isolates those contracts with one Python process, fresh owned keys, an authored 23-byte payload and synthetic Unix times. The supplied preparation run used Python 3.12.14 and cryptography 50.0.2 and completed eleven controlled cases. Those cases qualify only the behavior tested here. Labels such as ADMIT_AGE_CHECK, ROTATED_NOT_RENEWED and NEW_ISSUANCE_REQUIRES_POLICY are experimental decisions, not authorization, session renewal, replay protection, global key-retirement approval or evidence about a production service.
The central result is narrow and operationally important: Fernet rotation preserves age relative to the original authenticated timestamp. The consumer, not the token format, supplies the maximum-age policy.
State the age contract before evaluating rotation
The selected contract is straightforward: a token is eligible for this bounded age decision only when it authenticates successfully and the consumer evaluates it with the declared TTL and comparison time. Fernet version 0x80 stores a 64-bit unsigned big-endian Unix timestamp in the token. The format contains version, timestamp, IV, ciphertext and HMAC fields; it contains no stored TTL field. The HMAC covers the version, timestamp, IV and ciphertext, so the timestamp is visible but authenticated. The Fernet specification is the relevant format authority, with the supplied preparation retaining the raw source.
The expiration rule therefore does not travel as a self-contained “expires at” field inside these fixture tokens. Cryptography’s documented decrypt(token, ttl=None) API says that ttl is optional; when it is supplied, messages older than that number of seconds are rejected, and when it is omitted or None, age is not considered. The consumer owns that maximum-age argument.
That differs from the separate question explored in Refonte Learning’s article on JWT expiration requirements, where the review boundary concerns requiring and validating a JWT exp claim. The Fernet fixture here does not test missing claims or JWT decoder profiles. Every freshly created Fernet fixture token has its format timestamp; this experiment asks what happens to that authenticated timestamp during re-encryption.
Separate cryptographic validity from permission to act
Three decisions must remain separate. First, cryptographic processing can establish that the holder of an appropriate Fernet key can authenticate and recover the expected plaintext. Second, a consumer can decide that the authenticated timestamp falls within its supplied TTL. Third, an application can decide whether a person, session or operation is permitted to do something.
The fixture reaches only the first two boundaries. ADMIT_AGE_CHECK means the controlled age test accepted the token and recovered the exact authored payload. It does not mean “authorize this user,” “renew this session” or “approve this transaction.” No service principal, customer identity, endpoint or business action exists in the laboratory.
Freeze the implementation and source baseline
The source baseline matters because the equality boundary is implementation-specific evidence, not a slogan to project onto every future package version. The supplied preparation run identifies Python 3.12.14, cryptography 50.0.2, Linux 6.18.57-x86_64-with-glibc2.39, and a cryptography backend reporting OpenSSL 4.0.3 29 Sep 2026. Those are measured identities for that run, not a claim that every Python installation or every cryptography wheel uses the same backend.
The rolling stable Fernet documentation was consulted for version 50.0.2. It documents rotate() as re-encrypting under the first MultiFernet key while preserving the timestamp saved with the original token. It also documents that decrypt() considers age only if ttl is supplied, that extract_timestamp() verifies the signature before returning the timestamp, and that InvalidToken covers several invalidity classes. rotate() was added in cryptography 2.2; encrypt_at_time() and decrypt_at_time() were added in 3.0 for expiration testing. None of those version introductions is a 2026 launch claim.
The pinned source for cryptography 50.0.2 provides the implementation baseline. In that snapshot, MultiFernet.rotate() authenticates/decrypts candidate input with time_info=None, then calls the first Fernet instance’s encryption path with the same parsed timestamp and a new random IV. The same source checks expiration with:
timestamp + ttl < current_time
That strict inequality means equality remains accepted on this pinned implementation: when timestamp + ttl == current_time, that particular rejection condition is false.
The retained SHA-256 supplied for that source snapshot is dac2c23ce99e8e13956ee75c4b742c3353c8b876f109e45c46d5a49dc437982a. The source inspection explains the expected boundary, while the fixture itself deliberately uses public APIs. If a later package behaves differently, the right response is to record the later runtime and investigate the contract change or wrapper difference, rather than silently rewrite the 50.0.2 oracle.
Build the controlled clock and plaintext oracle
The laboratory fixes four values before decryption:
· ISSUED = 1700000000
· TTL = 60
· PAYLOAD = b'owned-fixture:record-17'
· comparison ages of 59, 60 and 61 seconds
The acceptance oracle is literal rather than derived from whatever the library happens to return. At age 59 the expected result is ACCEPT; at age 60 the expected result is also ACCEPT; at age 61 the expected result is REJECT. On every accepted path, the plaintext must equal the authored byte string exactly. Before each age case, extract_timestamp() must authenticate the token and return exactly 1700000000.
That distinction prevents a weak test from turning “no exception occurred” into the definition of success. F01 through F03 establish the original-token boundary first. F05 through F07 later repeat the same oracle against rotated bytes. If the rotated token suddenly became acceptable at age 61 merely because it had been re-encrypted, the experiment would fail.
A 60-second TTL is useful here because it creates an easily reviewed boundary without waiting for real time to pass. It is not production TTL guidance. No conclusion about session lifetime, credential sensitivity, user experience or business risk can be derived from choosing 60 for a deterministic unit-style security control.
Keep synthetic Unix time inside the laboratory
Python’s time.time() returns seconds since the epoch and can return a lower value than an earlier call if the system clock is adjusted backward. By contrast, time.monotonic() cannot go backward, but its reference point is undefined and only differences between readings are meaningful. The Python 3.12 time documentation explains these clock behaviors.
That distinction matters because a Fernet issuance timestamp is an epoch timestamp, not an elapsed-duration counter from an arbitrary monotonic origin. A monotonic clock is excellent for many local duration measurements, but it cannot simply replace the token’s Unix timestamp domain.
Cryptography’s explicit-clock APIs are intended to support expiration tests and warn callers to pass the real int(time.time()) outside testing. This fixture therefore keeps synthetic values inside the test. It does not manipulate the host clock, sleep for 61 seconds, test NTP behavior, or qualify future-skew handling.
Run the complete eleven-case fixture
The preparation evidence uses one process, fresh owned Fernet keys, no service and no external endpoint. To reproduce it in a disposable Linux environment, save the source as security_fernet_fixture.py in an owned writable directory and use a compatible interpreter with the pinned package:
python3 -m venv .venv
.venv/bin/python -m pip install 'cryptography==50.0.2'
.venv/bin/python security_fernet_fixture.py > security_fernet_results.json
Those commands describe a reproduction. They are not an assertion that dependency installation occurred during the supplied measured run; the dependency was already installed there.
The supplied fixture SHA-256 for UTF-8/LF source bytes including the final newline is:
d38e031381ff0a65f58e96576ce70f5c3393e4622ae532c3b210b90dc4ee5485
The complete authored fixture is:
"""Owned Fernet rotation/age controls; fixed times are for testing only."""
import base64, hashlib, json, platform, sys
from datetime import datetime, timezone
from pathlib import Path
import cryptography
from cryptography.fernet import Fernet, InvalidToken, MultiFernet
from cryptography.hazmat.backends import default_backend
ISSUED, TTL = 1_700_000_000, 60
PAYLOAD = b'owned-fixture:record-17'
ROWS = []
def require(ok, label):
if not ok:
raise RuntimeError(label)
def digest(data):
return hashlib.sha256(data).hexdigest()
def rejected(operation):
try:
operation()
except InvalidToken:
return True
return False
def record(case, observation, decision):
ROWS.append({'case': case, **observation, 'decision': decision, 'status': 'PASS'})
def age_case(case, label, reader, token, when, expected):
timestamp = reader.extract_timestamp(token)
require(timestamp == ISSUED, case + ' authenticated timestamp')
try:
plaintext = reader.decrypt_at_time(token, TTL, when)
except InvalidToken:
observed = 'REJECT'
else:
require(plaintext == PAYLOAD, case + ' exact plaintext')
observed = 'ACCEPT'
require(observed == expected, case + ' expected TTL result')
record(case, {'token': label, 'token_sha256': digest(token),
'authenticated_timestamp': timestamp, 'current_time': when,
'age_seconds': when - timestamp, 'ttl_seconds': TTL,
'expected': expected, 'observed': observed},
'ADMIT_AGE_CHECK' if observed == 'ACCEPT' else 'REJECT_AGE_CHECK')
def run():
old, new = Fernet(Fernet.generate_key()), Fernet(Fernet.generate_key())
original = old.encrypt_at_time(PAYLOAD, ISSUED)
original_digest = digest(original)
age_case('F01', 'original', old, original, ISSUED + 59, 'ACCEPT')
age_case('F02', 'original', old, original, ISSUED + 60, 'ACCEPT')
age_case('F03', 'original', old, original, ISSUED + 61, 'REJECT')
ring = MultiFernet([new, old])
rotated = ring.rotate(original)
require(new.extract_timestamp(rotated) == ISSUED, 'Rotation preserves timestamp')
require(new.decrypt(rotated) == PAYLOAD, 'New key reads rotated payload')
require(rejected(lambda: old.decrypt(rotated)), 'Old key alone rejects rotated token')
require(digest(original) == original_digest, 'Original token remains unchanged')
record('F04', {'original_sha256': original_digest, 'rotated_sha256': digest(rotated),
'authenticated_timestamp': ISSUED, 'plaintext_matches': True,
'new_key_accepts': True, 'old_key_rejects': True}, 'ROTATED_NOT_RENEWED')
age_case('F05', 'rotated', new, rotated, ISSUED + 59, 'ACCEPT')
age_case('F06', 'rotated', new, rotated, ISSUED + 60, 'ACCEPT')
age_case('F07', 'rotated', new, rotated, ISSUED + 61, 'REJECT')
require(new.decrypt(rotated) == PAYLOAD, 'No-TTL control still decrypts')
record('F08', {'token': 'rotated', 'ttl_argument': None,
'plaintext_matches': True, 'policy_time_for_comparison': ISSUED + 61,
'time_passed_to_decrypt': False}, 'NO_AGE_DECISION')
# A distinct issuance counterexample, not an authorized renewal workflow.
reissued = new.encrypt_at_time(PAYLOAD, ISSUED + 61)
require(new.extract_timestamp(reissued) == ISSUED + 61, 'Reissue uses a new timestamp')
require(new.decrypt_at_time(reissued, TTL, ISSUED + 61) == PAYLOAD,
'Newly issued control is accepted at its issuance time')
record('F09', {'authenticated_timestamp': ISSUED + 61, 'current_time': ISSUED + 61,
'age_seconds': 0, 'plaintext_matches': True,
'token_sha256': digest(reissued)}, 'NEW_ISSUANCE_REQUIRES_POLICY')
wrong_order = MultiFernet([old, new]).rotate(original)
require(old.extract_timestamp(wrong_order) == ISSUED, 'Old-primary timestamp')
require(old.decrypt(wrong_order) == PAYLOAD, 'Old primary still encrypts')
require(rejected(lambda: new.decrypt(wrong_order)), 'New key rejects old-primary output')
record('F10', {'primary': 'old', 'authenticated_timestamp': ISSUED,
'old_key_accepts': True, 'new_key_rejects': True}, 'REPAIR_PRIMARY_ORDER')
damaged = bytearray(base64.urlsafe_b64decode(rotated))
damaged[8] ^= 1 # Change one timestamp byte without changing the authenticating tag.
tampered = base64.urlsafe_b64encode(damaged)
require(rejected(lambda: new.extract_timestamp(tampered)), 'Reject unauthenticated timestamp')
require(rejected(lambda: ring.rotate(tampered)), 'Reject rotation of tampered token')
record('F11', {'timestamp_extraction_rejected': True, 'rotation_rejected': True,
'exception_type': 'InvalidToken'}, 'REJECT_TAMPERED_CONTROL')
require([r['case'] for r in ROWS] == ['F%02d' % i for i in range(1, 12)], 'Case inventory')
return {'original_unchanged': digest(original) == original_digest,
'payload_sha256': digest(PAYLOAD)}
if name == '__main__':
report = {'started_utc': datetime.now(timezone.utc).isoformat(),
'python': platform.python_version(), 'platform': platform.platform(),
'cryptography': cryptography.__version__,
'openssl_backend': default_backend().openssl_version_text(),
'source_sha256': digest(Path(__file__).read_bytes()),
'issued_at': ISSUED, 'ttl_seconds': TTL, 'cases': ROWS,
'scope': 'Owned random keys, synthetic epoch times, no service or business operation.'}
try:
report.update(run(), status='PASS_11_CASES')
code = 0
except Exception as error:
report.update(status='HOLD', error=type(error).__name__, detail=str(error))
code = 1
report['finished_utc'] = datetime.now(timezone.utc).isoformat()
print(json.dumps(report, indent=2))
sys.exit(code)
The supplied preparation execution started at 2026-10-31T07:12:00.170299+00:00 and finished at 2026-10-31T07:12:00.189461+00:00, with exit status 0 and overall status PASS_11_CASES. That short interval identifies the run; it is not a performance benchmark.
Its measured environment was Python 3.12.14, cryptography 50.0.2, Linux-6.18.57-x86_64-with-glibc2.39, and an OpenSSL backend string of OpenSSL 4.0.3 29 Sep 2026. The result ledger is intentionally concise:
Case | Controlled condition | Expected and observed result | Bounded decision |
F01 | Original, age 59, TTL 60 | Exact payload accepted; timestamp 1700000000 | ADMIT_AGE_CHECK |
F02 | Original, age 60, TTL 60 | Exact payload accepted at equality | ADMIT_AGE_CHECK |
F03 | Original, age 61, TTL 60 | InvalidToken | REJECT_AGE_CHECK |
F04 | Rotate with [new, old] | Timestamp preserved; new key reads; old key alone rejects; original unchanged | ROTATED_NOT_RENEWED |
F05 | Rotated, age 59, TTL 60 | Exact payload accepted | ADMIT_AGE_CHECK |
F06 | Rotated, age 60, TTL 60 | Exact payload accepted at equality | ADMIT_AGE_CHECK |
F07 | Rotated, age 61, TTL 60 | InvalidToken | REJECT_AGE_CHECK |
F08 | Rotated, decrypt with omitted TTL | Exact payload returned; no current-time argument supplied | NO_AGE_DECISION |
F09 | New issuance at 1700000061 | Timestamp becomes 1700000061; accepted at age zero | NEW_ISSUANCE_REQUIRES_POLICY |
F10 | Rotate with [old, new] | Old key reads; new key alone rejects; timestamp unchanged | REPAIR_PRIMARY_ORDER |
F11 | Alter one timestamp byte without authenticating it | extract_timestamp and rotate both raise InvalidToken | REJECT_TAMPERED_CONTROL |
“PASS” means each observation matched the predefined oracle, including controls designed to reject. It does not endorse omitted TTLs, reverse key order or automatic reissuance.
Retain a complete report before accepting the reproduction
A reproduction should be qualified only when the process exits zero, the final status is PASS_11_CASES, the ordered inventory is exactly F01 through F11, and the report records the runtime/source identities expected for that reproduction. HOLD, missing JSON, truncated output or a missing case means the qualification evidence is incomplete.
The fixture uses require() calls rather than removable Python assert statements. Inside the protected run() path, an unexpected exception produces HOLD and a nonzero exit. A failure before report construction can still prevent usable JSON, so an empty or partial result file must never be interpreted as a green run.
The per-token SHA-256 values are labels for random artifacts, not golden outputs. Fresh keys and fresh IVs mean a valid rerun should ordinarily produce different token bytes and therefore different token hashes. By contrast, the supplied source digest identifies particular fixture bytes. Even that digest proves only which source bytes are being referenced; a digest by itself does not prove that execution occurred.
Establish the original token’s three age outcomes
F01 through F03 create the control boundary before any rotation occurs. Each case first calls extract_timestamp() and requires the authenticated timestamp to equal 1700000000. On successful decryption paths, the returned bytes must equal b'owned-fixture:record-17' exactly.
At ISSUED + 59, F01 accepts. At ISSUED + 60, F02 also accepts. The pinned 50.0.2 source explains that boundary: the age rejection predicate is timestamp + ttl < current_time, so equality is not rejected.
At ISSUED + 61, F03 receives InvalidToken. In this controlled case, the token and key are already known-good and only the comparison time changed, so the fixture can legitimately associate that observation with the over-TTL condition it designed. That reasoning should not be generalized to arbitrary production InvalidToken exceptions. Cryptography documents InvalidToken as a shared exception for multiple conditions, including excessive age, malformed tokens and invalid signatures.
The three cases therefore establish the baseline consumer policy: 59 accepted, 60 accepted, 61 rejected.
Prove which key protects the rotated artifact
F04 performs the actual re-encryption:
MultiFernet([new, old]).rotate(original)
The order is material. Cryptography documents that MultiFernet performs encryption operations using the first key in the list and tries available keys for decryption. rotate() specifically re-encrypts the token under that primary key while preserving the original timestamp.
The fixture requires four separate observations. The new key must authenticate and return timestamp 1700000000; the new key must decrypt the rotated artifact to the exact authored payload; the old key by itself must reject the rotated bytes; and the original token digest must remain unchanged. Together, those observations justify the narrow decision ROTATED_NOT_RENEWED.
A changed fingerprint alone would not prove any of this. Ciphertext can change for several reasons. The stronger evidence is key-specific: new-only positive, old-only negative, exact plaintext recovery and retained authenticated timestamp.
The same discipline appears in a different domain in Refonte Learning’s guide to encrypted-data migration and key dependencies: key-related operations have to be tested against the contract they are supposed to change, rather than inferred from a routing or identifier change. The present experiment is narrower and local: Fernet re-encryption genuinely occurs, and the review target is the surviving age metadata.
Bound the old-key rejection to this token
The old key’s inability to decrypt the rotated artifact is not evidence that the old key has become useless globally. The original token remains unchanged and remains an old-key artifact. Other copies could also exist.
F04 therefore says nothing about revocation, complete migration, secure deletion or global retirement. It qualifies one rotated token. Moving from “old key cannot read this new artifact” to “old key can be retired everywhere” would require inventory and lifecycle evidence that this fixture intentionally does not collect.
Repeat the same TTL test after rotation
F05, F06 and F07 repeat exactly the earlier age experiment against the rotated token using the new key. Their result is the clearest answer to the article’s central question:
Age | Original token | Rotated token |
59 seconds | F01: ACCEPT | F05: ACCEPT |
60 seconds | F02: ACCEPT | F06: ACCEPT |
61 seconds | F03: REJECT | F07: REJECT |
The ciphertext is different, the protecting primary key is different, but the authenticated timestamp is still 1700000000. Therefore the same TTL and the same comparison times produce the same age decisions.
This is the operational meaning of Fernet rotation preserves timestamp. MultiFernet.rotate() does not receive a TTL argument, and in the pinned 50.0.2 implementation it decrypts the candidate token with time_info=None before re-encrypting with the original parsed timestamp. The public documentation independently states that rotation preserves the originally saved timestamp.
That also explains a frequently surprising but valid sequence: rotate() can successfully re-encrypt a token that the same application would reject under TTL=60 at age 61. Rotation success does not disable authentication, nor does it make the token younger. It answers a key-protection question; the later consumer call answers an age-policy question.
Recognize a decode that makes no age decision
F08 calls:
new.decrypt(rotated)
There is no TTL argument. The exact plaintext is returned, which proves that the token authenticates under the new key and decrypts correctly. It does not prove that an age policy passed.
That distinction is directly documented. Fernet.decrypt(token, ttl=None) treats ttl as optional; if no TTL is provided, “the age of the message is not considered.” The pinned source similarly sets time_info = None when ttl is None, bypassing the age comparisons while still proceeding to signature verification and decryption.
The bounded decision is therefore NO_AGE_DECISION, not ADMIT_AGE_CHECK. Omitting TTL does not strip authentication, alter the timestamp or renew the token. It simply means that this invocation asked for no maximum-age evaluation.
For a reviewer, that difference is consequential. If the intended consumer contract requires age enforcement and the code path calls decrypt() without TTL, the defect is in the consumer’s missing policy input. Removing TTL must not be proposed as a compatibility fix for an over-age token, because it changes the policy being evaluated rather than repairing rotation.
Read the comparison time without inventing an argument
F08 records policy_time_for_comparison = ISSUED + 61 only so the report can be read alongside F07. It also records time_passed_to_decrypt = False.
Those fields must be interpreted literally. The synthetic 1700000061 value was not passed into new.decrypt(rotated), and no TTL was passed either. Therefore F08 contains no result about whether the library would admit or reject that token at a particular time. It proves authenticated no-TTL decryption and nothing more about age.
Treat a new issuance as a separate policy event
F09 is deliberately not another rotation. It calls:
new.encrypt_at_time(PAYLOAD, ISSUED + 61)
The resulting token authenticates with timestamp 1700000061, and a TTL check at that same comparison time accepts it at age zero. That is expected because a newly generated Fernet token records the timestamp passed at generation. The Fernet format defines the timestamp as the token-creation time, and encrypt_at_time() documents that the supplied current_time becomes the timestamp embedded in the token.
The comparison at 1700000061 is therefore revealing:
Artifact | Authenticated timestamp | Age at 1700000061 | TTL 60 result |
Rotated original | 1700000000 | 61 | REJECT |
Explicit new issuance | 1700000061 | 0 | ACCEPT |
The payload bytes are identical, but the issuance events are not. Rotation preserves the earlier issuance timestamp; explicit issuance creates a token with a later timestamp.
That is why Fernet rotation versus reissue is not semantic hair-splitting. Re-encryption can be an infrastructure/key-lifecycle operation. Reissue is a policy event because it intentionally gives an artifact a new creation timestamp and therefore a new starting point for any age rule based on that timestamp.
The fixture labels F09 NEW_ISSUANCE_REQUIRES_POLICY. It does not answer who is permitted to issue a replacement, which identity or session state must be rechecked, whether a prior credential must be revoked, or whether a user must reauthenticate. Those decisions belong to the application’s independently defined product and security policy.
In particular, “decrypt an expired token and immediately issue another one” is not established here as a recovery procedure. A symmetric Fernet key holder can create valid tokens and authenticated timestamps. That cryptographic capability is not independent evidence that renewal is authorized.
Check primary order and authenticated metadata
F10 shows why Fernet key order rotation must be reviewed explicitly. It constructs:
MultiFernet([old, new]).rotate(original)
That operation is behaving correctly for the configured ring: the first key is the primary encryption key. The resulting token still carries timestamp 1700000000, the old key reads it, and the new key alone rejects it. Cryptography’s documented first-key behavior and the pinned implementation both support that interpretation.
The fixture labels this REPAIR_PRIMARY_ORDER only because the selected operational objective is to move protection to new. It is not evidence of a cryptography defect. The configuration contradicts the chosen target-key policy.
F11 checks a different boundary. After base64-decoding the rotated token, it flips one bit in a timestamp byte but leaves the existing authenticator untouched. Both new.extract_timestamp(tampered) and ring.rotate(tampered) raise InvalidToken.
That outcome follows from Fernet’s authentication design. The specification includes the timestamp among the bytes covered by the HMAC, and extract_timestamp() verifies the signature before returning the value. The control therefore demonstrates that this one unauthenticated timestamp mutation is not accepted as trustworthy metadata.
The adjacent lesson in Refonte Learning’s article on authenticated decryption and application admission is useful only at the decision boundary: cryptographic authentication and application admission are distinct questions. This Fernet test does not recreate that article’s CBC experiment.
InvalidToken should still be treated carefully. In an uncontrolled failure it can represent age, malformed encoding, signature failure or other invalidity documented by the API. F11 can identify its designed cause only because the test alters exactly one known field under controlled conditions.
Reconcile the evidence into operational decisions
The eleven cases support a compact decision model:
Decision | Evidence | What it means | What it does not mean |
ADMIT_AGE_CHECK | F01, F02, F05, F06 | Authenticated timestamp is within the declared test TTL | Authorization or renewal |
REJECT_AGE_CHECK | F03, F07 | Controlled token is over the declared test TTL | Generic diagnosis of every InvalidToken |
ROTATED_NOT_RENEWED | F04 | New primary protects rotated token; original timestamp retained | Revocation or fleet-wide migration |
NO_AGE_DECISION | F08 | Authenticated decryption occurred without TTL | Successful expiration validation |
NEW_ISSUANCE_REQUIRES_POLICY | F09 | Separate issuance deliberately creates a new timestamp | Permission to renew an expired credential |
REPAIR_PRIMARY_ORDER | F10 | Ring order does not match the selected new-primary objective | Library defect |
REJECT_TAMPERED_CONTROL | F11 | Controlled timestamp modification fails authentication | Classification of arbitrary hostile input |
A useful evidence record needs enough data to distinguish those states without exposing cryptographic material. This fixture records case IDs, runtime/package identities, timestamps, expected and observed outcomes, token SHA-256 labels and boolean key-specific checks. It does not log raw Fernet keys or token bytes.
That is consistent with the broader ownership principle described in Refonte Learning’s discussion of API security and observability: security-relevant behavior becomes reviewable when evidence makes the important decision boundary observable. The present test applies that principle narrowly to a local cryptographic consumer rather than to an API telemetry architecture.
Hold an unexplained result instead of changing the oracle
If a reproduction on a later runtime returns a different boundary, do not “fix” the expected table until the discrepancy is understood. First preserve the package version, interpreter version, backend identity, source digest, case inventory and actual exception/output.
A missing case, unexpected exception or source mismatch is grounds to withhold qualification. An arbitrary InvalidToken should not automatically be labeled an attack, signature failure or expiry event, because the public API intentionally uses that exception class for multiple invalid conditions.
Likewise, a fully green F01 through F11 matrix confirms the supplied experiment. It does not approve every policy exercised by the matrix. F08 is green precisely because it correctly proves the absence of an age decision; F10 is green because it correctly exposes wrong primary order relative to the selected objective.
Recover without renewing a credential accidentally
The recovery action should match the failed contract.
If the intended consumer is supposed to enforce a TTL but a wrapper accidentally omitted it, restore the intended TTL and rerun the age controls. If rotation targeted the wrong key because the ring order was [old, new], correct the primary ordering according to the agreed key policy and rerun the key-specific checks. If the token is correctly authenticated but older than the application’s maximum age, route the renewal question to the component or owner authorized to make that business decision.
Re-running rotate() is not a way to make an old token young. Cryptography documents that rotation preserves the original timestamp, and the pinned implementation explicitly carries that timestamp into the newly encrypted artifact. Re-rotation can change which key protects the artifact while leaving the age basis unchanged.
Do not collapse storage rollback into this procedure either. Replacing stored token bytes, restoring an older key list, coordinating replicas or managing concurrent readers can have availability, access and copy-management consequences. None of those operations appears in this fixture. There is no durable store, crash injection, concurrent writer, secure-erasure check or compensation transaction.
The safe operational phrasing is therefore narrow: repair the key-order configuration when that is the defect; repair the consumer TTL invocation when that is the defect; refer new issuance to its policy owner when age rejection is correct. Do not use cryptographic re-encryption as an implicit credential-renewal mechanism.
Assign ownership and requalification triggers
A maintainable review separates at least four ownership domains.
The issuer/time owner controls when a genuinely new token is issued and what source of Unix time is used for that issuance. The key-ring owner controls key membership and primary ordering. The consumer-policy owner controls whether a TTL is required and what maximum age is declared for a specific use. The security/QA reviewer owns the reproducible evidence showing that the implementation matches those contracts.
Requalification is appropriate when changing any element capable of altering the observed behavior: the cryptography version, relevant backend/runtime combination, a wrapper around Fernet calls, primary key order, TTL rule, issuance path or source of comparison time. The same philosophy applies to broader automated security testing in DevSecOps: automate stable security expectations so implementation changes surface as reviewable differences rather than silent assumptions.
The fixture deliberately leaves several domains unresolved: distributed clock synchronization, future-skew behavior, concurrency, crash durability, durable token replacement, replay controls, session policy and bulk data migration. Python’s documentation also reminds reviewers that wall-clock time can move backward after a system clock adjustment; this laboratory does not claim to have tested such adjustments.
One more ownership limit is cryptographic rather than operational: anyone possessing the symmetric Fernet key can create tokens that authenticate under that key, including tokens carrying timestamps they choose through explicit-time APIs. Authentication therefore shows consistency with the key, not independent historical proof that an honest issuer observed a particular real-world time.
Develop the security review skills behind the decision
The technical lesson is compact: rotation, issuance and age validation are different contracts. MultiFernet.rotate() can successfully move a token to a new primary key while preserving its original authenticated timestamp; the consumer can then apply the same TTL and reach the same age result it would have reached before rotation. Omitting TTL makes no age decision, while explicit new issuance creates a different timestamp and therefore requires separate policy authority. Those behaviors are documented by the Fernet API, visible in the 50.0.2 source and isolated by the supplied eleven-case fixture.
This style of review depends less on memorizing crypto terminology than on reading contracts precisely, freezing versions, defining literal oracles, including negative controls and keeping application policy separate from cryptographic success.
Refonte Learning’s Cybersecurity & DevSecOps programme lists relevant coverage in cryptography and secure data management, secure CI/CD pipelines, DAST/SAST/IAST, infrastructure-as-code security and automation, OWASP and threat modeling, incident response/risk mitigation, and security workflow automation. Its page describes practical work in a virtual-internship context, states a dedication of 12 to 14 hours per week, and says successful completion leads to a Training Certificate and a Certificate of Internship.
Those are useful foundations for the discipline demonstrated here: define what an operation actually promises, write reproducible controls around that promise, and preserve evidence when implementation behavior disagrees with the oracle. The programme page does not establish that this exact Fernet fixture, MultiFernet, or cryptography 50.0.2 is a named module, so this article does not imply that it does.