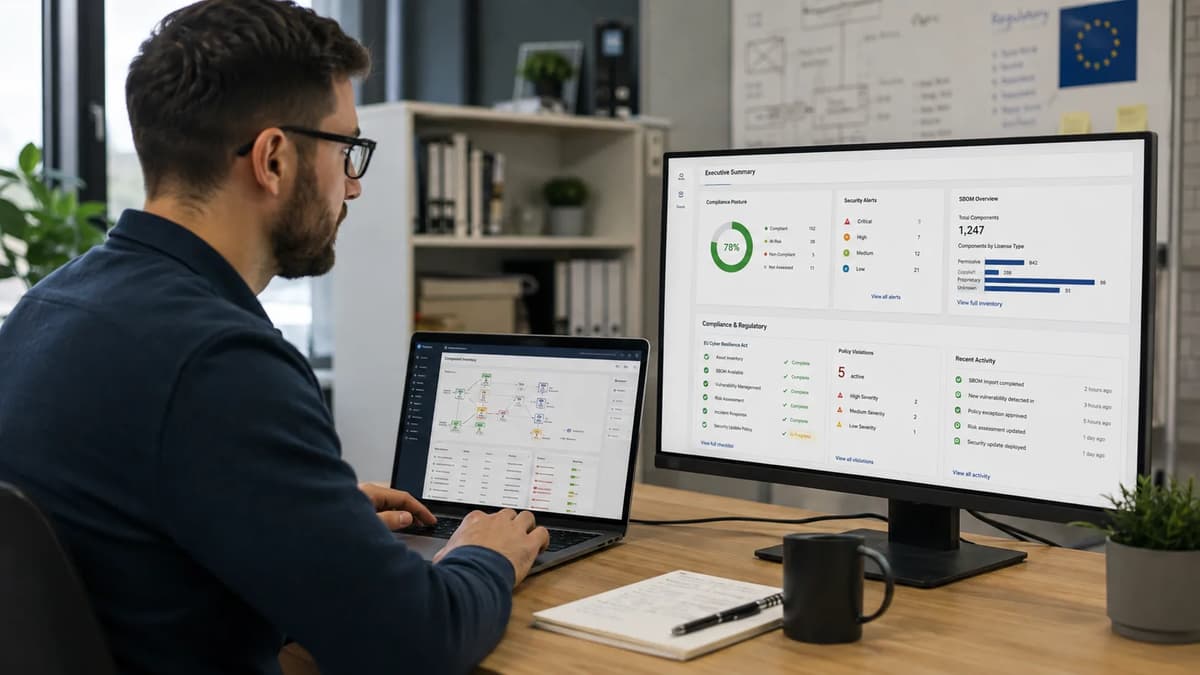
Running trivy image --format cyclonedx can generate an SBOM in seconds. It does not prove that your organization can identify every affected product when a component becomes actively exploited, preserve the evidence behind that decision, route a legally required notification, or reconstruct what your team knew at a specific point in time.
That distinction has become urgent in 2026. Cyber Resilience Act vulnerability reporting starts on September 11, 2026, while the CRA’s broader obligations apply from December 11, 2027. The European Commission says manufacturers must send an early warning within 24 hours after becoming aware of an actively exploited vulnerability or severe security incident, followed by the prescribed notification and final-report stages.
The compliance problem is therefore larger than SBOM generation. ENISA’s 2026 survey found that 44% of respondents reported a moderate gap between generating and using SBOMs, while another 23% reported a significant gap; only 7% reported no gap.
That gap is exactly where the SBOM compliance platform 2026 buying decision sits. Syft can produce inventory; Anchore Enterprise has repositioned around SBOM-powered compliance; FOSSA now offers a CRA-specific readiness assessment; and Snyk has CRA-specific capabilities and marketing of its own. The question for a compliance officer is not “which one scans?” but “which combination lets us prove what happened?”
For directional market context, QY Research estimates that the global SBOM market grew to $1.859 billion in 2025 and projects $8.222 billion by 2032. That is a commercial market-research estimate, not a regulator, audited industry census, or first-party figure, so treat it as evidence of investment direction rather than a precise measure of compliance adoption.
The CRA’s SBOM Deadlines Aren’t as Far Off as They Sound
The EU Cyber Resilience Act SBOM requirements do not begin with one single compliance date. The CRA entered into force on December 10, 2024; its reporting obligations apply from September 11, 2026; and its main obligations apply from December 11, 2027.
There is an important correction to make to the simplified timeline you will often see in vendor material. The legal reporting sequence is more nuanced than “24 hours, 72 hours, then all documentation in 14 days.”
Obligation | Timing | What your program actually needs |
Early warning for actively exploited vulnerability | Within 24 hours of awareness, from Sept. 11, 2026 | Detection, triage, product mapping, decision ownership and reporting access |
Vulnerability notification | Within 72 hours of awareness | Updated information, severity/impact assessment and affected-product context |
Final vulnerability report | No later than 14 days after a corrective or mitigating measure is available | Documented remediation, analysis and preserved supporting evidence |
Early warning for severe incident affecting product security | Within 24 hours of awareness | Incident classification and escalation capable of distinguishing CRA-reportable events |
Severe-incident notification | Within 72 hours of awareness | Formal incident information and impact assessment |
Final severe-incident report | Within one month of the incident notification | Root-cause and corrective-action documentation |
Main CRA obligations, including SBOM-related Annex I requirements | Dec. 11, 2027 | Continuous component documentation, maintained SBOMs and conformity evidence |
The Commission’s July 31 reporting guidance confirms the 24-hour early-warning and 72-hour full-notification stages. It also states that a final report for an actively exploited vulnerability is due no later than 14 days after a corrective measure is available, whereas the final severe-incident report follows a one-month timeframe.
That distinction matters in an audit. You do not want an internal procedure saying “final report in 14 days” if the regulation establishes different final-report triggers for vulnerabilities and severe incidents.
The SBOM side is equally specific. ENISA summarizes the CRA requirement as requiring manufacturers to generate an SBOM for products with digital elements, use a commonly used machine-readable format, cover at least top-level dependencies, keep the SBOM current through the product lifecycle, include it in technical documentation, and provide it to market-surveillance authorities upon request; ENISA explicitly notes that the CRA does not require public publication of the SBOM.
Non-compliance is not merely a documentation inconvenience. The regulation provides for administrative fines of up to €15 million or, for an undertaking, up to 2.5% of total worldwide annual turnover for specified violations including relevant Article 14 obligations.
The independent Cyber Resilience Act implementation site can be useful as a readable reference, but a defensible compliance program should anchor legal interpretations to EUR-Lex, European Commission guidance and ENISA rather than treating an independent guide as the legal authority.
Why September Matters More Than the Later Headline Date
Compliance teams that fixate on December 2027 can miss the nearer operational risk. September 11, 2026 arrives first, and the obligation that starts then is not “have an SBOM project underway”; it is “be able to report qualifying vulnerabilities and incidents inside legally defined windows.”
That requires a product inventory, ownership model, vulnerability intake process, escalation criteria, incident classification procedure and evidence-retention design before your first reportable event occurs. A 24-hour timer is particularly unforgiving of unresolved questions such as “which team owns this product?” or “does this package appear in the EU version we actually shipped?”
There is another reason not to postpone the work: the Commission says the Single Reporting Platform, established under Article 16 and operated by ENISA, will become operational by September 11, 2026, and functional and security testing was still underway in its July 31 update.
For a compliance officer, the practical implication is simple:
Build the internal evidence workflow before you depend on the external reporting interface.
Define who may make a reportable-event determination.
Preserve the facts and timestamps behind that determination.
Rehearse the handoff among product security, incident response, engineering, legal and compliance.
Your September readiness exercise therefore needs to test decision latency, not merely scanning latency.
Generating an SBOM Is the Easy Part: Syft and the Open-Source Tooling Layer
Syft is a good example of why generation and compliance should be treated as separate architectural layers. Anchore describes Syft as an open-source CLI and Go library for generating SBOMs from container images and filesystems, with support for CycloneDX, SPDX, Syft JSON and other formats across dozens of package ecosystems.
As of August 2026, the repository displayed roughly 9.4k GitHub stars, so the 9.1k figure appearing in earlier comparisons is already stale. Syft can also create SBOM attestations using the in-toto specification, while Anchore’s documentation describes support for cryptographically signed attestations with in-toto and Sigstore.
Anchore also publishes an official GitHub Action that invokes Syft and can upload the resulting SBOM as a workflow artifact or release asset.
Layer | What Syft is good at | What a compliance program still needs |
Discovery | Identifying packages in images, filesystems and archives | Determining which regulated product/version the artifact belongs to |
SBOM creation | CycloneDX, SPDX, Syft JSON and other output | Retention rules, lifecycle status and evidence ownership |
Build integration | Automation through CI, including Anchore’s GitHub Action | Control evidence showing when generation succeeded or failed |
Attestation | in-toto/Sigstore-compatible signing capabilities | Approval, custody and evidentiary policy |
Vulnerability response | Provides inventory that downstream tooling can evaluate | Impact analysis, triage workflow, regulatory deadlines and reporting decisions |
Audit | Produces an artifact | Demonstrates history, completeness, approvals and regulatory traceability |
That final row is where teams get into trouble. A JSON file answers “what did this generator detect?”; it does not automatically answer “what product did we sell, which release was in market, which vulnerability intelligence did we rely on, who made the impact decision, when did they make it, and what did we report?”
There is no need to rebuild scanner mechanics here. Refonte Learning already covers the mechanics of generating SBOMs with tools like Trivy; the compliance buyer’s problem begins after generation succeeds.
For a CRA program, Syft belongs naturally in the generation layer. You can absolutely build a broader compliance system around open-source components, but then your organization, not the generator, owns the engineering of inventory indexing, historical records, alerting, role-based access, evidence retention, product mappings and reporting orchestration.
That can be a rational choice for a technically mature company. It is not the same procurement decision as buying a commercial compliance platform.
Anchore Enterprise: SBOM Generation Repositioned as a Compliance Product
Anchore made that distinction unusually explicit in May 2026. The company announced Enterprise v6 as a “unified SBOM-powered compliance solution” and tied the release directly to the CRA reporting obligations beginning September 11.
The vendor says Enterprise v6 combines a unified asset model, SBOM generation and ingestion, vulnerability information, VEX-supported prioritization, centralized third-party SBOM management, continuous monitoring and automated reporting. It explicitly markets the platform for automating CRA-related SBOM management and vulnerability-reporting work.
That repositioning is a meaningful market signal, although not proof that buying Anchore equals CRA compliance. A software vendor changing its product narrative from scanning toward auditability and CRA workflow tells you what enterprise buyers are now asking procurement teams to justify.
A useful buyer evaluation looks like this:
Evidence question | What to ask Anchore to demonstrate |
Can I identify every version containing component X? | Query product/application versions against stored SBOM inventory |
Can I reconstruct yesterday’s state? | Historical evidence and time-stamped reporting |
Can I distinguish build inventory from current vulnerability status? | Continuous re-evaluation of stored SBOM data |
Can I ingest supplier SBOMs? | Import workflow for CycloneDX/SPDX supplier artifacts |
Can I show why a finding was accepted or suppressed? | VEX, policy evaluation, exceptions and remediation records |
Can compliance get evidence without asking engineering to rerun a scan? | Compliance reporting interface and export |
Can we connect evidence to CRA reporting decisions? | Live demonstration of the organization’s intended Article 14 process |
The last question matters most. Vendor features can support an Article 14 process; the software cannot make the legal determination that an event meets the CRA reporting threshold for you.
How Anchore’s Positioning Differs From a Pure Scanner
A scanner typically answers a narrow technical question: what known vulnerabilities match the software I just analyzed? A compliance platform has to preserve enough product and evidence context for another function, often compliance, legal, product security or audit, to ask the same question later without recreating the build.
Anchore’s own product material says it manages internal and external SBOMs in a central location and embeds security and compliance checks through the development lifecycle. Its Enterprise v6 release also introduced a unified asset model intended to create one view of application assets across the SDLC.
That architecture can close a real evidence problem. Consider a new actively exploited vulnerability in library X: compliance does not merely need a CVE result; it needs to know which commercial products contain X, which supported versions remain exposed, whether a mitigation exists, who owns those versions and what evidence supports the reporting decision.
The platform still needs to prove itself against your environment. Do not accept “CRA-ready” as a procurement requirement; convert it into test cases such as:
Search every currently supported EU product for an arbitrary dependency.
Produce a historical inventory for a specified release date.
Show how imported supplier SBOMs appear in the same investigation.
Demonstrate evidence of policy decisions and exceptions.
Export the evidence required for your internal 24-hour reporting record.
Show which actions remain manual.
That is how you evaluate Anchore Enterprise CRA claims without turning a vendor presentation into your control narrative.
FOSSA’s CRA Readiness Assessment: A Free Starting Point Worth Using
FOSSA takes a different entry point. Its free CRA Readiness Assessment asks organizations about product classification, vulnerability handling, reporting, SBOM and supply-chain governance, secure-by-design measures and lifecycle security, then generates a prioritized 30/60/90-day remediation plan and executive-ready report.
FOSSA says the assessment maps responses to Annex I and gives heavier scoring weight to issues it considers central, including Article 14 reporting and machine-readable SBOM readiness. The company explicitly describes the result as directional planning guidance rather than legal advice, which is the right boundary for this class of tool.
Assessment output | Compliance value | What it does not prove |
Readiness score | Creates a common baseline for stakeholders | Legal conformity |
Annex I mapping | Helps organize remediation areas | That every requirement applies exactly as interpreted by the tool |
SBOM/supply-chain questions | Exposes missing inventory controls | SBOM completeness in production |
Reporting-workflow questions | Forces ownership conversations | That your team can execute under a real deadline |
30/60/90-day plan | Converts gaps into sequenced work | Continuous compliance after remediation |
Executive report | Supports sponsorship and budget discussion | Audit evidence that controls operated |
For a company that has not yet performed a CRA readiness assessment, this is useful because the first problem is often not tooling at all. It is discovering that legal has not confirmed product scope, engineering has no authoritative supported-version inventory, product security and incident response use different severity language, and nobody owns regulator notification.
There is also an important caution in FOSSA’s own page. Its brief summary says “24-hour vulnerability reporting” in a way that can sound as if the entire notification is due inside 24 hours; the Commission’s official guidance distinguishes the 24-hour early warning, the 72-hour notification and later final-report stages.
That is a useful reminder of how compliance officers should use every vendor tool: vendor mappings accelerate analysis; they do not replace the regulation or authoritative implementation guidance.
The free assessment also does not replace an operating platform. FOSSA separately sells SBOM management and compliance capabilities, including application-level SBOMs, vulnerability monitoring and SBOM-sharing functions, but procurement should evaluate those capabilities independently from the free assessment.
So the correct FOSSA CRA readiness model is:
1. Use the assessment to expose program gaps.
2. Validate those gaps against counsel and official CRA sources.
3. Assign owners and deadlines.
4. Decide whether FOSSA’s broader platform, or another platform, meets your operating requirements.
5. Test the actual reporting workflow with a simulated vulnerability.
A PDF roadmap sitting in a governance folder is better than no assessment, but it is not a control.
What About Snyk?
A source review does not support saying that Snyk lacks CRA-specific capability. Snyk has explicitly published CRA material describing SBOM generation, vulnerability management and rapid reporting, and its current CRA landing page says its platform supports automated vulnerability scanning, SBOM generation and compliance reporting.
What did not surface in the sources checked is a separately named CRA product or a free readiness-assessment workflow directly equivalent to FOSSA’s CRA Readiness Assessment. That is a narrower and defensible statement.
Question | Anchore | FOSSA | Snyk |
Explicit CRA positioning found | Yes | Yes | Yes |
SBOM generation/management positioning | Yes | Yes | Yes |
Vulnerability-management positioning | Yes | Yes | Yes |
Dedicated free CRA readiness assessment found | No equivalent reviewed | Yes | No equivalent reviewed |
Enterprise evidence workflow needs live validation | Yes | Yes | Yes |
Should buyer assume marketing = legal compliance? | No | No | No |
That means Snyk belongs on a serious shortlist where it already has a footprint. Do not eliminate it because an article calls it “just a scanner,” but do not assume an existing Snyk deployment automatically supplies the evidence architecture your CRA program needs.
Ask Snyk and every other vendor to run the same proof-of-capability scenario:
“Here is an actively exploited dependency.”
“Show me every affected commercial product and supported version.”
“Show me the evidence timestamp.”
“Show me who triaged it and how exceptions are recorded.”
“Show me the data compliance receives before the 24-hour deadline.”
“Show me what must still happen outside your platform.”
That evaluation keeps this article distinct from the advanced SBOM and supply chain security use cases Trivy already covers. The issue here is not whether a tool can find a package; it is whether your organization can turn that fact into regulated action.
Absence of a named CRA SKU is not absence of CRA capability. Conversely, presence of a CRA landing page is not evidence that your reporting control operates effectively.
The Gap ENISA Found: Generating SBOMs Without Using Them
ENISA’s SBOM Adoption State of Play: 2026 is the most useful evidence in this market because it measured what organizations are actually doing rather than what vendors say they should do. The survey received 334 responses, with about 65% from EU-based organizations and more than 80% from companies directly affected by the CRA.
The results expose the exact generation-to-compliance gap this article is concerned with.
ENISA finding | Survey result | Compliance interpretation |
Partially/fully automated SBOM generation for each release/build | 74% | Production is progressing quickly |
Partially/fully automated vulnerability workflow tied to SBOM | 51% | Operational response trails generation |
Partially/fully automated SBOM updates | 52% | Lifecycle maintenance remains incomplete |
Partially/fully automated SBOM inclusion in technical documentation | 39% | Evidence packaging lags technical generation |
Respondents reporting moderate generation-to-utilization gap | 44% | SBOM files exist but are not fully operationalized |
Respondents reporting significant gap | 23% | Nearly one quarter sees a major operational disconnect |
Respondents reporting no gap | 7% | Fully closing the loop remains uncommon |
The stakeholder numbers are just as revealing. Security/AppSec and development/engineering each accounted for 34% of primary SBOM stakeholders in the survey, while legal/compliance accounted for 15% and procurement just 5%.
That distribution helps explain why SBOM programs can be technically healthy but audit-poor. Engineering owns the generator, security owns vulnerability matching, but neither automatically owns the legal evidence package.
ENISA also found that respondents primarily used SBOMs for vulnerability identification and patching at 29%, open-source licensing at 22%, regulatory requirements at 19%, third-party risk at 14% and component inventory at 13%.
Supply-chain ingestion remains weak, too. For commercial off-the-shelf products, 39% said suppliers never provided an SBOM and another 39% said they rarely did; only 2% said suppliers always provided one as a standard practice.
These are not reasons to abandon SBOMs. They are reasons to stop measuring maturity by “percentage of repositories generating CycloneDX.”
What “Utilization” Actually Looks Like in Practice
A useful SBOM is one you can query before an incident forces you to rebuild your knowledge of the product. When a vulnerability becomes actively exploited, the first compliance question is not “can Syft generate another file?” but “which products already in our indexed inventory contain the affected component?”
A mature workflow should produce an answer resembling this:
Question during an incident | Evidence source |
Which product contains the component? | Product-to-SBOM inventory |
Which shipped versions are affected? | Release and lifecycle records |
Is the product still supported? | Product-support register |
Which customers/markets may be exposed? | Distribution and product records |
Is the vulnerability exploitable in our implementation? | AppSec analysis/VEX decision |
When did we become aware? | Intake/event timestamp |
Who classified the event? | Case record and approval history |
What remediation exists? | Engineering remediation record |
What did we notify and when? | CRA reporting record |
Can we reproduce the evidence six months later? | Retained audit trail |
This is SBOM audit evidence: not one static inventory file, but a traceable relationship among software composition, product identity, vulnerability intelligence, human decisions, deadlines and remediation.
ENISA’s investment data shows organizations already recognize where the gap lies. Among respondents, 34% were investing in vulnerability handling using SBOMs, 21% in automating SBOM inclusion in technical documentation, 19% in deeper generation and another 19% in continuous updating.
The platform procurement question should therefore be: Which product reduces the time from vulnerability intelligence to defensible product-level evidence?
That is much more useful than comparing scanner benchmark speeds.
A Practical Compliance-Officer Workflow for the September Deadline
A defensible CRA program needs clear sequencing because legal scope, engineering implementation and incident response depend on one another. SBOM generation and platform evaluation can proceed in parallel, but the reporting workflow must reach rehearsal stage before September 11.
Step | Owner | Required output |
Map products that may fall within CRA scope | Compliance/legal + product leadership | Product scope register with rationale |
Identify manufacturers and economic-operator roles | Legal/compliance | Responsibility mapping |
Map supported products and versions | Product + engineering | Authoritative lifecycle inventory |
Automate SBOM generation | DevSecOps | SBOM artifact for each governed release |
Connect SBOMs to product/version identity | DevSecOps + product security | Queryable product composition inventory |
Select evidence/reporting platform | Compliance + security + procurement | Requirements-based vendor decision |
Define vulnerability intake | Product security | Timestamped intake process |
Define Article 14 classification | Product security + legal | Decision tree and RACI |
Build reporting package | Compliance + incident response | Approved templates and evidence checklist |
Rehearse reporting | Cross-functional team | Tabletop record and corrective actions |
Retain evidence | Compliance/security | Defined retention and immutable history |
The first step is deliberately legal, not technical. “Products with digital elements” is a regulatory scope concept; a scanner should never decide which commercial offerings your counsel considers in scope.
The second major dependency is product identity. An SBOM labeled with a repository or container digest may satisfy engineering, but compliance needs a reliable mapping from that artifact to the product/version placed on the EU market.
The third dependency is time. Your incident clock begins when the organization becomes aware according to the applicable CRA rule, not when the compliance officer eventually receives a ticket, so intake and escalation timestamps need to be designed deliberately.
A practical tabletop test could start at 09:00 with threat intelligence showing active exploitation of a dependency. By the end of the exercise, the team should be able to prove which supported products contain it, document the exploitability assessment, establish who made the reporting determination and assemble the initial information needed for the required early warning.
Record every place where somebody says, “I need to ask another team for that.” Those handoffs are your actual control weaknesses.
This workflow complements broader DevSecOps compliance and governance best practices, but CRA readiness requires the extra product-level evidence and statutory reporting timing described here.
A sensible sequencing rule is:
Now: settle scope, ownership and product inventory.
Next: automate SBOM production and index the results.
In parallel: select the evidence/platform layer.
Before September: conduct at least one full Article 14 tabletop.
After each exercise: remediate process latency and missing evidence.
Toward December 2027: mature technical documentation, lifecycle SBOM maintenance and conformity evidence.
The Commission’s latest page says the Single Reporting Platform will be operational by September 11 and that functional and security testing remains underway. Your internal process therefore needs enough flexibility to absorb final platform procedures without redesigning the evidence workflow itself.
Skills Priority Order for DevSecOps Professionals Handling CRA Compliance
A DevSecOps compliance specialist 2026 needs enough technical depth to challenge scanner output and enough regulatory literacy to know why that output exists. The sequence matters.
Priority | Skill | Why it ranks here |
Must | Read the CRA timeline accurately | Every control depends on knowing which deadline and obligation you are solving |
Must | Product-to-software traceability | A vulnerability has to map to a regulated product/version |
Must | Secure CI/CD integration | SBOM evidence must follow releases consistently |
Must | Vulnerability and incident workflow design | Article 14 creates time-bound operational duties |
Should | Compliance-platform evaluation | Vendor capabilities need to map to evidence requirements |
Should | Evidence retention and auditability | You must reconstruct what happened later |
Should | Incident tabletop execution | A documented procedure is not proof that the process works |
Good | CycloneDX/SPDX literacy | Enough knowledge to challenge format and completeness claims |
Good | VEX concepts | Helps distinguish component presence from actual exploitability |
Good | Supplier SBOM ingestion | Third-party inventory quality affects product-level visibility |
Deadline literacy ranks first because confusing September 2026 with December 2027 creates the wrong implementation plan. A team that spends the next year perfecting SBOM document formatting while leaving Article 14 escalation untested has optimized the later control while neglecting the earlier legal obligation.
Secure CI/CD comes next because manual evidence creation does not scale reliably across releases. ENISA found 74% of respondents had at least partially automated release/build SBOM generation, yet only 39% had reached the equivalent level for inclusion in technical documentation, the exact transition a compliance-minded engineer needs to understand.
Vendor evaluation is a separate professional skill. The right question is not “does Anchore support CycloneDX?” but “can Anchore prove the product/version state we need, preserve historical evidence and fit the incident RACI approved by legal?”
For professionals, that is where CRA work becomes more valuable than memorizing scanner commands: you translate a legal obligation into a repeatable engineering control and then prove that the control operated.
Certifications Worth Having for CRA Compliance Work
I would not tell a hiring manager that a generic security certificate proves CRA capability. As of the sources reviewed in August 2026, I did not find a widely recognized, regulator-backed or industry-standard individual certification dedicated specifically to CRA compliance.
CRA-specific education already exists. The Linux Foundation/OpenSSF offers a free CRA course covering requirements and conformity concepts and awards a completion badge/certificate, but that is training completion rather than an industry-standard professional CRA certification comparable to established security-management credentials.
Credential/evidence | What it signals | CRA-specific? |
Linux Foundation/OpenSSF CRA course | Regulatory awareness | Yes, training-level |
ISO/IEC 27001 Lead Implementer | Ability to implement and manage an ISMS | No |
ISO/IEC 27001 Lead Auditor | Audit-method competence | No |
Lab-based CRA readiness case study | Ability to translate requirements into controls | Can be |
SBOM incident-response tabletop | Operational evidence and workflow judgment | Can be |
Vendor platform lab | Product-specific capability | No legal authority |
PECB describes its ISO/IEC 27001 Lead Implementer credential as demonstrating the ability and practical knowledge to implement an information security management system. That does not prove CRA knowledge, but it can support the broader implementation and evidence discipline this work demands.
For a practitioner portfolio, I would value a documented CRA case study highly. Take a lab application, establish a product/version inventory, generate SBOMs in CI, feed them into an indexed system, simulate an exploited dependency, document the 24-hour/72-hour process, and write an audit evidence package.
That shows judgment a multiple-choice exam cannot easily show.
A credible portfolio artifact should disclose its boundaries: “lab simulation, not legal advice; no actual conformity determination.” Compliance hiring managers tend to trust people who know exactly what they can and cannot prove.
What This Means for DevSecOps Compliance Specialist Salaries
Do not turn CRA deadlines into a salary prediction. There is not enough evidence to say that the regulation by itself raises compensation by a fixed percentage.
There is, however, a relevant 2026 market signal. KORE1’s updated DevSecOps salary guide puts U.S. base pay broadly at $115,000–$185,000, with senior/staff total compensation reaching $200,000–$340,000 in its analysis.
KORE1 measure | Reported range/data | How to interpret it |
Broad U.S. base range | $115K–$185K | Directional role-market range |
Senior/staff total compensation | $200K–$340K | Includes equity/bonus effects |
KORE1 placed-base median | $152.8K | Based on 41 cited placements |
SBOM/supply-chain specialty | Vendor reports $175K+ senior base | Recruiter-observed specialty premium, not a universal benchmark |
KORE1 deserves a methodological caveat. It is a staffing company with a commercial interest in hiring activity, and the guide itself discloses that conflict; it says its analysis combines public sources with 41 closed DevSecOps/security-engineering searches from late 2025 through early 2026.
That makes the ranges useful for direction, not authoritative salary truth. Geography, employer type, equity, clearance requirements, cloud stack and whether the role owns build pipelines versus audit/GRC responsibilities can move compensation substantially.
The more defensible career takeaway is about skill combination. An engineer who can integrate software-supply-chain controls, interpret regulatory requirements, build evidence retention and participate credibly in incident response occupies a narrower talent category than somebody who can only execute an SCA scan.
KORE1’s guide specifically identifies SBOM and software-supply-chain depth as a scarce specialty in regulated environments. Again, that is recruiter evidence rather than an industry census, but it aligns with the technical responsibilities CRA programs now need.
For candidates, I would therefore optimize for demonstrable control ownership, not a new job title. “I implemented SBOM generation” is useful; “I mapped product releases to SBOM evidence, built vulnerability-impact queries, rehearsed the regulatory escalation process and preserved an auditable record” is much stronger.
Common Mistakes Compliance Teams Make With SBOM Tooling
The recurring errors are organizational rather than syntactic. ENISA’s survey is especially useful here because it shows that generation has moved ahead faster than utilization and technical-documentation integration.
Mistake | What it looks like | Corrective control |
Treating generation as compliance | “Every build emits an SBOM, so we are done” | Evidence + product mapping + lifecycle workflow |
Keeping SBOMs by repository only | Compliance cannot map dependency to commercial product | Product/version asset model |
Rebuilding inventory during incidents | Response starts with rescanning everything | Continuously indexed inventory |
Buying on CRA marketing | Vendor deck substitutes for requirements testing | Scenario-based procurement |
Ignoring supplier SBOM quality | Internal code is visible; COTS dependencies are opaque | Supplier intake and validation |
Waiting to rehearse | First test occurs during a real exploited vulnerability | Pre-deadline tabletop |
Treating SBOM Generation as Compliance, Full Stop
This is the most common conceptual error because generation produces something visible. A build finishes and a .json artifact appears; the team can point to it.
But ENISA found the structural weakness directly: 44% of respondents described a moderate generation-to-utilization gap and 23% a significant one.
Fix it by separating controls in your compliance matrix:
Generation control: every governed release produces an SBOM.
Completeness control: required component depth and fields meet your policy.
Identity control: SBOM maps to a specific product and release.
Maintenance control: product SBOM remains current through its support period.
Monitoring control: stored inventories receive updated vulnerability intelligence.
Response control: security can identify affected products within the defined SLA.
Evidence control: decisions and timestamps remain reconstructable.
Provision control: authorized personnel can produce the applicable SBOM when required.
A control does not become effective merely because the preceding control passed.
Waiting Until Close to September to Build the Reporting Workflow
The second mistake is scheduling a “CRA reporting project” for the same month reporting becomes mandatory. A process with a 24-hour initial window has to work before the obligation starts, because there is no implementation grace period inside an actual vulnerability event.
A pre-deadline test should inject failures deliberately:
The component has three aliases.
One affected product uses an imported supplier SBOM.
The product owner is unavailable.
VEX says one version is not affected.
Legal disputes the initial classification.
The platform lacks customer-market metadata.
The reporting portal is temporarily inaccessible.
Engineering produces a patch before the final vulnerability report becomes due.
The purpose is not to make a tabletop dramatic. It is to discover whether your clock depends on individuals rather than controls.
Afterward, ask the question legal teams eventually ask in real audits: “Show me the evidence that the process worked.”
If the answer is a Slack thread plus screenshots from four tools, you have identified your next compliance engineering project.
Self-Study vs. a Structured Cybersecurity & DevSecOps Program: An Honest Comparison
You can learn the technical foundations for this work independently. Open-source tooling, the CRA legal text, ENISA reports and the free Linux Foundation CRA course make that entirely possible.
What I would not claim is that every self-learner becomes job-ready in a fixed “six to twelve months,” because there is no defensible universal benchmark for that. The relevant comparison is structure and evidence of practice, not a fabricated average.
Factor | Self-study | Structured Cybersecurity & DevSecOps Program |
Learning sequence | You design it | Defined curriculum |
Secure CI/CD practice | Depends on your lab plan | Confirmed Refonte competency |
IaC security automation | Depends on your project choices | Confirmed Refonte competency |
Incident response | Must be deliberately practiced | Confirmed Refonte competency |
Security testing breadth | Self-selected | DAST, SAST and IAST listed |
Portfolio structure | Entirely self-designed | Program progresses to a capstone project |
Completion timeline | Variable | Refonte specifies three months |
Weekly structure | Variable | Refonte specifies 12–14 hours/week |
CRA/SBOM-specific curriculum | Available through separate sources | Not claimed by Refonte’s program page |
The last row is important. Refonte Learning’s Cybersecurity & DevSecOps page does not name SBOM, CycloneDX, SPDX or the Cyber Resilience Act in its published curriculum, so it would be inaccurate to advertise the program as direct CRA-compliance training.
What it does list is the foundation that makes this work possible: Secure CI/CD Pipelines, IaC Security and Automation, Incident Response and Risk Mitigation, Security Workflow Automation, and application-security testing.
That is the honest connection. An SBOM compliance platform plugs into development and response processes; somebody still needs to understand those processes well enough to integrate, test and challenge it.
The same distinction applies to broader regulation knowledge. Readers interested in how DevSecOps specialists navigate GDPR, HIPAA, and ISO 27001 compliance can use that context alongside CRA-specific primary sources rather than treating all compliance frameworks as interchangeable.
My preferred hybrid route for a new practitioner is structured security/DevSecOps fundamentals plus a dedicated CRA lab. The program supplies the pipeline and incident-response foundations; official EU guidance, ENISA and CRA-specific training supply the regulatory layer.
That combination is more defensible than pretending one course teaches every emerging regulation.
The Refonte Learning Cybersecurity & DevSecOps Program
The Refonte Learning Cybersecurity & DevSecOps Program is a three-month online virtual internship program requiring 12–14 hours per week. Its page says applicants must be engaged in bachelor’s or postgraduate studies.
The opening curriculum shown publicly includes Fundamentals of Cybersecurity, Exploring Cyber Threats, and Hands-On Practice: Applying Descriptive Techniques in Cybersecurity, with the broader syllabus continuing into practical work and a capstone.
Its confirmed competency list is directly relevant to the foundation behind compliance engineering:
Ethical Hacking and Penetration Testing
Cryptography and Secure Data Management
IDS, Firewalls, and Honeypots
Network and Cloud Security
Secure CI/CD Pipelines
DAST, SAST, and IAST
IaC Security and Automation
OWASP and Threat Modeling Practices
Incident Response and Risk Mitigation
Security Workflow Automation
Those are relevant because compliance automation only works when the underlying delivery pipeline has predictable control points. Anchore, FOSSA, Snyk or an open-source SBOM stack cannot compensate for a CI/CD process in which teams cannot reliably identify what artifact became which product release.
Program fact | Confirmed detail |
Format | Online virtual internship |
Duration | 3 months |
Weekly commitment | 12–14 hours |
Prerequisite | Engaged in bachelor’s or postgraduate studies |
Key pipeline competency | Secure CI/CD Pipelines |
Automation competency | IaC Security and Automation |
Response competency | Incident Response and Risk Mitigation |
Security testing | DAST, SAST and IAST |
Mentor | Dr. Christine Baker |
One-time fee | $300 |
Installments | $204 + $98 |
The program page identifies Dr. Christine Baker as a Senior Cybersecurity Consultant with more than 15 years of experience and expertise spanning threat analysis, incident response and security architecture.
The tools referenced by the program include Wireshark, Metasploit, Nmap, Burp Suite and Kali Linux, according to the verified program information provided for this article. These should not be confused with a claim that the program teaches Anchore, FOSSA, Syft or CRA tooling specifically.
Upon successful completion, Refonte says students receive a Training Certificate and Certificate of Internship. Its page also states that outstanding performers may receive a Letter of Recommendation and Certificate of Appreciation.
The listed career outcomes are DevSecOps and Cyber Risk Analyst, Secure Development and Cyber Security Specialist, and Application Security and Cyber Threat Expert.
Fees currently shown on the program page are $300 as a one-time payment, or installments of $204 and $98. Note that those two installments total $302, so prospective students should rely on the checkout terms applicable when enrolling rather than assuming the installment total equals the one-time price.
For context beyond CRA and SBOMs, Refonte also covers the broader cybersecurity trends shaping 2026. The useful connection here remains narrower: secure pipelines, infrastructure automation and incident-response discipline are exactly the foundations you need before an SBOM compliance platform becomes more than a purchased dashboard.
The program does not claim to teach CRA or SBOM compliance specifically. Its defensible role is to build the technical foundation on which you can later practice CRA-specific platform integration and evidence design.
Explore the Refonte Learning Cybersecurity & DevSecOps Program for structured practice in secure CI/CD, security automation and incident-response fundamentals.
FAQ: People Also Ask
When do the EU Cyber Resilience Act’s SBOM requirements take effect?
The CRA’s vulnerability and incident reporting obligations begin on September 11, 2026, while the regulation’s main obligations apply from December 11, 2027. The latter include the Annex I vulnerability-handling duties under which manufacturers must maintain software-component information and draw up an SBOM in a commonly used, machine-readable format covering at least top-level dependencies.
Do not interpret September 2026 as a generic “72-hour deadline.” The Commission specifies a 24-hour early warning, a 72-hour notification and different final-report timing for actively exploited vulnerabilities versus severe incidents.
Is generating an SBOM the same as being CRA-compliant?
No. SBOM generation addresses one technical requirement, while CRA readiness also depends on product scope, lifecycle maintenance, vulnerability handling, reporting, technical documentation and evidence processes.
ENISA’s 2026 survey found a clear operational gap: 44% of respondents reported a moderate gap between generating and utilizing SBOMs, 23% reported a significant gap and only 7% reported no gap.
What does Anchore Enterprise v6 actually add for CRA compliance?
Anchore’s May 2026 release repositioned Enterprise v6 as a “unified SBOM-powered compliance solution.” The company describes centralized internal and third-party SBOM management, a unified asset model, vulnerability analysis, VEX-supported triage, continuous monitoring and reporting, while explicitly marketing the release for CRA-related SBOM management and vulnerability reporting.
Those are vendor-documented capabilities, not a legal guarantee of compliance. Buyers should test them against their own Article 14 evidence and reporting workflow.
What is FOSSA’s CRA Readiness Assessment?
It is a free browser-based assessment that maps responses to CRA requirements and generates a prioritized 30/60/90-day remediation plan plus an executive-oriented report. FOSSA says it covers areas including Annex I, SBOM and supply-chain governance, product classification, vulnerability handling and reporting.
FOSSA itself labels the tool as directional planning guidance rather than legal advice. It is a useful scoping tool, not proof that ongoing operational controls work.
Does Snyk have a dedicated CRA compliance product?
Snyk clearly has CRA-specific positioning and capabilities: its current materials describe automated vulnerability scanning, SBOM generation and compliance reporting in the CRA context.
In the sources reviewed for this article, however, I did not find a separately named CRA product/SKU or a free readiness-assessment experience directly equivalent to FOSSA’s CRA Readiness Assessment. Procurement teams should request a live Article 14 mapping demonstration rather than infer capability from either product naming or general scanner features.
Does the Refonte Learning Cybersecurity & DevSecOps Program teach SBOM or CRA compliance specifically?
No. The published program curriculum does not name SBOM, CycloneDX, SPDX or the Cyber Resilience Act, so it would be inaccurate to claim direct CRA-compliance training.
Its relevant contribution is foundational: the program explicitly develops Secure CI/CD Pipelines, IaC Security and Automation, Incident Response and Risk Mitigation, application-security testing and Security Workflow Automation, the engineering capabilities needed to integrate and operate compliance tooling responsibly.
The CRA buying decision becomes much clearer once you stop asking which scanner “supports SBOM” and start asking what your legal, security and engineering teams must be able to prove.
The September 11, 2026 reporting deadline comes first. It requires a working, rehearsed process for 24-hour early warning, subsequent notification and final reporting, not a directory full of generated SBOM files.
Syft and similar tools solve generation extremely well, but generation is one control. ENISA’s 2026 data shows the industry has progressed further on producing SBOMs than on operationalizing them in vulnerability workflows and technical documentation.
Anchore Enterprise, FOSSA and Snyk approach the next layer differently. Anchore has made SBOM-powered compliance central to its Enterprise positioning; FOSSA offers an unusually practical free CRA readiness assessment; Snyk has CRA-specific SBOM, vulnerability and reporting positioning that also deserves direct evaluation.
Your underlying operating discipline matters more than the logo on the platform. Secure CI/CD, authoritative product inventory, incident classification, evidence retention and rehearsed escalation determine whether automation becomes defensible compliance or automated theater.
For the secure CI/CD, security-automation and incident-response foundation that makes a compliance platform operationally meaningful, the Refonte Learning Cybersecurity & DevSecOps Program provides a structured starting point.