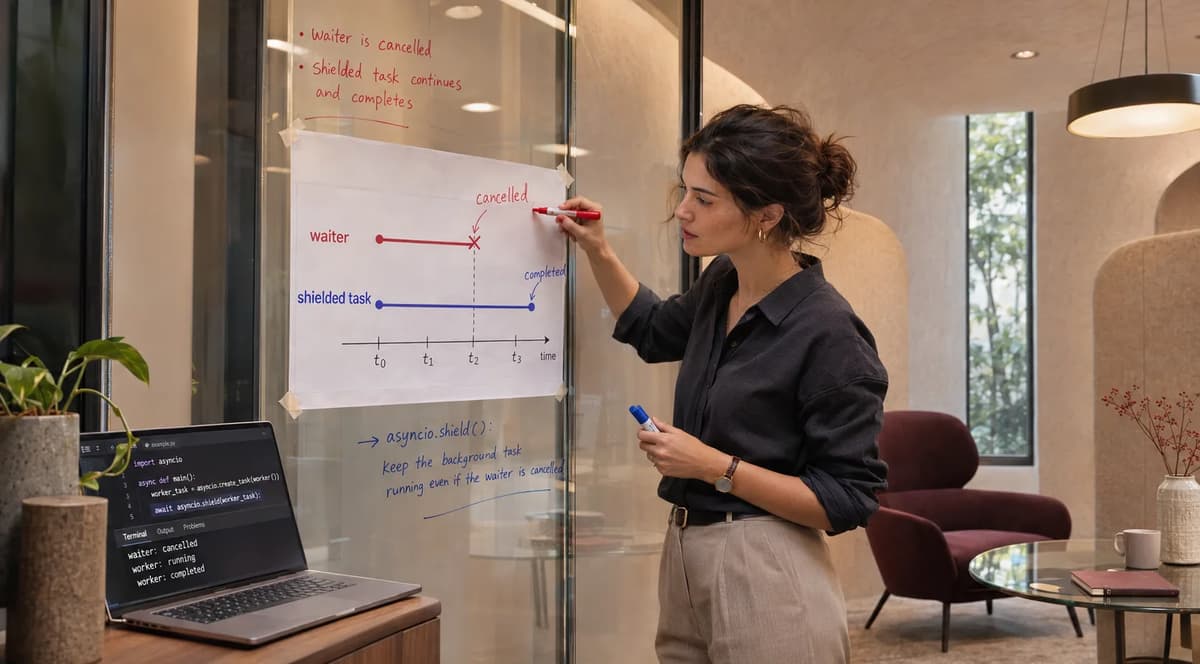
A CancelledError at an await asyncio.shield(task) boundary is not evidence that the protected task was cancelled, finished, succeeded, failed, or committed its intended effect. Python’s documented contract is narrower: when the coroutine awaiting shield() is cancelled, that caller still receives CancelledError, while cancellation is not propagated through the shield to the protected task. If the protected task is cancelled independently, however, the shield is cancelled too. Python also explicitly warns callers to keep a strong reference to tasks passed to shield().
That creates an operationally dangerous false-positive signal. A log line such as “request cancelled,” an exception handler that catches CancelledError, or a cancelled waiter task can look like a terminal answer. It is not. The release question is: what independently proves the protected task’s final state and the intended effect?
This playbook treats that as a bounded acceptance problem. The fixture uses only synthetic state, explicit synchronization barriers, a separately authored expected-case manifest, a raw evidence ledger, and a fail-closed decision of ACCEPT / REPAIR / RERUN / HOLD. The executed observations below are from CPython 3.13.5 only. Cases for other interpreter versions remain EXPECTED / NOT EXECUTED until rerun. Nothing in this procedure treats a waiter’s cancellation as a proxy for protected-task completion.
Define the operational acceptance contract
The contract must name two distinct objects: the waiter, which executes await asyncio.shield(worker_task), and the protected worker task. Conflating them is the defect this validation is designed to expose.
For the canonical shielded case, acceptance requires all of the following: the waiter receives and propagates CancelledError; immediately after that waiter cancellation is observed, the protected task remains neither done nor cancelled; the protected task is subsequently allowed to continue; its terminal state is inspected independently; and the synthetic effect ledger proves whether the declared operation committed. Python documents the first half of that relationship directly: caller cancellation does not cancel the task running inside shield(), although the caller’s await still raises CancelledError.
The fixture also requires a negative control without shield(). When a task directly awaits another task, cancellation of the waiter can propagate into the awaited task. That control prevents a defective harness (one that simply assumes every worker survives) from producing a convincing but meaningless green result.
Use four evidence classes:
Evidence | Required assertion |
Waiter terminal state | cancelled, success, or failed |
Worker terminal state | pending, cancelled, success, or failed |
Boundary snapshot | worker state immediately after waiter cancellation |
Effect evidence | explicit synthetic commit record, not inferred from task state |
The minimum command sequence is equally explicit:
python3 --version
python3 shield_fixture.py evidence/
python3 validate.py expected-cases.json evidence/observed-summary.json
sha256sum shield_fixture.py expected-cases.json validate.py \
  evidence/observed-summary.json evidence/evidence.jsonl
The methodological overlap with Refonte Learning’s Kubernetes shutdown-budget validation playbook is evidence separation, not subject matter: that article distinguishes lifecycle boundaries instead of trusting a single “hook ran” signal. The asyncio problem is different, but the same acceptance discipline applies.
Reject the release if a report contains only CancelledError, task.cancelled(), an application log message, or elapsed time. None independently establishes both protected-task terminal state and declared effect.
Pin the documented baseline
Four Python documentation surfaces define the baseline.
First, asyncio.shield() protects the supplied awaitable from cancellation propagating from the awaiting coroutine. If the outer coroutine is cancelled, its await still raises CancelledError, while the protected task is not cancelled for that reason. Conversely, if the protected operation is cancelled by another path, the shield is cancelled too. If a coroutine rather than an existing task is passed to shield(), Python automatically schedules it as a task.
Second, Future and Task terminal states are not binary “worked/did not work.” done() means a result, exception, or cancellation is terminal; result() raises CancelledError for a cancelled future and re-raises a stored exception for exceptional completion; exception() likewise distinguishes cancellation, failure, and normal success. Future cancellation returns False when the Future is already done or cancelled.
Third, asyncio.CancelledError directly subclasses BaseException, not Exception, and Python says that when it is explicitly caught for cancellation cleanup it should ordinarily be re-raised.
Fourth, event-loop execution order should be controlled with synchronization primitives, not with guessed wall-clock sleeps. The event-loop reference describes scheduling behavior and identifies loop.time() as an internal monotonic clock. This fixture uses Event barriers and a single await asyncio.sleep(0) only to yield control where a task must enter its await point; it does not claim latency or scheduling performance.
These statements establish expected semantics. They do not substitute for runtime evidence on the release candidate.
Pin exact runtime versions
The executed preparation run used:
implementation: CPython
python: 3.13.5
build: 3.13.5 (main, Jul 15 2026, 20:25:40) [GCC 14.2.0]
platform: Linux-6.18.57-x86_64-with-glibc2.41
asyncio: /usr/lib/python3.13/asyncio/__init__.py
external dependencies: none
Python.org records CPython 3.13.5 as the fifth 3.13 maintenance release, released June 11, 2025; it has since been superseded within the 3.13 series. The documentation consulted here is the current Python 3.13 documentation, presently rendered as 3.13.18. Its shield() entry contains no 3.13-specific change note to the shielding rule itself; nevertheless, this report deliberately does not promote the 3.13.5 execution result into an observed result for 3.13.18 or another branch.
Boundary case: deploy the same code under 3.13.18 or 3.14.x.
Expected result: the documented shield relationship remains the oracle.
Rejection criterion: version identity differs from the accepted runtime and no fresh evidence bundle exists. Decision: RERUN, not implicit ACCEPT.
Build an isolated reproducible fixture
The fixture must make the cancellation boundary deterministic without reaching external systems. A pair of asyncio.Event objects supplies the barriers: started proves the worker entered the controlled region; release prevents it from reaching success or failure until the controller has cancelled and reconciled the waiter.
The worker owns one synthetic effect: appending effect_committed to the evidence ledger immediately before returning "synthetic-commit". No network, database, filesystem mutation, signal handler, or nondeterministic timeout is part of the behavior under test.
A compact executable core is:
import asyncio

class SyntheticFailure(RuntimeError):
    pass

async def worker(log, started, release, mode):
    log("worker_started", "worker")
    started.set()
    try:
        await release.wait()
        log("worker_released", "worker")

        if mode == "fail":
            log("worker_raising", "worker", exc="SyntheticFailure")
            raise SyntheticFailure("synthetic worker failure")

        log("effect_committed", "worker", value="synthetic-commit")
        return "synthetic-commit"

    except asyncio.CancelledError:
        log("worker_cancelled", "worker")
        raise

async def waiter(log, task, shielded):
    log("waiter_started", "waiter", shielded=shielded)
    try:
        result = (
            await asyncio.shield(task)
            if shielded else
            await task
        )
        log("waiter_returned", "waiter", result=result)
        return result
    except asyncio.CancelledError:
        log("waiter_cancelled", "waiter")
        raise
    except Exception as exc:
        log("waiter_failed", "waiter", exc=type(exc).__name__)
        raise
Keep explicit references to both worker_task and waiter_task. Python specifically warns that the event loop keeps only weak references to tasks and instructs callers to retain a reference to tasks passed to shield().
The SQLite WAL committed-row validation playbook is relevant methodologically because it separates apparent artifact success from independently verified logical state and uses a controlled synthetic fixture.
Fixture rejection criteria are simple: external dependencies appear; sleeps become correctness barriers; expected results are generated from observed output; the worker reference is dropped; or success is inferred without the effect record.
Write the independent expected-case manifest
Write expected cases before reconciling the run. Do not generate them from observed-summary.json; doing so converts the oracle into a restatement of the implementation.
The manifest used for this run is:
{
  "schema_version": 1,
  "runtime": {
    "implementation": "CPython",
    "python_exact": "3.13.5"
  },
  "cases": {
    "S1_SHIELD_WAITER_CANCEL_WORKER_SUCCESS": {
      "status": "EXPECTED",
      "waiter_terminal": "cancelled",
      "worker_terminal": "success",
      "effect_committed": true,
      "waiter_cancel_return": true,
      "worker_pending_after_waiter_cancel": true
    },
    "N1_DIRECT_AWAIT_WAITER_CANCEL_WORKER_CANCELLED": {
      "status": "EXPECTED",
      "waiter_terminal": "cancelled",
      "worker_terminal": "cancelled",
      "effect_committed": false,
      "waiter_cancel_return": true,
      "worker_pending_after_waiter_cancel": false
    },
    "S2_SHIELD_WAITER_CANCEL_WORKER_FAILURE": {
      "status": "EXPECTED",
      "waiter_terminal": "cancelled",
      "worker_terminal": "failed",
      "effect_committed": false,
      "waiter_cancel_return": true,
      "worker_pending_after_waiter_cancel": true,
      "worker_exception": "SyntheticFailure"
    },
    "S3_INNER_CANCEL_WHILE_SHIELDED": {
      "status": "EXPECTED",
      "waiter_terminal": "cancelled",
      "worker_terminal": "cancelled",
      "effect_committed": false,
      "worker_cancel_return": true
    },
    "B1_COMPLETION_PRECEDES_WAITER_CANCEL": {
      "status": "EXPECTED",
      "waiter_terminal": "success",
      "worker_terminal": "success",
      "effect_committed": true,
      "waiter_cancel_return": false
    },
    "V1_CPYTHON_3_13_18_REVALIDATION": {
      "status": "EXPECTED / NOT EXECUTED"
    },
    "V2_CPYTHON_3_14_7_REVALIDATION": {
      "status": "EXPECTED / NOT EXECUTED"
    }
  }
}
The last two entries matter. Documentation may support the same expectation, but this evidence package contains no observation for those interpreters. They remain EXPECTED / NOT EXECUTED.
The manifest should be immutable for a given run. If evidence disagrees, change the implementation, explain a changed contract, or create a new manifest version. Never edit expected values merely to make the validator green.
Preserve a negative control
N1_DIRECT_AWAIT_WAITER_CANCEL_WORKER_CANCELLED removes exactly one variable: shield().
Boundary case: worker blocks at release.wait(), waiter directly awaits the worker, controller cancels the waiter.
Expected result: cancellation reaches the directly awaited worker; both tasks terminate cancelled; no synthetic commit appears.
Rejection criterion: the negative control reports the worker as successful or still pending after the cancelled direct await. Such a result means the harness does not discriminate the semantic boundary it claims to test.
The negative control is especially important because a broken fixture could accidentally release the worker before cancellation and still produce plausible “worker completed” output.
Reproduce the misleading success
The misleading signal is produced in S1_SHIELD_WAITER_CANCEL_WORKER_SUCCESS.
The sequence is deliberately ordered:
worker_task = asyncio.create_task(
    worker(log, started, release, "success")
)
waiter_task = asyncio.create_task(
    waiter(log, worker_task, shielded=True)
)

await started.wait()
await asyncio.sleep(0)

cancel_return = waiter_task.cancel("synthetic waiter cancellation")

try:
    await waiter_task
except asyncio.CancelledError:
    pass

pending_after_cancel = (
    not worker_task.done()
    and not worker_task.cancelled()
)

release.set()
result = await worker_task
The CancelledError is real. The waiter task really becomes cancelled. But that event answers only the waiter question.
In the executed CPython 3.13.5 run, the ledger sequence was:
worker_started
waiter_started shielded=true
waiter_cancel_requested returned=true
waiter_cancelled
worker_snapshot_after_waiter_cancel done=false cancelled=false
worker_released
effect_committed value=synthetic-commit
Those are observed results from the preparation run, not merely expected results.
The crucial evidence is event 5 followed by event 7. At the point where the caller already has a cancellation outcome, the worker is demonstrably still pending. It later commits the synthetic effect and returns successfully.
That is the false-positive pattern to eliminate in production diagnostics: “the await was cancelled, therefore the work did not finish.” Python’s shield contract says that conclusion does not follow.
The inverse mistake is equally dangerous: “shield protected it, therefore the work finished.” Shielding prevents one cancellation path. It does not guarantee successful completion.
Run the controlled comparison
A meaningful comparison changes cancellation topology, not timing.
The executed summaries were:
Case | Waiter | Protected/direct worker | Effect | Status |
S1 shield + waiter cancel | cancelled | success | committed | OBSERVED |
N1 direct await + waiter cancel | cancelled | cancelled | absent | OBSERVED |
S2 shield + waiter cancel + later failure | cancelled | failed | absent | OBSERVED |
S3 shield + direct worker cancel | cancelled | cancelled | absent | OBSERVED |
B1 completion before cancel | success | success | committed | OBSERVED |
V1 CPython 3.13.18 | Not executed | Not executed | Not executed | EXPECTED / NOT EXECUTED |
V2 CPython 3.14.7 | Not executed | Not executed | Not executed | EXPECTED / NOT EXECUTED |
The table is the core reconciliation. The same visible waiter outcome, “cancelled,” coexists with three different worker outcomes: success, failure, and cancellation. That is precisely why waiter cancellation cannot be a completion oracle.
The N1 result is consistent with the absence of a shield boundary; the S1 result is consistent with Python’s documented shield semantics; S3 exercises the explicitly documented exception that cancelling the inner operation by another means also cancels the shield.
The comparison also uses Future/Task state classification correctly. A task being done() is not enough because “done” includes cancellation, normal result, and exception. Independent inspection must therefore branch on cancelled(), then retrieve the exception or result only where valid.
The Java periodic-task exception validation playbook addresses a different runtime and failure mechanism, but its useful parallel is object-level lifecycle inspection: an apparently healthy executor does not prove a particular scheduled future remains healthy. Here, a cancelled waiter does not prove a particular protected task’s terminal state.
Assert the failure boundary
S2 is the decisive boundary case.
The waiter is cancelled while the shielded worker is blocked. Immediately afterward, the worker is still pending. Only then is the worker released, and it raises SyntheticFailure.
Expected result: waiter cancelled; worker failed; worker_exception == "SyntheticFailure"; effect absent.
Executed CPython 3.13.5 result: exactly that classification was observed.
Rejection criterion: classifying the case as “successful because shield worked” or “cancelled because the waiter was cancelled.” Shield protected continuation from one cancellation source; it did not convert a later worker exception into success.
This case prevents an over-repair in which engineers respond to cancellation ambiguity by treating every surviving shielded operation as successful.
Test failure and boundary cases
Five cases are sufficient for the narrow acceptance contract because each establishes a different state transition.
S1 proves outer waiter cancellation can coexist with later worker success.
N1 proves the harness can detect the non-shielded propagation path.
S2 proves survival of waiter cancellation does not imply worker success.
S3 proves shield is not an unconditional cancellation blocker: Python states that cancellation of the protected operation by another means also cancels shield().
B1 proves cancellation requests are themselves state-dependent. The worker is released and the waiter returns successfully before waiter_task.cancel() is attempted. The executed run observed cancel() returning False, with both tasks already successful. Future documentation specifies the corresponding terminal-state principle: cancellation of an already done or cancelled Future returns False; Task documentation similarly defines cancellation as a request whose effect depends on task state and coroutine behavior.
Do not add timing cases merely to enlarge coverage. “Cancel after 10 ms,” “cancel after 100 ms,” and “sleep for one second and inspect” are weaker than explicit barriers because their meaning depends on machine load and scheduling.
Useful later extensions should remain separately declared and, until actually executed, marked EXPECTED / NOT EXECUTED. Examples include passing a coroutine directly to shield() rather than an already created task, exercising a custom task factory, or testing another Python patch release. Python documents that shield() automatically schedules a coroutine argument and that event loops may support task-factory customization, but neither behavior was executed in this evidence set.
Do not broaden the release claim to them.
Capture raw evidence
The evidence ledger is append-only JSON Lines. Each event contains a case identifier, per-case sequence number, role, event name, and only the fields relevant to that event.
Representative executed records are:
{"case":"S1_SHIELD_WAITER_CANCEL_WORKER_SUCCESS",
 "seq":3,"event":"waiter_cancel_requested",
 "role":"controller","returned":true}

{"case":"S1_SHIELD_WAITER_CANCEL_WORKER_SUCCESS",
 "seq":4,"event":"waiter_cancelled","role":"waiter"}

{"case":"S1_SHIELD_WAITER_CANCEL_WORKER_SUCCESS",
 "seq":5,"event":"worker_snapshot_after_waiter_cancel",
 "role":"controller","done":false,"cancelled":false}

{"case":"S1_SHIELD_WAITER_CANCEL_WORKER_SUCCESS",
 "seq":7,"event":"effect_committed",
 "role":"worker","value":"synthetic-commit"}
The preparation run produced these SHA-256 digests:
a44ce2838ef6c11534af59c19972a45e3cfe974a8f20294299d5a642ca70fee8
  shield_fixture.py

6c018a085bf9f2c5078a581c9c587a068299d35178f45239e774fc64a8096253
  expected-cases.json

c2529dab84356e8428110bd0c65be8aad91c6361f46b20245c59c4f6116bb4aa
  validate.py

6fc7665fb519f79f9695deb0b6e3c318ada49b11933fb47465153a911c0b2f2b
  observed-summary.json

5e36bf997b577b36a7a6efb5b2ba2749b5b1c6a8aab822148086e37958feff15
  evidence.jsonl
Those hashes are evidence identity, not behavioral proof. They let a reviewer establish which fixture, oracle, validator, summary, and ledger belong together.
Do not make timestamps primary acceptance fields. Event-loop timing can be recorded diagnostically using loop.time(), whose value comes from the loop’s monotonic clock, but ordering here is stronger because explicit synchronization determines the causal boundary.
Detect missing evidence
A case is not accepted merely because no contradiction appears.
Boundary case: the ledger contains waiter_cancelled but lacks both the worker terminal classification and a synthetic effect record.
Expected decision: HOLD.
Rejection criterion: treating absence of a worker failure record as success.
The same applies if a task reference was not retained. Python’s documentation warns that task references must be kept because the event loop maintains weak references; losing the evidence subject undermines the qualification path.
Missing evidence and negative evidence are different. “No commit record captured” is not automatically “commit did not happen” unless the fixture guarantees that every commit path emits the record and the ledger itself is complete.
Reconcile the actual state
Reconciliation compares manifest identity to observed identity case by case and field by field. It never asks only whether the process exited zero.
The validator is intentionally dull:
import json
import sys
from pathlib import Path

manifest = json.loads(Path(sys.argv[1]).read_text())
observed = {
    row["case"]: row
    for row in json.loads(Path(sys.argv[2]).read_text())
}

errors = []

for case, expected in manifest["cases"].items():
    if expected["status"] != "EXPECTED":
        continue

    actual = observed.get(case)
    if actual is None:
        errors.append(f"{case}: missing observed summary")
        continue

    for key, value in expected.items():
        if key == "status":
            continue
        if actual.get(key) != value:
            errors.append(
                f"{case}.{key}: expected {value!r}, "
                f"got {actual.get(key)!r}"
            )

print({
    "result": "PASS" if not errors else "FAIL",
    "errors": errors,
})
raise SystemExit(bool(errors))
For the CPython 3.13.5 preparation execution, this validator returned:
result: PASS
errors: []
That statement is an observed test outcome for the captured files above.
The reconciliation should answer three separate questions for every shielded case: what happened to the waiter; what happened to the worker; what happened to the declared effect. A two-column report is insufficient because worker success and effect success are not interchangeable in a real system. The fixture deliberately places the effect marker immediately before the successful return so their relationship is controlled locally; a database write, remote API, queue publish, or transaction would require its own independent state evidence.
That evidence-first pattern resembles Refonte Learning’s pandas missing-key reconciliation playbook, which checks row identity rather than trusting plausible aggregates. Its focus is data-group membership rather than asyncio cancellation.
Separate documented from observed behavior
A release record should label epistemic status explicitly.
Statement | Classification |
Outer cancellation does not propagate through shield() to the protected task | DOCUMENTED |
Caller awaiting shield() still receives CancelledError | DOCUMENTED |
Independent cancellation of the inner operation cancels the shield | DOCUMENTED |
Tasks passed to shield() should be strongly referenced | DOCUMENTED |
S1 worker was pending after waiter cancellation under CPython 3.13.5 | OBSERVED |
S1 later committed synthetic effect and returned successfully | OBSERVED |
S2 later raised SyntheticFailure | OBSERVED |
Same fixture will pass on CPython 3.13.18 | EXPECTED / NOT EXECUTED |
Same fixture will pass on CPython 3.14.7 | EXPECTED / NOT EXECUTED |
Production side effect will be idempotent | NOT ESTABLISHED |
The documented rows come directly from Python’s shield, task, Future, exception, and event-loop references.
The observed rows come only from the captured preparation run.
The final row illustrates a common invalid inference. asyncio.shield() controls cancellation propagation at one await boundary. It says nothing about transactional atomicity, duplicate suppression, idempotency keys, remote acknowledgement durability, or application-level rollback. Those require domain evidence outside this narrow fixture.
A second limitation is interpreter scope. The Python 3.13 documentation currently reflects a later 3.13 maintenance release than the executed 3.13.5 binary. That is acceptable for defining the documented series contract, but not for relabeling unexecuted runtimes as observed. The version gate remains intentional.
Measure the repair boundary
Boundary case: an application currently catches CancelledError around await asyncio.shield(task) and records the operation as “failed.”
Expected repair: change only the status model and evidence collection needed to represent the worker as unresolved until independently reconciled.
Rejection criterion: cancelling the protected task merely to make waiter and worker status agree, or swallowing cancellation and presenting the waiter as successful.
Python explicitly recommends propagating CancelledError after cleanup in normal cancellation handling, and warns against casually suppressing cancellation state.
The smallest repair preserves both truths: the caller was cancelled; protected work may still be running.
Apply the smallest safe repair
A production repair should introduce an explicit ownership record for shielded work rather than rewrite cancellation semantics.
A minimal pattern is:
async def submit_and_wait(payload, registry):
    task = asyncio.create_task(
        perform_operation(payload),
        name=f"operation:{payload.id}",
    )
    registry[payload.id] = task

    try:
        return await asyncio.shield(task)

    except asyncio.CancelledError:
        record_waiter_cancelled(payload.id)
        raise

    finally:
        if task.done():
            reconcile_terminal_task(payload.id, task)
The critical detail is that reconciliation must also exist after the cancelled waiter is gone. A long-lived owner, request coordinator, task group suited to the application’s lifecycle, or explicit registry callback may perform that job. Simply placing reconciliation in the waiter’s post-shield() code is insufficient because the waiter is the component being cancelled.
A done callback can capture terminal classification, but retrieve exceptions deliberately. Python notes that unawaited tasks whose exceptions are never retrieved can produce “Task exception was never retrieved” diagnostics; its task documentation also emphasizes keeping task references.
A robust callback therefore distinguishes:
def on_done(task):
    if task.cancelled():
        record_worker_cancelled(task.get_name())
        return

    exc = task.exception()
    if exc is not None:
        record_worker_failed(task.get_name(), type(exc).__name__)
        return

    record_worker_succeeded(task.get_name(), task.result())
Do not repair this by catching CancelledError and returning None unless the application contract intentionally suppresses cancellation. Python shows such suppression as possible but explicitly labels completely ignoring cancellation as not recommended.
The operational fix is therefore observability and lifecycle ownership, not semantic camouflage.
Test rollback and rerun safety
A rerun must be able to distinguish a fresh validation attempt from residue left by the previous one.
The synthetic fixture achieves this cheaply: every invocation creates new in-memory Events, new tasks, and a new output directory. For production-like qualification, use a run ID and isolate side effects by namespace, transaction, temporary database, mock service, or disposable environment. Never rerun a case against an unknown partially completed operation and then call the second attempt proof of the first.
Rollback evidence should answer: what external state existed before the attempt; which operation identity was used; whether the first protected task reached a terminal state; whether compensating action was applied; and whether retrying can duplicate a committed effect. Shield itself provides no answer to those questions.
The Ansible check-mode task-coverage validation playbook is relevant because it distinguishes predicted behavior from evidence of what actually ran. That page focuses on infrastructure automation rather than coroutine cancellation.
For this fixture, a repeat execution is safe because the effect is only the literal synthetic ledger entry. For a real payment, message publish, file promotion, or database mutation, rerun approval must be owned by the subsystem that defines idempotency.
The release rule is fail-closed:
same manifest + clean isolated state + same pinned runtime
    -> rerun eligible

unknown prior protected-task state
    -> HOLD

known failed test implementation
    -> REPAIR, then new run

environmental interruption with evidence preserved
    -> RERUN

production side effect possibly committed but unreconciled
    -> HOLD, never blind retry
Assign operational ownership
Boundary case: waiter is cancelled, protected task remains pending, and the request-handling coroutine exits.
Expected state: another named component retains the task reference and is responsible for terminal reconciliation.
Rejection criterion: “background task will probably finish” with no retained reference, terminal callback, registry, or owning scope.
Python’s weak-reference warning makes this more than an organizational nicety. A shielded task whose caller disappears still needs a durable owner in the application design.
Ownership should name four roles even if one engineer fills several: code owner for cancellation behavior; evidence owner for ledger integrity; operation owner for external side-effect reconciliation; release owner for the final gate.
Make the release decision
The final decision must be derived from the evidence bundle, not from the most reassuring log line.
Condition | Decision | Required action |
Pinned runtime, complete evidence, manifest matches, negative control discriminates correctly | ACCEPT | Archive manifest, hashes, ledger, summary and runtime identity |
Harness or implementation defect explains mismatch and original evidence is preserved | REPAIR | Fix smallest defect, create a new run, never rewrite old observations |
Environment/version changed or a run was interrupted before complete evidence, with no ambiguous external effect | RERUN | Re-execute the unchanged manifest in a clean fixture |
Protected task/effect state cannot be independently established | HOLD | Reconcile state before retry or release |
For the preparation fixture actually executed under CPython 3.13.5, the five executed cases matched the independent manifest and the validator returned PASS. The appropriate fixture-level decision for that captured evidence package is ACCEPT.
That acceptance is intentionally narrow. It means the fixture demonstrated the expected distinction between shield waiter cancellation and protected-task terminal state on that runtime. It does not accept a production service, a different Python patch version, a different event-loop implementation, or an external side-effect protocol.
The strongest release assertion is therefore:
A cancelled waiter is evidence about the waiter. Protected-task completion must be established independently.
That statement follows both the Python contract and the executed comparison. Python documents that shield() prevents cancellation propagation from the caller while still allowing the caller to receive CancelledError, and that direct cancellation of the protected operation remains possible.
Any system that reduces those states to one “cancelled” boolean has discarded information required for safe operational acceptance.
Connect the practice to Refonte Learning
Refonte Learning’s current Backend Development program is described in the catalog as a three-month program with a stated dedication of 10–12 hours per week and a basic-programming-concepts prerequisite. Its listed competencies include Node.js and Express, MongoDB and SQL, REST APIs and microservices, authentication and authorization, testing and debugging, and deployment with Docker and cloud platforms; it also describes hands-on projects and a potential internship.
These topics connect the playbook to broader backend engineering practice, particularly testing, debugging, API lifecycle behavior, and evidence-based release decisions. This connection does not imply that the program teaches this specific asyncio.shield() fixture or includes mentorship or specialized asyncio instruction. Engineers evaluating the program should use the current catalog page as the authority for program details.