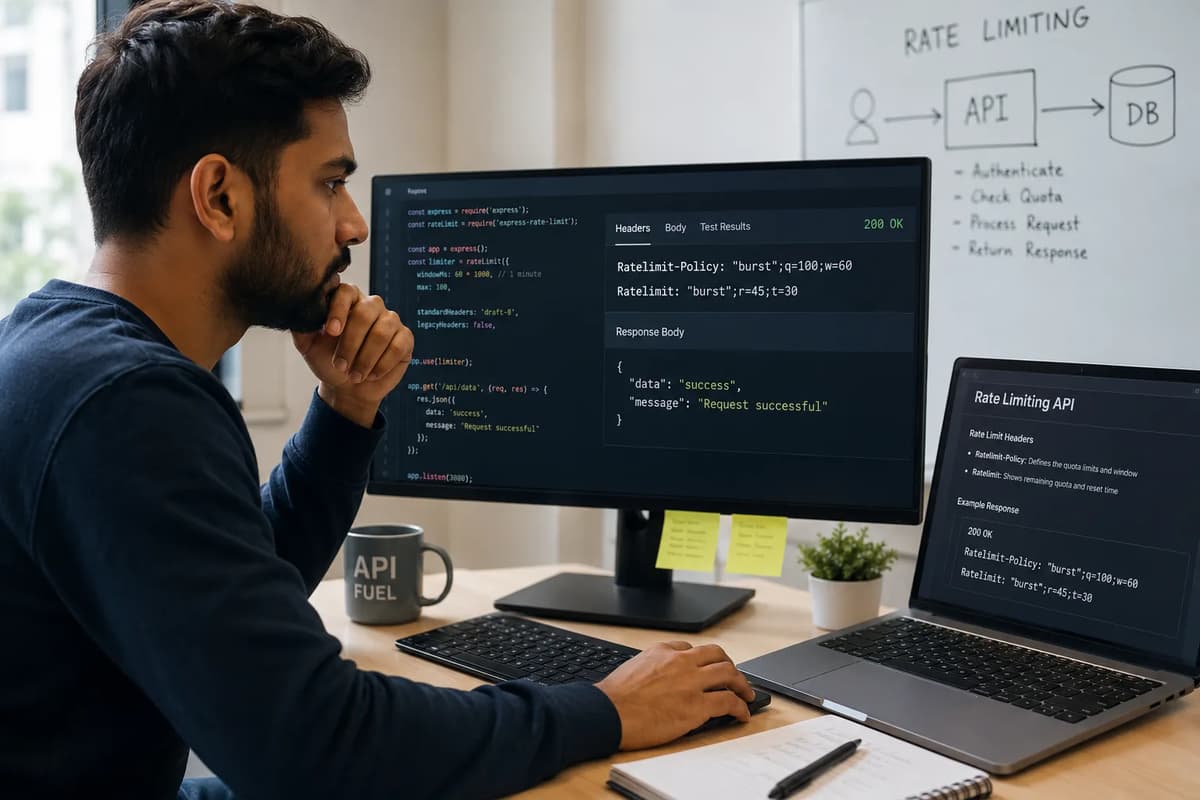
Opening a conversation with a frustrated client who notices your API’s X-RateLimit headers don’t match their expectation has probably happened to you. As an API developer with years of experience, I’ve fielded that exact question: “Why doesn’t your RateLimit header look like GitHub’s?” The truth is, today every major API has its own rate-limit headers. Stripe returns Stripe-Rate-Limited-Reason; GitHub sends X-RateLimit-Limit and friends; others use yet more variations. In response, the IETF’s HTTPAPI working group is actively defining a new, standardized set of RateLimit headers to replace this tangle. In this article, we’ll demystify the IETF’s RateLimit-Policy and RateLimit headers (and related error types), see who’s already using them, and show how to implement them in a Node.js API. Along the way we’ll tie this into the Refonte Learning APIs Developer Program’s focus on error handling, versioning, and API documentation. By the end, you’ll understand the new draft standard (and why your integrator cares) and how to adopt it confidently.
Every API Has Its Own Rate-Limit Headers Right Now
Right now, there is no single standard for expressing rate-limit information in HTTP responses. Instead, each API chooses its own header names and format. For example:
GitHub: Uses proprietary X-RateLimit-* headers such as X-RateLimit-Limit, X-RateLimit-Remaining, X-RateLimit-Used, X-RateLimit-Reset (in seconds since epoch), plus an X-RateLimit-Resource header to identify which quota applies. On errors (403/429) it often sets X-RateLimit-Remaining: 0 and relies on X-RateLimit-Reset or Retry-After to tell clients when to try again.
Stripe: Returns a 429 Too Many Requests status and a custom Stripe-Rate-Limited-Reason header to explain the kind of limit hit (e.g. global-rate, endpoint-rate, etc.). It does not use the X-RateLimit-* names at all.
Others: Many APIs (Twitter, Reddit, etc.) all have their own names and semantics for rate-limit headers. For instance, the example below from Postman’s blog shows a generic pattern used by many services (here GitHub’s style):
HTTP/1.1 200 OK
X-RateLimit-Limit: 1000
X-RateLimit-Remaining: 847
X-RateLimit-Reset: 1677721600
Even though these headers work, they are not consistent across APIs.
In summary, each vendor has been free to invent: GitHub’s X-RateLimit-*, Stripe’s Stripe-Rate-Limited-Reason, etc. This fragmented ecosystem leads to confusion. Clients often have to write bespoke code for every API they use. For example, an integrator might expect a RateLimit-Remaining header (some APIs call it that) but your API named it differently, sparking the exact confusion we’re addressing. The IETF draft aims to replace all these custom fields with a single standardized structure. (For a contrast, see Refonte’s “Building Secure and Scalable APIs in 2026” post, which discusses general best-practices but doesn’t deal with this specific standardization topic.)
The IETF Draft, Explained
In mid-2026, the IETF HTTPAPI working group advanced draft-ietf-httpapi-ratelimit-headers (version 11 as of May 23, 2026) toward standardization. This draft (expected to become an RFC) defines two new header fields for rate limiting:
RateLimit-Policy: A structured header describing the quota policy itself. It encodes the total allowed request quota (q=), the time window in seconds (w=), and optional tags or partition keys. For example, Cloudflare uses Ratelimit-Policy: "burst";q=100;w=60 to mean “a burst limit of 100 requests per 60 seconds”. Multiple policies can be listed in a comma-separated structured list if needed.
RateLimit: A structured header conveying the current state of the quota for the response. It includes the name of the policy, the remaining requests (r=) and the time until the quota resets (t=). For instance, RateLimit: "burst";r=50;t=30 (as seen in Cloudflare docs) means “50 requests remaining, reset in 30 seconds”.
In practice, an API would send both headers on successful responses so clients can see both “you have X quota in total” and “you have Y quota left until time T.” The syntax is based on HTTP structured fields (RFC 8941) to allow unambiguous parsing.
RateLimit-Policy vs. RateLimit, What Each One Carries
Header | Purpose | Example (structured syntax) |
RateLimit-Policy | Describes each quota policy’s limits and windows. For each policy: a name (quoted string), total quota (q=<integer>), and window (w=<seconds>). An optional p=<partition> parameter can tag policies. | "normal";q=500;w=3600 (policy “normal”, 500 requests per hour) |
RateLimit | Reports current usage against each policy. For each policy: the name, remaining quota (r=<integer>), and time-to-reset (t=<seconds>). | "normal";r=123;t=1800 (123 remaining, resets in 30 mins) |
Both headers can include multiple policies (comma-separated lists). For example, if an API had a “default” and a “burst” policy, you might see:
RateLimit-Policy: "default";q=1000;w=3600, "burst";q=100;w=60
RateLimit: "default";r=800;t=1800, "burst";r=20;t=30
The IETF draft spells out this structure in detail.
Importantly, neither header replaces the HTTP status code. The API still returns the usual 200 OK, 429 Too Many Requests, etc. The headers merely inform the client about limits. (If a limit is exceeded, the server would use a 429 code and could include these headers to say the quota is 0.)
The Three Standardized Problem Types
Along with the headers, the draft also standardizes three “problem type” URIs (for use in an application/problem+json 4xx/5xx body) to describe rate-limit errors. They are:
quota-exceeded: Use this when the client’s requests exceeded a configured quota policy. The problem response can include a "violated-policies" array naming which policies were hit. Example:
HTTP/1.1 429 Too Many Requests
Content-Type: application/problem+json
{
"type": "https://iana.org/assignments/http-problem-types#quota-exceeded",
"title": "Request cannot be satisfied as assigned quota has been exceeded",
"violated-policies": ["daily","bandwidth"]
}
This tells the client it violated one or more specific policies.
temporary-reduced-capacity: Use this when the server is temporarily capacity-limited, not because of the client’s behavior per se. For instance, the service is overloaded or in a degraded state. The response may include a RateLimit-Policy indicating the new lowered quota, and "violated-policies" naming which policies are affected. Example:
HTTP/1.1 503 Server Unavailable
Content-Type: application/problem+json
{
"type": "https://iana.org/assignments/http-problem-types#temporary-reduced-capacity",
"title": "Request cannot be satisfied due to temporary server capacity constraints",
"violated-policies": ["hourly"]
}
abnormal-usage-detected: Use this to signal that the client’s pattern of requests appears malicious or anomalous. It means “we think you might be doing something abusive.” Like quota-exceeded, it can list "violated-policies", but it indicates a behavioral issue. Example:
HTTP/1.1 429 Too Many Requests
Content-Type: application/problem+json
{
"type": "https://iana.org/assignments/http-problem-types#abnormal-usage-detected",
"title": "Request not satisfied due to detection of abnormal request pattern",
"violated-policies": ["hourly"]
}
By standardizing these problem types, clients and monitoring tools can recognize why a 429/503 was returned. This is more informative than a generic 429. (Note: while RFC 7807-style problem responses are optional, they fit well here.) Together, the new headers and problems give a full picture of quota policy (RateLimit-Policy), current usage (RateLimit), and error reasons (problem types).
Where This Sits in the IETF Process
It’s easy to be confused by the fact this is still a “Draft” (not yet RFC). In the IETF lifecycle, all new protocols start as Internet-Drafts that expire after 6 months, and drafts are often revised. As of May 23, 2026, the ratelimit draft is on version 11 and is set to expire Nov 24, 2026. That expiration is normal, not a sign of failure. Expect updated versions or eventual publication as an RFC if all goes well.
Recall that the HTTPAPI Working Group has recently produced related standards. For instance, RFC 9745 (“Deprecation” header) was approved in June 2024, adding a standard Deprecation response header to signal retiring an API. Similarly, RFC 9727 (“api-catalog” Well-Known URI) was published in June 2025. These were sibling efforts: the same working group (HTTPAPI) tackled them. The Deprecation header (RFC 9745) has status “permanent” in the HTTP field registry, showing this group’s results.
What “Draft,” Not “RFC,” Means Here
At the moment, draft-ietf-httpapi-ratelimit-headers-11 is in progress. It has IESG approval as a Proposed Standard pending publication. The November 2026 date means authors need to publish the next revision or the document is simply updated in the queue. In practice, many vendors (including Cloudflare, discussed below) are already implementing the draft’s format before official RFC status. Even in draft form, it is reasonable to start experimenting with these headers in your API, as long as you note that the format is still evolving. The Refonte API program’s “Versioning and Deprecation” module is a useful foundation for understanding these processes, though it does not teach this specific draft by name.
GitHub's Legacy Headers: A Case Study in the Old Way
To see the contrast, consider GitHub’s REST API. GitHub is a major API provider that still uses only the old proprietary headers. Its docs list:
X-RateLimit-Limit
X-RateLimit-Remaining
X-RateLimit-Used
X-RateLimit-Reset (a Unix epoch timestamp)
X-RateLimit-Resource
GitHub does not provide RateLimit or RateLimit-Policy. The table below summarizes how GitHub describes its legacy fields.
GitHub Legacy Headers | Meaning |
X-RateLimit-Limit | The number of requests allowed in the current window |
X-RateLimit-Remaining | How many requests remain in the window |
X-RateLimit-Used | How many requests have been made in the window |
X-RateLimit-Reset | UTC epoch seconds when the window resets |
X-RateLimit-Resource | Which resource/category the limit applies to |
When a client exceeds GitHub’s primary rate limit, the API returns HTTP 403 or 429, with X-RateLimit-Remaining: 0 and an instruction not to retry until the time in X-RateLimit-Reset. For secondary rate limits, GitHub returns a Retry-After header. These GitHub headers work, but they illustrate the old style: separate fields, inconsistent names, and they don’t directly carry any structured meaning beyond flat numbers.
By contrast, the new IETF headers would let GitHub provide something like RateLimit-Policy: "core";q=5000;w=3600 and RateLimit: "core";r=1234;t=1800 (if it chose to implement the draft). This would standardize what it means to exceed “core” usage. However, as of now GitHub has not mentioned adopting the draft. Its docs make no reference to the IETF effort.
Cloudflare's Headers: A Case Study in Early Adoption
Meanwhile, Cloudflare has been an early adopter of the draft’s format. In a September 2025 blog post, Cloudflare announced new rate-limit headers on its API following “the pattern developed by the IETF draft on rate limiting”. What Cloudflare actually emits are Ratelimit-Policy and Ratelimit headers with structured values exactly matching the draft’s syntax. For example, the Cloudflare docs show:
Cloudflare (IETF-like) Header | Value Explanation |
Ratelimit-Policy | For example: "burst";q=100;w=60 means policy named “burst”, allowing 100 requests per 60 seconds. |
Ratelimit | For example: "burst";r=50;t=30 means 50 remaining, resets in 30s. |
These headers use the same abbreviations (q, w, r, t) that the IETF draft defines. Cloudflare’s announcement explicitly says it is “using the pattern developed by the IETF draft,” though it does not label its headers as a formal IETF standard; it simply notes that they align. In practice, when you inspect Cloudflare API responses after a rate-limit hit, you will see both values in the response headers. For example:
Ratelimit-Policy: "burst";q=100;w=60
Ratelimit: "burst";r=20;t=10
A 429 response may also include a Retry-After header.
Thus, Cloudflare’s case shows how the new format can work today: they implemented the draft’s header names and syntax before an RFC was published. Other platforms may follow, but as of writing GitHub and many others have not made this switch. Cloudflare’s example proves the draft is implementable; just note that their docs merely match the syntax but don’t claim official “IETF compliance.” It’s an observed alignment.
Implementing RateLimit Headers in Node.js
If you’re using Node.js and Express, you can quickly emit the new RateLimit headers using existing middleware. A popular choice is express-rate-limit. In recent versions, this middleware has built-in support for the IETF draft. Here’s how to use it:
1. Install express-rate-limit:
npm install express-rate-limit
2. Configure the limiter:
const rateLimit = require('express-rate-limit');
const limiter = rateLimit({
windowMs: 15 60 1000, // time window (15 minutes)
max: 100, // max requests per window
standardHeaders: 'draft-8', // use the combined RateLimit header (draft-8)
legacyHeaders: false, // disable old X-RateLimit-* headers
});
app.use(limiter); // apply to all routes
In this configuration, standardHeaders: 'draft-8' tells express-rate-limit to emit the new combined RateLimit header (and RateLimit-Policy if your config has a named identifier). Setting legacyHeaders: false removes the old X-RateLimit-* output. If you set standardHeaders: 'draft-6', it will emit the older separate RateLimit-* headers (a precursor format). The README notes: “draft-6: RateLimit-* headers; draft-7 & 8: combined RateLimit header”.
3. Optional identifier: You can also set an identifier option to name the policy (default “global”). For example:
const limiter = rateLimit({
// ... other options ...
identifier: 'api-policy'
});
Then your headers might appear as RateLimit: "api-policy";r=98;t=900 to indicate which quota policy is being used.
Express-rate-limit will automatically send HTTP 429 Too Many Requests when the limit is hit (default status code 429). You can customize that with the message, handler, or statusCode options if desired. But by default, the moment a client exceeds 100 requests in 15 minutes, they get a 429, and in the response headers you’ll see something like:
RateLimit: "global";r=0;t=900
This indicates that no requests are left and the quota resets in 900 seconds. The Retry-After header is also typically set to 900.
With this setup, your Node.js API will now serve IETF-draft-style headers. You can try it locally or in your integration tests to inspect the RateLimit output.
Configuring express-rate-limit's standardHeaders Option
The standardHeaders option controls which draft format to use:
'draft-6': Emits separate headers RateLimit-Limit, RateLimit-Remaining, RateLimit-Reset (an earlier draft format).
'draft-7' or 'draft-8': Emits the single combined RateLimit header (with structured fields). The difference between draft-7 and -8 is minor wording; both produce one RateLimit header.
If you set legacyHeaders: true (the default), Express-rate-limit will also emit the old X-RateLimit-* fields. To fully migrate, set legacyHeaders: false to stop sending them.
By picking 'draft-8' and disabling legacy headers, your API will send only the newer IETF-style fields. If you have existing clients, consider a transition period in which both formats are sent. Either way, express-rate-limit makes the draft format available through two configuration choices.
Migrating From X-RateLimit-* Without Breaking Clients
Moving from custom X-RateLimit-* headers to the new RateLimit format should be done carefully if clients are already using your API. Here are some strategies:
Dual Headers (temporary): For a transition period, you can send both the old and new headers together. For example, leave legacyHeaders: true and also add the new RateLimit header manually (or vice versa). This way old clients see the familiar values and new clients can start reading the RateLimit header. Over time, you can phase out the X- headers.
Versioning: If you use API versioning (URI path, header, etc.), you could introduce RateLimit headers in a new minor version and keep the old version’s behavior unchanged. Document clearly in each version’s spec which headers appear.
Communication: Update your API docs (Swagger/OpenAPI, markdown, etc.) to reflect the new headers. Perhaps put up a deprecation notice on the old headers or announce the change in a developer newsletter. This aligns with Refonte’s curriculum on Error Handling & Logging and Versioning & Deprecation: you’re effectively deprecating the old headers in favor of a standard.
Testing: Be sure to add tests (even automated tests in Postman or your CI) that verify the new headers appear and carry correct values. See the next section for how to test with Postman.
By migrating carefully, you preserve your existing clients’ expectations (the old headers) while giving them time to adapt to RateLimit and RateLimit-Policy. Eventually, the industry may converge fully on the standard format, so aligning early is future-proof.
Testing Rate-Limit Headers in Postman
To verify your rate-limit headers, Postman is a great tool. You can use Postman’s Runner (or a simple collection) to send many rapid requests and watch how the headers change. In Postman:
Check Response Headers: After each request, open the Headers tab in the response pane. You should see RateLimit and RateLimit-Policy (if implemented) as part of the headers list. Verify the values make sense (decreasing r, consistent q, etc.).
Automated Tests: In your Postman request’s Tests script, you can assert header presence. For example:
pm.test("RateLimit header present", function () {
pm.response.to.have.header("RateLimit");
});
Or check values:
const rl = pm.response.headers.get("RateLimit");
pm.test("Remaining less than or equal to limit", () => {
let r = parseInt(rl.match(/r=(\d+)/)[1]);
let q = parseInt(pm.response.headers.get("RateLimit-Policy").match(/q=(\d+)/)[1]);
pm.expect(r).to.be.at.most(q);
});
429 Testing: Use Postman to trigger the 429 condition. The Postman blog “What is API Rate Limiting?” notes that when limits are exceeded, APIs “typically return a 429 Too Many Requests status”. You can watch for 429, check that RateLimit-Remaining (or r=) is 0, and that Retry-After is set. For example:
pm.test("Correct status code", () => {
pm.expect(pm.response.code).to.equal(429);
});
Then assert that Retry-After is present:
pm.test("Retry-After header exists", () => {
pm.response.to.have.header("Retry-After");
});
· Collections & Runner: Put your requests in a Collection and use the Collection Runner (or a CI pipeline with Newman) to fire bursts of calls. This simulates load and ensures your headers change as expected. See Refonte’s guide “How Do You Use Postman in API Testing” for more on using Postman to automate API testing.
By leveraging Postman (with tests and runner), you’ll catch any misconfiguration. For example, the Postman article’s quick reference shows sample rate-limit headers (with X-RateLimit-*) and confirms that the client should “send rapid requests” and verify the response headers. The same idea applies to our new headers.
Documenting Rate-Limit Behavior in Swagger/OpenAPI
When you document your API (e.g. with OpenAPI/Swagger), you should explicitly include the new rate-limit headers in your responses. Here’s how:
Response Headers in OpenAPI: In your OpenAPI spec, add a headers section for relevant responses. For example:
paths:
/items:
get:
description: Returns a list of items.
responses:
'200':
description: OK
headers:
RateLimit:
description: 'The current rate limit status (remaining and reset time).'
schema:
type: string
RateLimit-Policy:
description: 'The configured rate limit policy (total quota and window).'
schema:
type: string
'429':
description: Too Many Requests - quota exceeded.
headers:
Retry-After:
description: 'Seconds to wait before retrying.'
schema:
type: integer
This tells clients (and tools) that these headers may be present.
Components/Schemas (if desired): You could define a component schema for the structured header format (though typically they’re just strings). For clarity, many docs simply describe the header format in text.
OpenAPI 3.2.0 Features: If you are using OpenAPI 3.2.0 (released Sept 19, 2025), you have new fields that can help document advanced API behaviors:
Streaming/SSE support: 3.2.0 adds explicit support for streaming responses (e.g. text/event-stream with itemSchema). This is useful if your API’s rate limits apply differently for, say, a streaming endpoint.
webhooks field: You can document incoming webhooks with a top-level webhooks section.
pathItems component: You can define reusable path item objects to avoid repetition.
additionalOperations: Document non-standard HTTP methods (like COPY, PURGE) under additionalOperations.
These features aren’t specifically about rate-limits, but they show how the latest OpenAPI lets you describe the full shape of your API, including any special behaviors. For example, if you expose a Webhook callback where rate-limiting also applies, 3.2.0’s webhooks support makes documenting that clear.
In short, use Swagger/OpenAPI to explicitly list RateLimit and RateLimit-Policy as response headers, document your 429 error response, and use OpenAPI 3.2’s newer fields when they fit your API design. For related coverage of event-driven documentation, see AsyncAPI vs. OpenAPI: Event-Driven API Documentation.
What OpenAPI 3.2 Adds for This Use Case
OpenAPI 3.2.0 (Sept 2025) introduced features that can make API documentation more expressive. Relevant highlights include first-class support for streaming and SSE content, and new specification fields like webhooks, pathItems, and additionalOperations. In our context:
Streaming & SSE (text/event-stream): The spec now has formal guidance (itemSchema) for sequential media types and SSE. If your API allows streaming queries (e.g. chunked JSON or server-sent events), you can document those streams using the new schema/itemSchema approach. This is a tangential benefit if, say, you rate-limit a long-lived subscription endpoint.
webhooks: Use the top-level webhooks object if your API has callbacks that might themselves be rate-limited.
pathItems and additionalOperations: The pathItems component lets you reuse common path structures, and additionalOperations allows you to describe non-standard methods (like PURGE) on endpoints. If such endpoints have rate-limit headers, you can still document them in the same header section.
These new fields let you give richer documentation about how your API can be called, which complements the description of its limits. They do not change rate limiting itself, but they improve the accuracy of the API contract.
How This Connects to the Deprecation Header (RFC 9745)
It’s instructive to see HTTP header standardization in a broader context. The new RateLimit headers are part of a wave of HTTPAPI standards. For example, RFC 9745 (the Deprecation response header) was published in June 2024. This RFC adds a Deprecation header (with a date timestamp) to indicate that an endpoint is going away. Like RateLimit, the Deprecation header turned a custom practice (many APIs used “Sunset” headers or custom date fields) into a uniform standard. The working group’s goal is consistency across all these cases.
Versioning and Deprecation as a Shared Header Pattern
Refonte Learning’s curriculum explicitly includes “Versioning and Deprecation” as a module. Why? Because managing API evolution is crucial. The Deprecation header allows API owners to tell clients ahead of time when a change is coming, while RateLimit headers allow telling clients about usage quotas. In both cases, we see a pattern: use HTTP headers to convey metadata to clients. Rate-limit headers follow the same philosophy: instead of ad-hoc client tooling, we bake the policy into standard headers.
Thinking in terms of versioning: sending a Deprecation: <timestamp> or a structured rate-limit header are related tasks. Both require careful communication with clients, updating documentation, and possibly code branches. (In fact, the rate-limit draft and the deprecation draft share editors from HTTPAPI, so the design approach is consciously parallel.)
Common Mistakes Implementing Rate-Limit Headers
Even with a standard, there are pitfalls. Here are common mistakes and how to avoid them:
Misnaming Headers: Be precise: RateLimit and RateLimit-Policy (note no X-, correct case-insensitive spelling) must be used exactly as defined. Sending Rate-Limit (with a dash) or an abbreviated variant will confuse clients.
Incorrect Structured Syntax: The values for these headers follow RFC 8941 Item-list syntax. Forgetting the quotes around policy names or using commas incorrectly can make them unparsable. Example: use "policyName" not just policyName.
Missing Values: Always send both headers (Policy and RateLimit) on successful requests so clients know the policy rules. If you omit RateLimit-Policy, the client won’t know the total quota. If you omit RateLimit, the client won’t know current usage.
Timezone/Units Confusion: The draft uses seconds for windows and reset times (w= and t=). Don’t accidentally use milliseconds or an epoch. Double-check your math (e.g. resetSeconds = Math.floor(windowMs/1000)).
Not Updating Documentation: If you switch formats, update your OpenAPI specs, README, etc. Forgetting to document the new headers leads to confusion. Also, make sure to note deprecations of the old headers if you’re phasing them out.
Ignoring 429 Semantics: Remember that header standardization doesn’t change the fact that exceeding limits should return 429 (Too Many Requests). Some developers might omit setting the status code, but always return 429 for hard limits. (Network intermediaries and clients expect 429 for retries.)
Overlooking Problem Responses: If you use the new problem types (quota-exceeded, etc.), ensure your JSON error body follows RFC 7807 (“problem+json”). Don’t just send the URI as a string; use the proper keys.
Server vs. Client Time: If your API is consumed globally, ensure the reset time is unambiguous (the spec uses seconds remaining, not epoch) and that clients aren’t misinterpreting it as local time.
By carefully following the draft’s rules and updating all parts of your API (code, docs, tests), you’ll avoid these mistakes. Always test edge cases: for instance, what happens in a redirect (3xx)? The draft even notes issues: low quota should not prevent a redirect. And if you ever see a RateLimit header you sent being ignored or mangled by proxies, confirm it’s allowed by your infrastructure (some rate-limit headers were historically dropped by CDNs until clarified).
API Developer Skills and Salaries in 2026
Becoming proficient in APIs is not just technically rewarding; it is marketable. The Refonte Learning APIs Developer program is built around the full skill set needed to handle issues like rate limits, and the earning potential reflects that. Refonte’s marketing materials advertise “APIs Developer: $70.5K+ starting, $210K+ (Jobs annually).” The “$70.5K+ starting” figure comes from the program itself and represents its internal marketing and placement goals.
For comparison, independent data show higher averages:
Glassdoor’s 2026 data report a median total pay of about $134K/yr for “API Developer” roles. (That includes salary + bonus, with typical ranges from roughly $107K to $169K.)
ZipRecruiter’s Aug 2026 figures put the average around $124,567/yr for API Developers nationwide. They note typical salaries range $113K (25th percentile) to $140K (75th percentile), with top earners reaching ~$153K.
These figures indicate that the market values API development skills highly. The program’s stated outcomes, including roles such as API Developer, Backend Developer, and Integration Specialist, align with those salaries.
Of course, salary also depends on location, experience, and specific tech stacks. But the key takeaway: API developers command six-figure salaries in 2026 (the program’s $70K+ baseline is a conservative entry point). Earning that level usually requires both core skills (REST, GraphQL, databases, security) and specialization (e.g. knowing how to implement robust rate limiting, proper logging, API gateways, etc.).
Building This Skill Set: The Refonte Learning APIs Developer Program
If this deep dive into rate-limit headers piqued your interest, note that many of these concepts are covered by our Refonte Learning APIs Developer curriculum. This 3-month, 10–12 hours/week program covers:
Curriculum Highlights: REST API development fundamentals; GraphQL design; Authentication & Authorization; Database integration; API Documentation & Testing; Error Handling & Logging; Versioning & Deprecation; Microservices architecture; Performance optimization; API security best practices.
Tools Taught: You’ll work with Node.js frameworks, Postman for testing, Swagger/OpenAPI for docs, and GraphQL libraries (among others).
Mentorship: The course is led by Sophia Johnson, MSc, a seasoned API expert with 10+ years of experience in backend systems design. Her background spans startups to enterprise, working with both REST and GraphQL.
Projects & Outcomes: Students build real-world API projects, learning to handle exactly the issues we discussed (rate limiting, error responses, versioning, etc.). Top performers can earn internship letters of recommendation and prizes.
Career Path: Graduates typically move into roles like API Developer, Backend Developer, Fullstack Developer, Integration Specialist. The program advertises a starting salary of ~$70.5K, and given market data, you can expect to grow beyond that as you gain experience.
In short, Refonte’s APIs program equips you with the knowledge to design and implement standards-compliant APIs. While we didn’t teach the IETF RateLimit draft by name (it’s very new!), our modules on error handling and versioning give you the engineering judgment to adopt such best practices. By the end, you’ll know when to send HTTP headers like RateLimit-Policy or Deprecation and how to communicate limits to clients.
For more details or to enroll, see the Refonte Learning APIs Developer Program. It’s your launchpad for a modern API career in 2026 and beyond.